October 14, 2026
|
5 min read


احصل على وصول فوري إلى بيئة TrueFoundry مباشرة. انشر النماذج، ووجّه حركة مرور LLM، واستكشف المنصة بالكامل — بيئة الاختبار الخاصة بك جاهزة في ثوانٍ، ولا يلزم وجود بطاقة ائتمان.


Published: October 14, 2026

Blazingly fast way to build, track and deploy your models!
Search for Gloo AI Gateway today and solo.io sends you somewhere else: the old product page at solo.io/products/gloo-ai-gateway redirects to agentgateway. Behind the redirect, Solo moved its AI gateway features off Envoy and onto a new proxy built for MCP and agent traffic.
That much is in Solo's announcements. We wanted to know what the gateway actually does, so we ran it ourselves and checked the behaviours that matter in production, with version numbers wherever a result depends on them. If you're comparing Solo against the wider field, our roundup of Solo.io competitors and alternatives covers that ground. This post stays on the gateway itself.
Solo's AI gateway features used to run on Gloo Gateway, Solo's Envoy-based API gateway. Solo donated the open-source Gloo Gateway to the CNCF, where it was renamed kgateway and accepted as a Sandbox project in March 2025. That same month Solo created a new proxy from scratch in Rust: the agentgateway repository dates from 18 March 2025.
The handover took about eight months, across two kgateway releases, one Solo announcement and a move to a foundation:
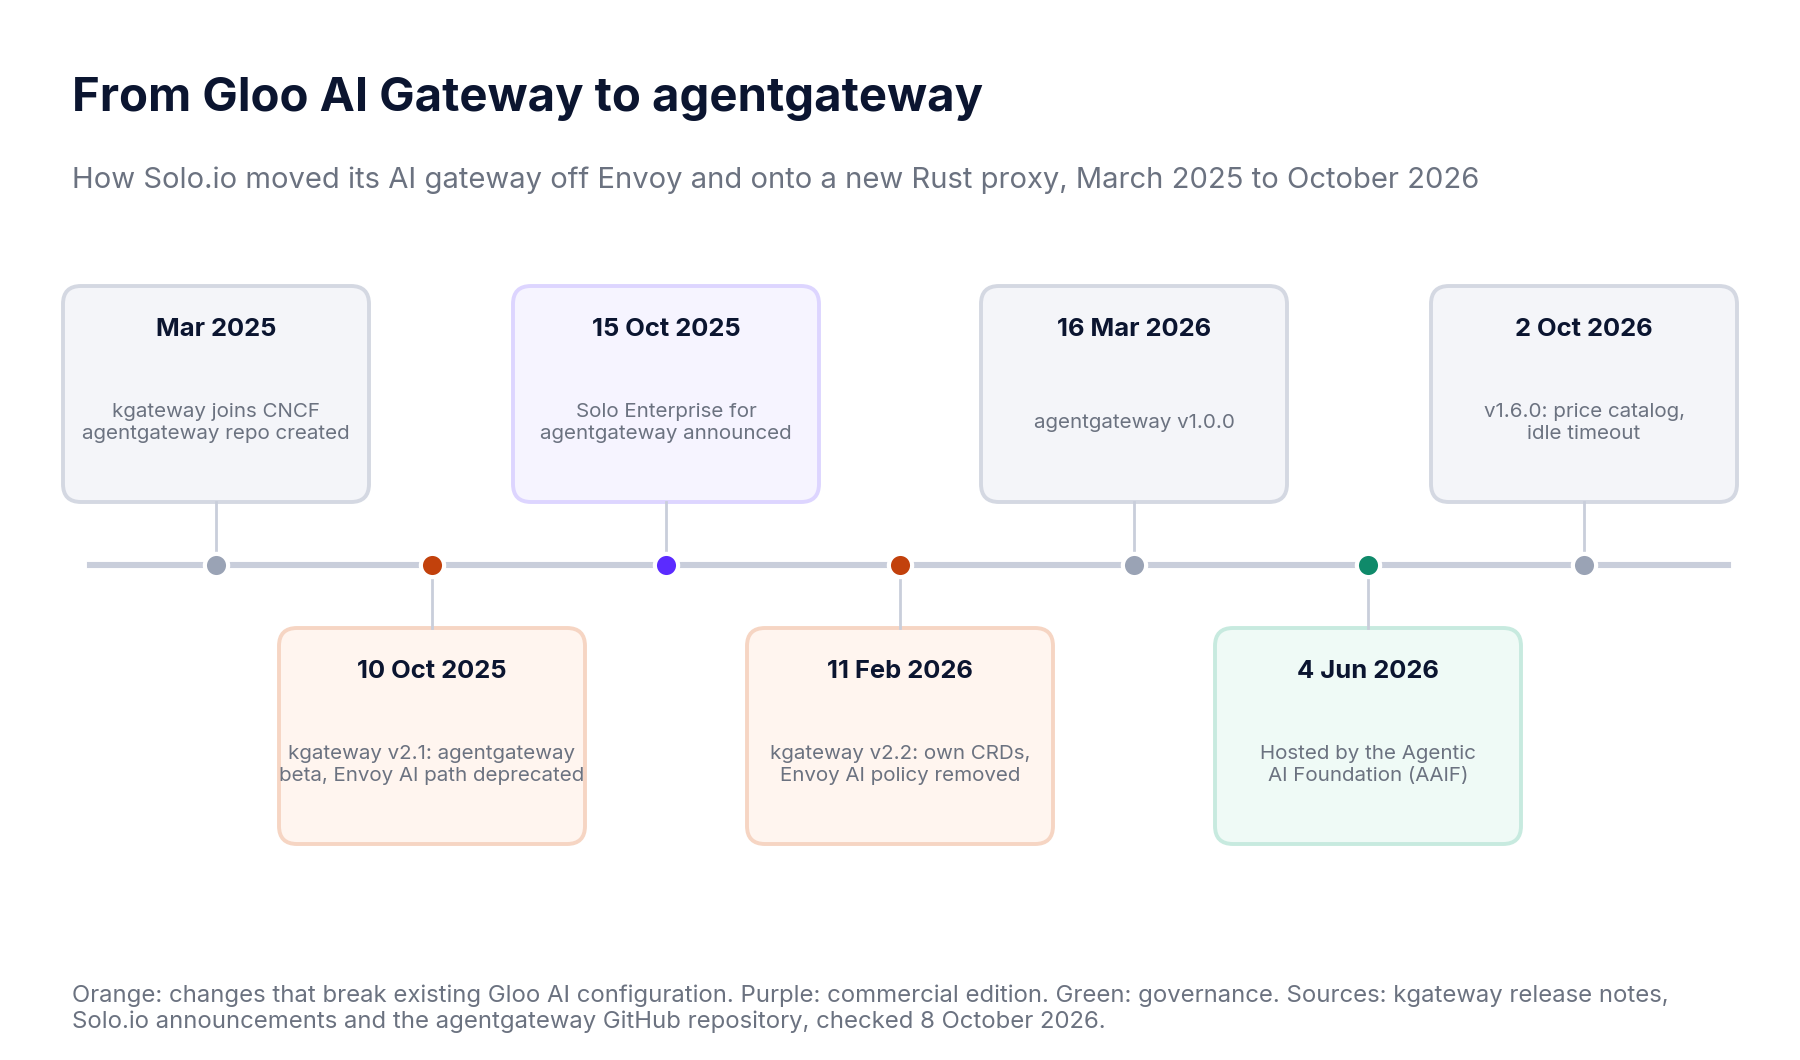
On the commercial side, Gloo Gateway was renamed Solo Enterprise for kgateway, and Solo Enterprise for agentgateway, once included in Gloo Gateway, became a separate product with its own Helm charts, controllers and APIs.
Existing configuration doesn't carry over unchanged. kgateway v2.2 required migrating agentgateway settings to the new resources before upgrading, and the Solo Enterprise 2.1 rename removed "Gloo" from CRDs and Helm charts.
agentgateway is an open source AI gateway, self-hosted, that sits between your applications and the model providers, tools and agents they call. Applications talk to it with the standard OpenAI request format, so adopting it is mostly a base-URL change. It governs three kinds of traffic: LLM calls, Model Context Protocol (MCP) traffic between agents and tools, and agent-to-agent (A2A) calls. (For why A2A traffic needs its own controls, see our post on governing multi-agent A2A traffic at the gateway.) It also proxies ordinary HTTP and gRPC. (What is an LLM gateway? covers the general pattern.) For the wider category, see our guide to agent gateways.
Solo's docs explain the rewrite: MCP sessions are long-lived and stateful, and traditional gateways were not designed for that kind of session awareness, so Solo built a new proxy instead of extending Envoy.
Minor releases ship roughly monthly, which means regular upgrade work. v1.6.0 alone had five breaking changes, and two of them are in the migration checklist below.
We ran the open-source standalone binary, v1.5.0, against local mock providers, plus a few real OpenAI calls where the provider itself was under test. When v1.6.0 shipped, we re-ran the four findings it was most likely to change on both versions. We haven't run the commercial edition, which needs a sales-issued licence key, so what we say about it comes from Solo's documentation.
There are two ways to run it.
Standalone, it's one process reading one YAML file. It needs no Kubernetes, Postgres or Redis to route LLM traffic, and it includes a web UI and an embedded SQLite request log. A minimal LLM configuration is under ten lines, with no account to create.
On Kubernetes, a controller watches Gateway API resources and pushes configuration to separate proxy deployments over xDS. agentgateway has its own GatewayClass and CRDs (AgentgatewayPolicy, AgentgatewayBackend, AgentgatewayParameters). Solo's optional Helm values for ClickHouse, Redis and OpenTelemetry are outside its support policy.
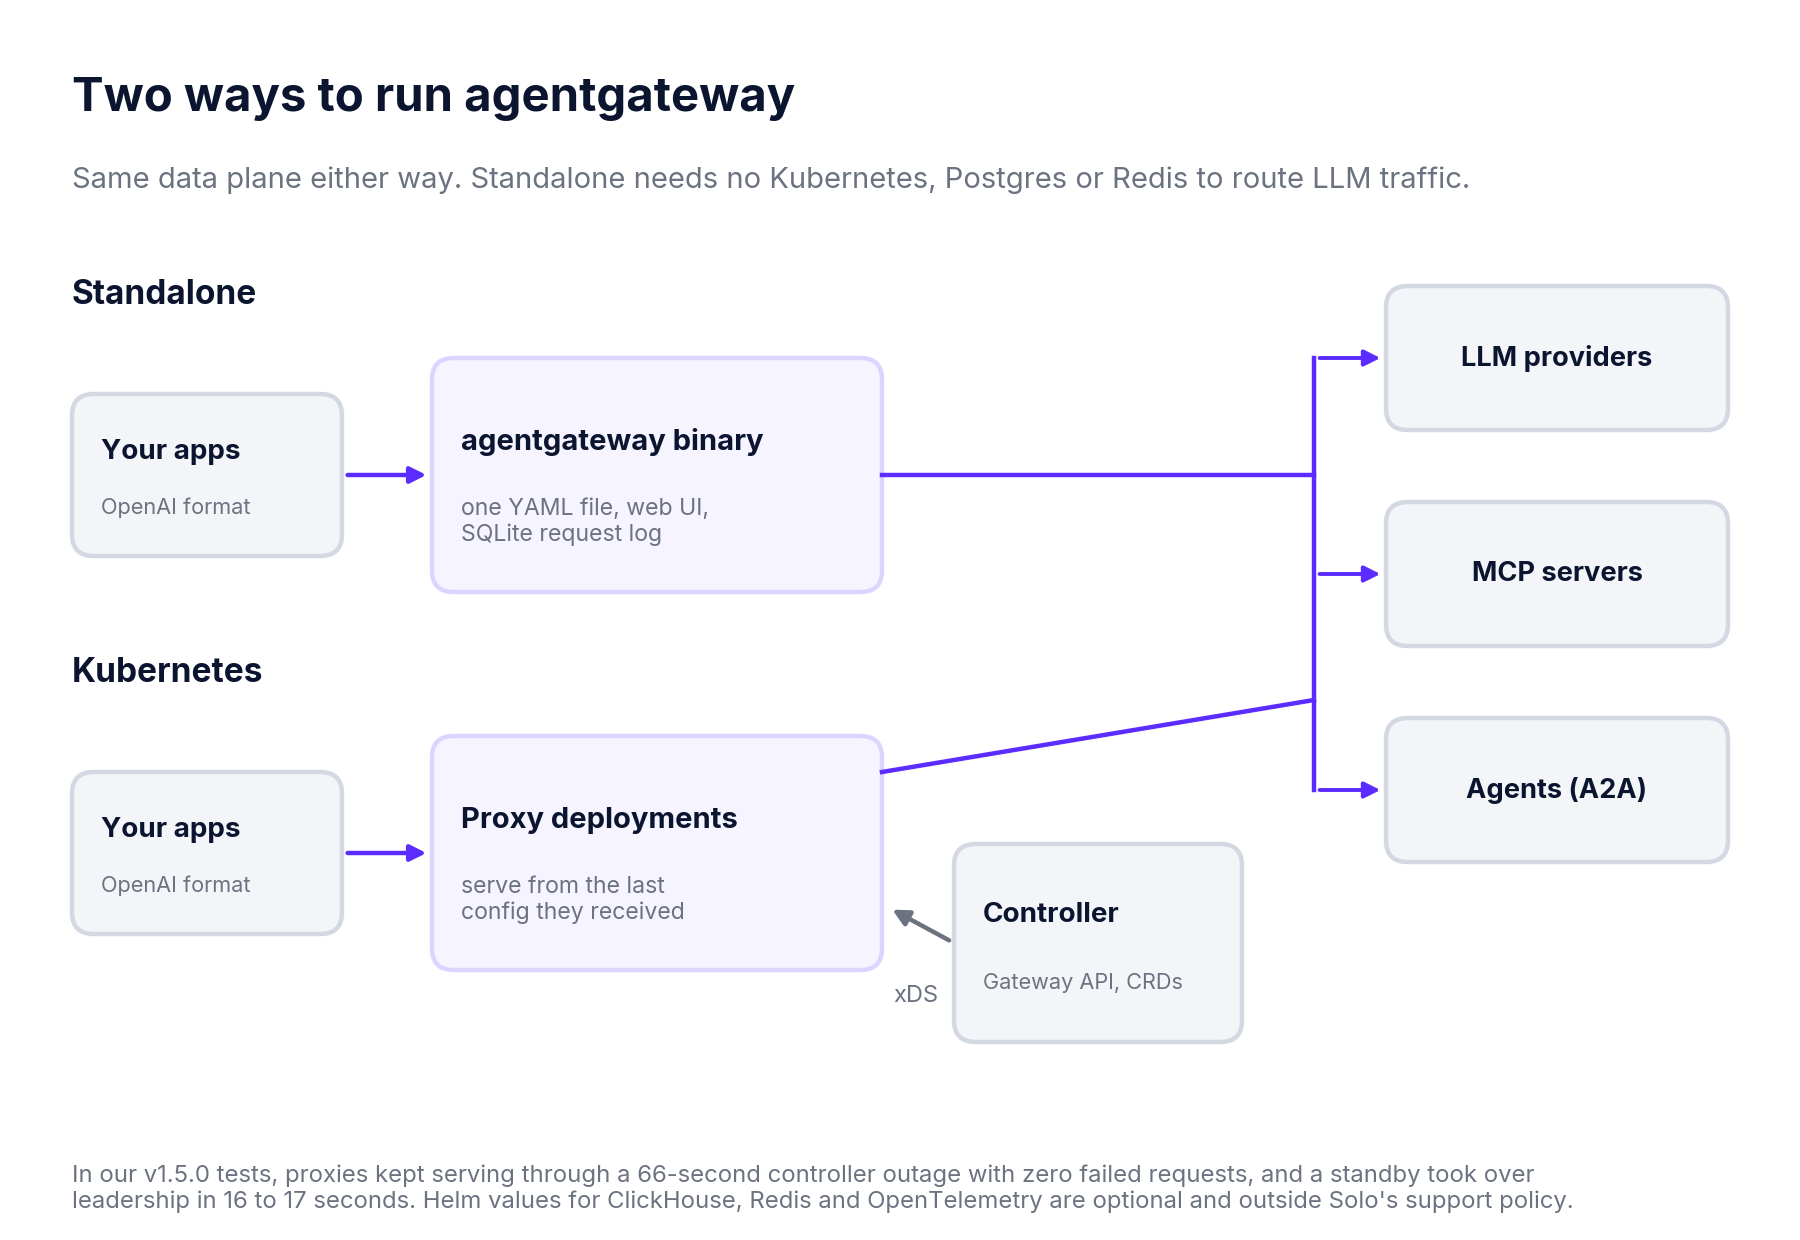
Figure 2: Standalone and Kubernetes deployments share one data plane and the same upstreams.
What we checked hands-on on v1.5.0:
The v1.6.0 schema has seven built-in provider types (OpenAI, Gemini, Vertex AI, Anthropic, Amazon Bedrock, Azure and GitHub Copilot) and 14 presets, including Groq, Mistral, DeepSeek, Together AI, Ollama and OpenRouter. A custom provider type reaches any other host that speaks one of the nine supported API formats, so in practice the reach is any OpenAI-compatible endpoint.
Passthrough fidelity was excellent in our tests. We sent tool calls, strict JSON-schema structured outputs, system prompts, image inputs, logprobs and seeded requests both directly to OpenAI and through the gateway, and the results matched. A separate check for "silent breaks", where a request returns HTTP 200 with empty or wrong content, found none across the capabilities we tested.
Image generation and audio are the gap. The LLM-aware path doesn't recognise image generation, transcription or speech requests. You can still proxy that traffic as plain HTTP, and we confirmed it arrives intact with API-key checks applied, but with no token accounting, cost tracking or model-aware policy.
agentgateway supports weighted routing, priority-based failover, conditional routing, retries, timeouts, outlier eviction, mirroring and session affinity. Failover works across providers with different API formats: we failed a chat-completions backend over to an Anthropic-format backend, and the client kept receiving responses in the shape it asked for.
Three behaviours need deliberate configuration.
Retries make one more upstream call than the schema describes (v1.5.0 and v1.6.0). The schema describes attempts as the "total number of attempts, including the original request." In our tests, attempts: 1, 2 and 3 produced 2, 3 and 4 backend calls. The gateway's own retry.attempt log field counts the same way, so the behaviour is consistent and only the documentation disagrees. Retries also have no backoff unless you configure one. Plan for one extra call per failure, and set a backoff.
Failover needed health checks in v1.5.0, and v1.6.0 fixes this. In v1.5.0, failover didn't move traffic off a failing primary unless an eviction policy was configured. On v1.6.0 with no health policy, the primary was evicted after one failure and the next five requests went to the backup. On both versions, the request that hit the failure still reached the client as an error and wasn't retried on the backup.
Stalled streams need an explicit timeout. In v1.5.0, neither requestTimeout nor backendRequestTimeout ended a stream that sent its first chunk and then went silent. v1.6.0 adds responseIdleTimeout, and set to 5 seconds, it cut our stalled stream at 5.04 seconds. The client has already received a 200 and the first chunk by then, so it sees a truncated stream, not an error code. With no timeout configured, the stream still hangs on v1.6.0 for as long as the client waits. This is the route policy we tested:
TrueFoundry AI Gateway delivers ~3–4 ms latency, handles 350+ RPS on 1 vCPU, scales horizontally with ease, and is production-ready, while LiteLLM suffers from high latency, struggles beyond moderate RPS, lacks built-in scaling, and is best for light or prototype workloads.



Solo.io's AI gateway is now agentgateway, an open-source project under the Agentic AI Foundation, with Solo Enterprise for agentgateway as the paid edition. The old Gloo AI Gateway page on solo.io now redirects to agentgateway.
Gloo Gateway was Solo's Envoy-based API gateway. Solo donated the open-source version to the CNCF, where it became kgateway in March 2025. agentgateway is a separate proxy written in Rust that Solo started the same month, and it replaced the Envoy-based AI features: kgateway v2.1 deprecated them and v2.2 removed them. On the commercial side, Gloo Gateway was renamed Solo Enterprise for kgateway, and Solo Enterprise for agentgateway is its own product.
agentgateway is free and Apache 2.0 licensed, and the open-source build includes per-key budgets, local rate limits, PII masking, MCP tool authorization and a request log. Solo doesn't publish enterprise pricing. Licences come through sales, and the only outside figure we found, Vendr's median Solo.io contract of $68,000 a year, covers all of Solo.io's products.
They share the same data plane. The enterprise edition adds on-behalf-of identity, global rate limiting, a budget resource and Cost Management UI, FIPS and long-term-support builds, and a support contract, and it needs a licence key from Solo's sales team.
Yes, and it's the product's strongest area. It federates several MCP servers behind one endpoint, supports stdio and streamable HTTP transports, can expose OpenAPI services as MCP tools, and authorizes access per tool with CEL rules, including filtering the tool list per caller.
نعم. تعمل TrueFoundry في VPC الخاصة بك أو محلياً أو في بيئة معزولة عن الشبكة أو هجينة، فلا تغادر التعليمات والردود نطاقك أبداً حتى وأنت توجّه الطلبات عبر مزوّدين كثيرين.
TrueFoundry's SaaS maintains SOC 2 Type II, GDPR and HIPAA programs, and reports are available at trust.truefoundry.com. TrueFoundry's documentation says these certifications apply to its managed infrastructure. For self-hosted deployments, compliance depends on your own infrastructure and controls. RBAC, SSO and audit logging are built in.



أحدث الأخبار والمقالات والموارد تصلك مباشرة إلى بريدك الوارد