September 24, 2026
|
5 min read


Published: September 24, 2026
Blazingly fast way to build, track and deploy your models!
Enterprise teams compare Obot AI vs LiteLLM when their AI stack starts to outgrow direct model calls. LiteLLM is usually the familiar choice for multi-model routing, virtual keys, spend tracking, budgets, and OpenAI-compatible access. Obot AI enters the discussion when MCP server management, AI client visibility, identity, and tool governance become important.
The real question is not whether one tool replaces the other in every case. LiteLLM starts from the LLM proxy layer. Obot AI starts closer to MCP governance and enterprise AI ecosystem management. A team that already runs LiteLLM without pain has no routing reason to leave. A team drowning in unmanaged MCP servers on developer laptops has no routing reason to stay.
TrueFoundry becomes relevant when teams need model routing, MCP tools, agent workflows, budgets, guardrails, and audit logs governed together, which is usually the point at which two open-source gateways start to feel like two separate compliance projects.
A useful LiteLLM vs Obot AI comparison starts with migration intent. Some teams want to replace a proxy server. Others want to add MCP governance around agents, coding tools, and internal AI clients. These represent different buying motions.
The core difference is where each project's opinion begins. LiteLLM configuration primarily describes models and the rules for reaching them. Obot's catalog starts with MCP servers and policies defining who can reach them. Both projects have since expanded into each other's territory.
LiteLLM now provides one single API across 140+ integrations, along with budgets, routing, guardrails, and usage tracking. Its LLM gateway architecture use case remains a natural setting for comparing model-aware routing with a general proxy approach. LiteLLM itself now positions its product as an AI Gateway spanning LLM, MCP, and agent traffic.
Both gateways have a free, open-source entry point, so the software price alone does not provide a complete comparison. The ownership cost also includes infrastructure, observability, identity, upgrades, and gateway operations.
LiteLLM's OSS tier covers 140+ providers, users, teams, budgets, rate limiting, fallbacks, request logging, and Prometheus metrics. Enterprise pricing scales by annual gateway request capacity, deployment architecture, and support requirements. Enterprise adds SSO, SCIM, OIDC or JWT authentication, audit logs, secret managers, multi-region support, and service SLAs.
That makes LiteLLM easier to evaluate when teams already understand expected request volume. TrueFoundry's LiteLLM pricing analysis provides additional context around infrastructure and enterprise TCO.
Obot also has a free path. Its current edition model supports up to 100 users and devices by default. Community retains those limits while adding identity options such as Microsoft Entra, Okta, JumpCloud, and Auth0. Enterprise removes those limits and adds formal support.
The comparison should therefore include hosting, databases, observability storage, key management, compliance requirements, and engineering effort. LiteLLM requires PostgreSQL for features such as virtual keys. Obot requires infrastructure for the gateway and hosted MCP workloads.
Not completely. Obot supports meaningful model access, although LiteLLM remains more deeply focused on cross-provider routing.
LiteLLM provides a unified interface for many LLM providers. Applications use a gateway base URL, a key, and a configured model name. Routing can distribute traffic across providers, regions, and credentials while applying fallback and cost control.
Obot's LLM Gateway follows a different model. It exposes provider-compatible endpoints for OpenAI and Anthropic models, Generic Responses endpoints, AWS Bedrock, and Azure. An Obot API key with LLM proxy scope replaces direct provider credentials.
Administrators then apply Model Access Policies to control which models each end user can see and call. The returned model list contains only approved choices. The gateway keeps upstream credentials within Obot rather than distributing them across applications.
Obot can also configure Google Vertex as a provider elsewhere in the platform. However, current external provider-specific gateway routes do not expose Google Vertex.
LiteLLM remains the stronger starting point when cross-provider fallback and request routing drive the decision. Obot is stronger when enterprise governance around users, agents, models, and MCP systems matters more.
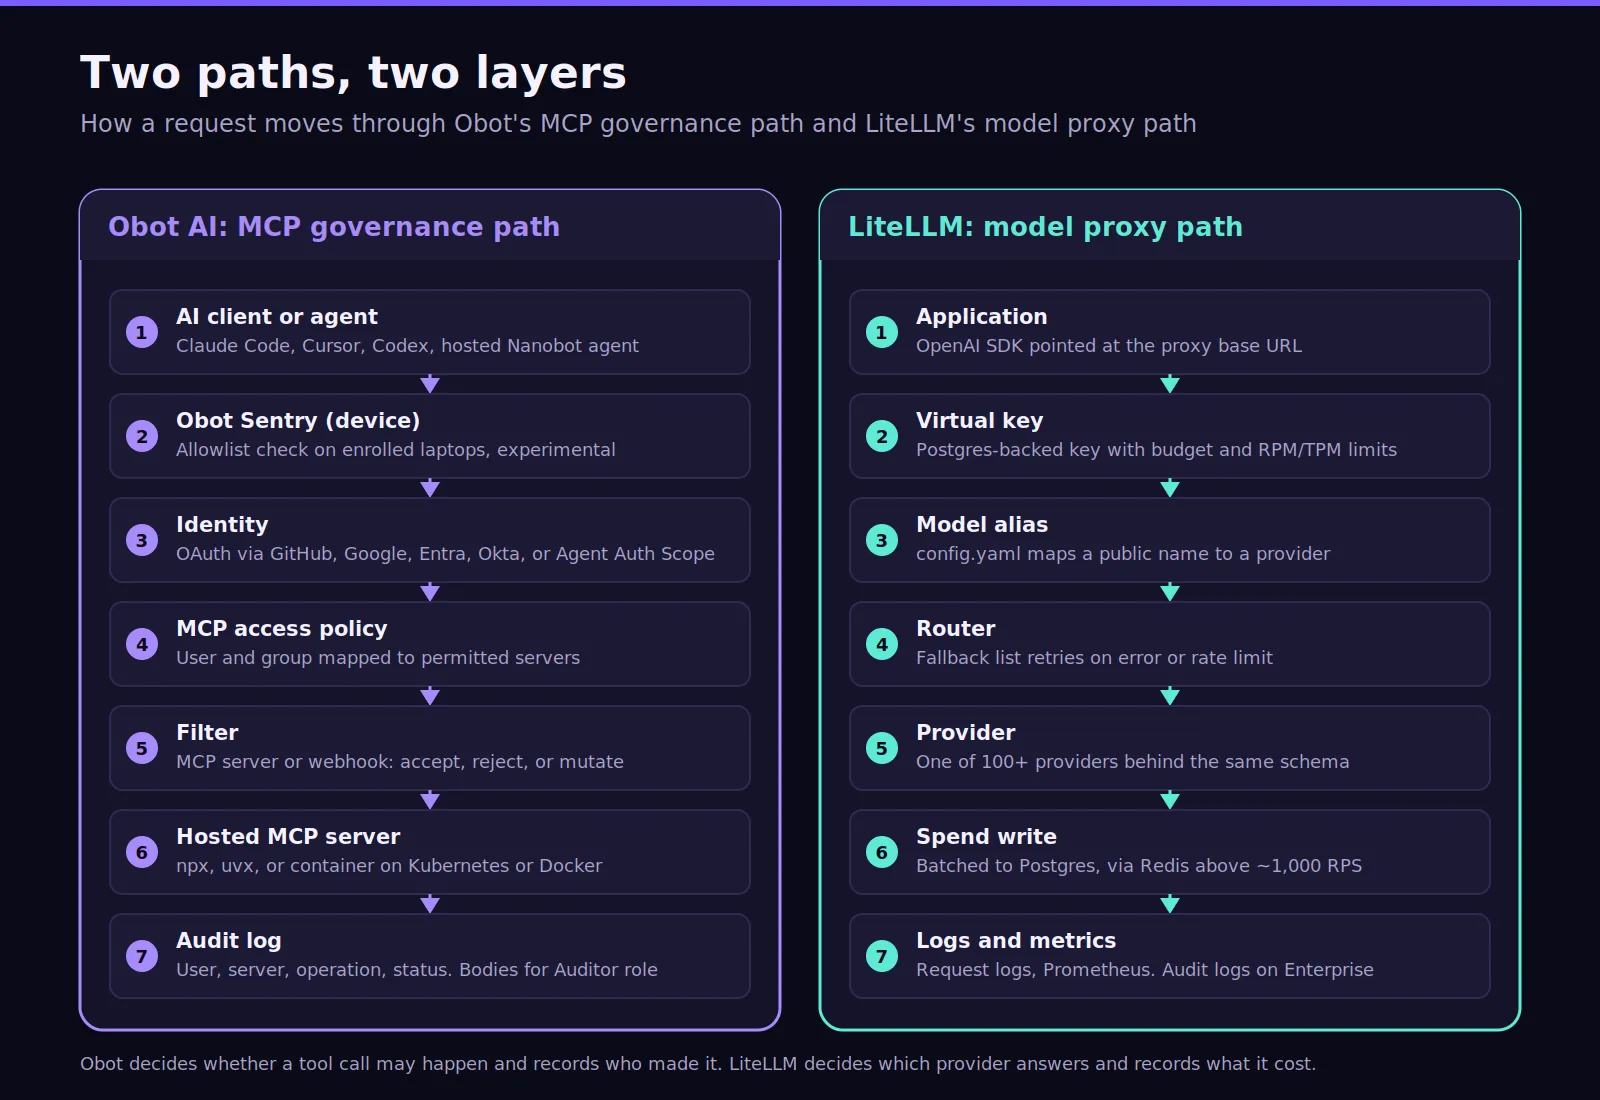
LiteLLM is strongest when applications primarily generate LLM traffic. The decision changes when an AI agent begins to call tools, retrieve sensitive data, or act across enterprise systems. Model routing then becomes one layer of control.
LiteLLM deserves credit here because its current capabilities are broader than older comparisons suggest. Its MCP layer presents a fixed endpoint for registered servers. Clients authenticate using the same gateway credential model, while access can be assigned by key or team.
The LiteLLM gateway also separates client authentication from upstream OAuth flows. This allows the gateway credential to remain distinct from server-side OAuth credentials. Coding tools such as Claude Code can connect to both LiteLLM model routing and MCP endpoints.
Obot goes further into MCP operations. Its MCP Gateway comparison point is hosting and policy depth. Obot can run npx, uvx, containerized, and remote MCP workloads while enforcing authentication and authorization.
Obot's access policies map approved servers to specific users or identity-provider groups. Filters can inspect individual tool calls, then accept, reject, or modify requests before they proceed. Custom filters can support controls such as PII masking when required.
Obot Sentry also extends governance toward local AI tools. Device Management can inventory activity from Claude Code, Codex, Cursor, and VS Code. This creates deeper integration when local developer activity must appear alongside gateway events.
Observability is another practical split in LiteLLM and Obot AI. Each platform sees the layer it primarily governs.
LiteLLM tracks spend, budgets, usage by key or team, request behavior, provider results, and gateway activity. It can attribute token usage across keys, users, teams, organizations, tools, agents, and MCP workloads.
Obot focuses more on MCP requests, local client activity, model calls, devices, and platform governance. Its audit system correlates activity across MCP servers, model providers, hosted workloads, and user devices. Administrators can filter activity by user, server, tool, provider, model, client, device, or session.
For platform teams, the difference is important. Model observability answers which model was called and what it cost. MCP observability answers which identity reached which tool and what happened afterward.
TrueFoundry's gateway observability analysis explains how model latency, errors, spending, policies, and traces can be correlated at the gateway layer.
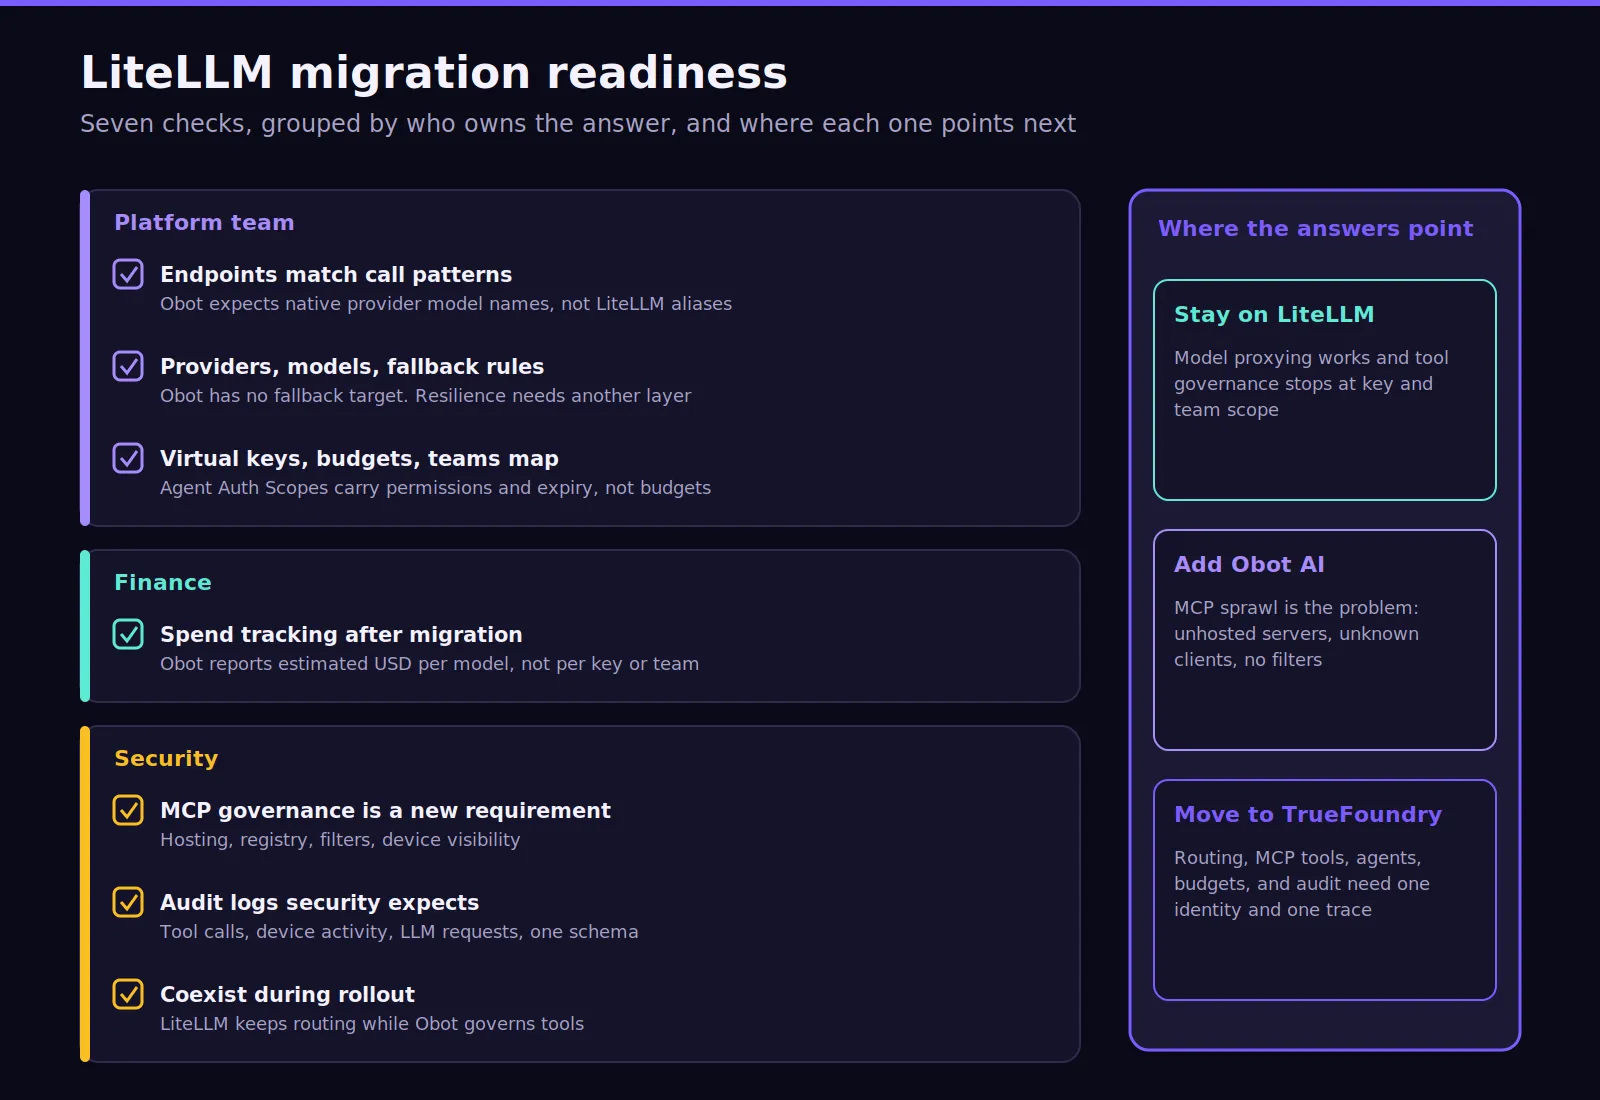
Migrating a proxy is rarely the hardest part. The challenge is migrating assumptions that are already embedded in application code. Before moving, teams should check:
Three items need particular attention. LiteLLM applications may use public aliases, while Obot expects provider-native names for supported gateway routes. That means model identifiers can become migration work across production applications.
LiteLLM also carries fallback behavior that does not map directly to Obot's model-access model. Environment variables that hold provider settings and credentials may require updates as responsibility shifts between gateways.
The key models differ as well. LiteLLM uses gateway credentials carrying budgets and access. Obot can issue scoped credentials through the Obot API, while an Obot token can authenticate supported client workflows. These permission models do not map one-to-one.
Teams may therefore keep LiteLLM for models while adding Obot for MCP. Another option appears when agentic workflows require policies across both layers. TrueFoundry's Agent Gateway provides workflow quotas, traces, and centralized identity for autonomous agents.
TrueFoundry serves as the enterprise consolidation layer. Its enterprise AI gateway provides routing, observability, guardrails, budgets, policy enforcement, and model governance. It can run through SaaS or customer-controlled deployment patterns.
The platform supports provider routing, fallback, rate limiting, and cost visibility across more than 1,600 models. Policies can also live as YAML, allowing teams to review governance through version control rather than maintaining controls independently inside applications.
Budget policies can scope usage to users, teams, applications, models, or environments. This provides real time enforcement before expensive LLM calls continue.
name: budget-limiting-configtype: gateway-budget-configrules: - id: 'coding-agents-daily' when: subjects: ['team:platform'] metadata: environment: 'production' limit_to: 200 unit: cost_per_day budget_applies_per: ['user'] alerts: thresholds: [75, 90, 100] notification_target: - type: slack-bot notification_channel: 'budget-alerts-channel' channels: ['#ai-spend']Cross $200 for the day, and the gateway answers with a 429 carrying `error_origin_level: rate_limit_budget`, with the violated rule ID in the `x-tfy-applied-rules` header. Audit mode tracks the same rule without blocking, which is the safe way to introduce a cap on a team that has never had one.
The MCP Gateway governs tool access through a central registry, per-server RBAC, OAuth 2.0 token management with automatic refresh, and Virtual MCP Servers that expose a curated subset of tools from multiple servers as a single endpoint without requiring a new deployment. Guardrails attach to MCP tool calls in the same policy file that governs LLM calls:
name: guardrails-controltype: gateway-guardrails-configrules: - id: github-tools-pii when: target: operator: or conditions: mcpServers: values: - github-mcp condition: in subjects: operator: and conditions: in: - team:platform llm_input_guardrails: [] llm_output_guardrails: [] mcp_tool_pre_invoke_guardrails: - pii/pii-detection mcp_tool_post_invoke_guardrails: []The MCP layer connects model governance with tool access rather than treating tools as another application concern. Federated identity, RBAC, OAuth 2.0, observability, and server registration support enterprise MCP workloads.
TrueFoundry is therefore a single-platform option when separate proxy and MCP products create duplicate policies. Teams can also compare this architecture directly through the TrueFoundry vs LiteLLM comparison.
Choose TrueFoundry when:
TrueFoundry currently lists Developer at $0 monthly, Pro at $499 monthly, Pro Plus at $2,999 monthly, and custom Enterprise pricing. Enterprise supports VPC and air-gapped gateway and control-plane deployments
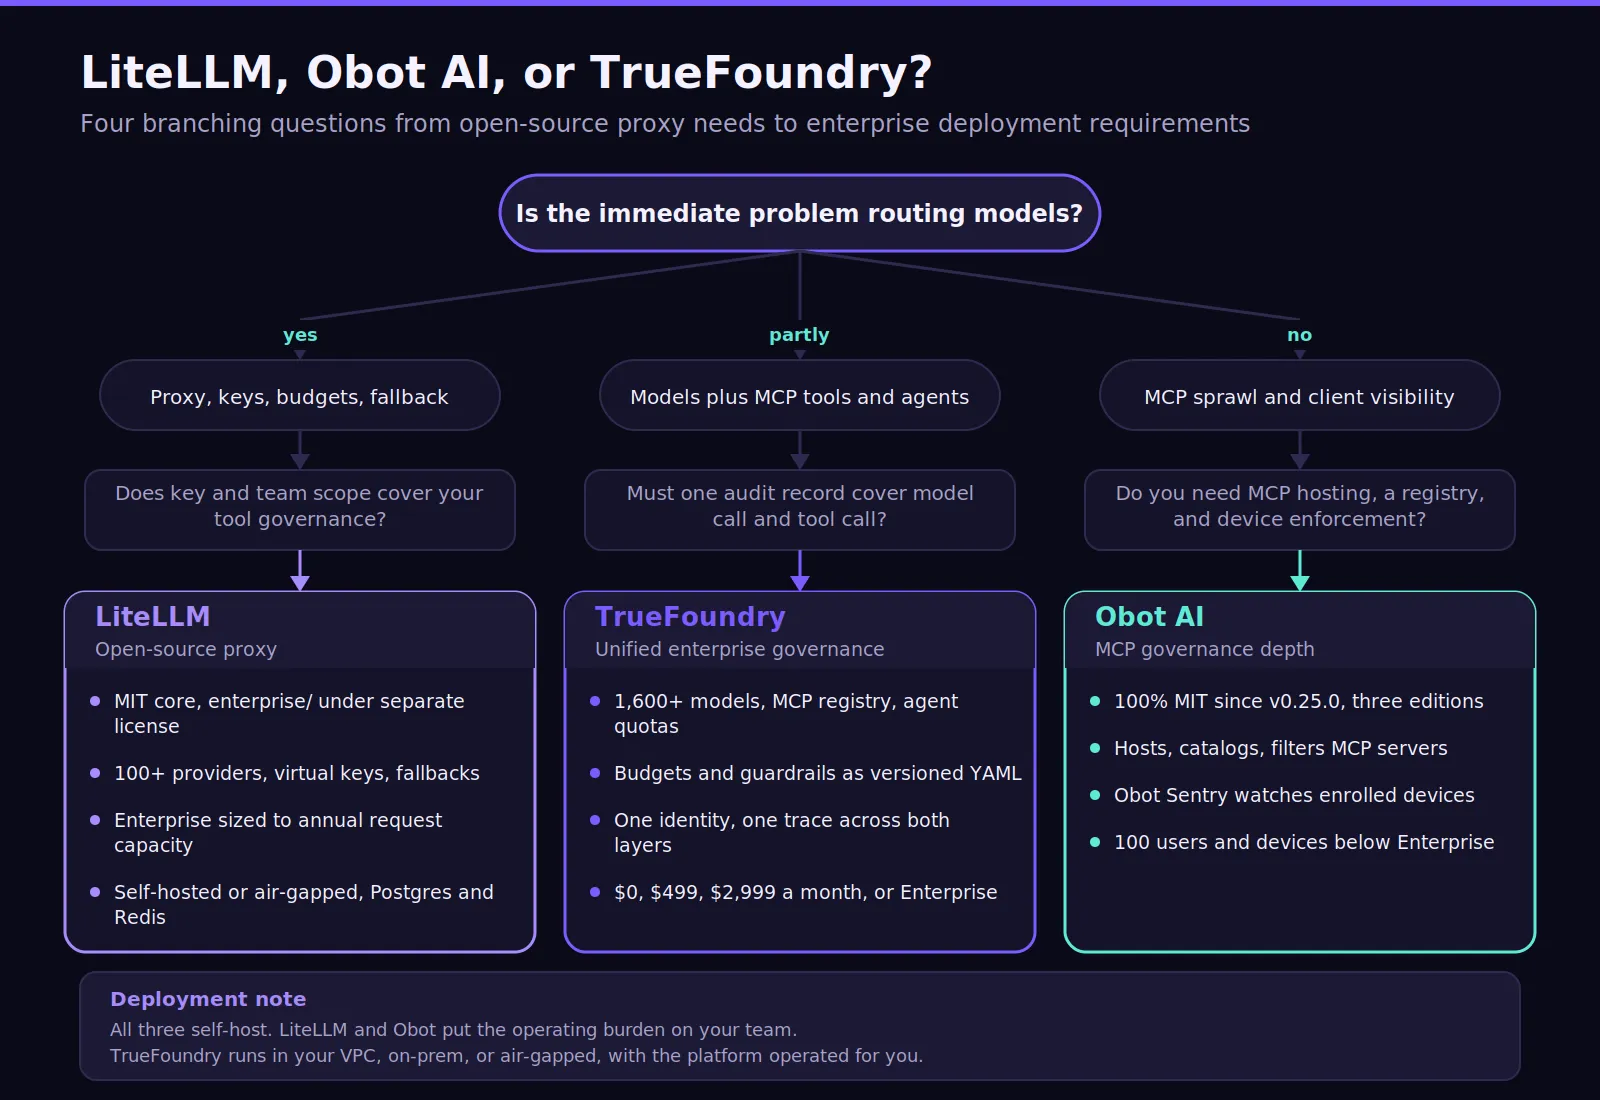
Choose LiteLLM when the immediate requirement is model access, provider routing, budgets, fallbacks, and spend tracking. It remains a strong candidate when production workloads primarily need a model-aware gateway.
Choose Obot AI when MCP governance, AI client visibility, server hosting, model-access policies, and identity-aware controls drive the decision. It fits teams dealing with MCP sprawl and unmanaged developer tool connections.
Choose TrueFoundry when models, tools, agents, budgets, guardrails, and observability require a single governance architecture. This approach provides full control across multiple AI layers without maintaining separate policy systems.
The Obot AI or LiteLLM decision is therefore a choice of starting layer. The right answer depends on whether model routing or MCP governance is the immediate operational constraint.
Teams considering another API gateway path, such as Kong Gateway or Kong AI Gateway, should evaluate that category separately. Those platforms begin from broader AI traffic and API management concerns.
Book a free demo today to see how TrueFoundry connects model, MCP, and agent governance across production environments.
TrueFoundry AI Gateway delivers ~3–4 ms latency, handles 350+ RPS on 1 vCPU, scales horizontally with ease, and is production-ready, while LiteLLM suffers from high latency, struggles beyond moderate RPS, lacks built-in scaling, and is best for light or prototype workloads.




The main difference in Obot AI vs LiteLLM is where each platform starts. LiteLLM is model-proxy first, with routing, budgets, provider access, and spend controls. Obot is MCP-governance first, with hosting, server policies, local client visibility, and tool controls. Both now extend beyond those original boundaries, although their strongest capabilities still reflect their starting architectures.
Obot can provide model access through provider-compatible endpoints, although it does not replicate LiteLLM's routing depth. LiteLLM supports cross-provider load balancing and fallback across many model providers. Obot focuses on user-specific model permissions and protected provider credentials. Teams relying on routing resilience should therefore retain LiteLLM or introduce another model-routing layer.
LiteLLM currently offers broader provider coverage. Its public product information lists more than 140 provider integrations. Obot's external gateway supports routes for OpenAI, Anthropic, Generic Responses Compatible, Amazon Bedrock, and Azure. Obot can configure additional providers elsewhere in the platform, although not all providers are exposed through its external gateway endpoints.
Both products have open-source foundations. LiteLLM offers a free self-hosted OSS gateway, while selected enterprise features require an Enterprise licence. Obot's current edition model also provides a free entry path and Community edition, with Enterprise removing user and device limits. Buyers should compare licensing alongside support, authentication, security, and operational requirements.
Only partly. Both support provider-compatible interfaces, although their configuration and model naming differ. LiteLLM applications may depend on aliases, routing, API keys, and fallback behavior that do not map directly to Obot. Teams should inventory each model reference, credential, routing policy, and MCP dependency before changing gateways.
The best choice between LiteLLM and Obot AI depends on the missing capability. Obot fits teams that need MCP hosting, local-client visibility, and server governance. A broader gateway is appropriate when the requirement combines model routing, MCP controls, budgets, agent workflows, and enterprise compliance into a single policy and observability layer.



The latest news, articles, and resources sent to your inbox