October 10, 2026
|
5 min read


احصل على وصول فوري إلى بيئة TrueFoundry مباشرة. انشر النماذج، ووجّه حركة مرور LLM، واستكشف المنصة بالكامل — بيئة الاختبار الخاصة بك جاهزة في ثوانٍ، ولا يلزم وجود بطاقة ائتمان.



Published: October 6, 202616
Blazingly fast way to build, track and deploy your models!
التحكم في وصول وكلاء الذكاء الاصطناعي هو مجموعة من السياسات التي تقرر ما إذا كان بإمكان جهة اتصال معينة الوصول إلى مورد معين. إنه يجيب على سؤال "هل هذا مسموح به؟"، بينما تجيب حواجز الحماية على سؤال "ما الذي يحتويه هذا؟".
هذا التمييز يستحق الاهتمام، لأن كلا نوعي التحكم يفشلان بطرق مختلفة، لذا فأنت بحاجة إلى كليهما.
يمكن أن يكون الوكيل مخولاً بالكامل لاستدعاء خادم MCP الخاص بقاعدة بياناتك، ومع ذلك يتم خداعه لإرسال استعلام تدميري. لقد وافق التحكم في الوصول على الخادم، ولا يمكن إلا لحاجز الحماية على الوسائط اكتشاف ما يفعله الاستعلام فعلياً. إذا قمت بتوسيع نطاق الوصول بشكل مفرط، فأنت تعتمد كلياً على جهاز الكشف عن المعادن. مبدأ الصلاحيات الأقل هو ما يحافظ على الحد الأدنى من الاستدعاءات المسموح بها في المقام الأول.
تطبق TrueFoundry التحكم في الوصول على مستويين، وفهم هذا التقسيم هو الجزء الأكبر من العمل.
يمكنك إضافة مستخدم أو فريق أو حساب افتراضي كمتعاون مباشرة على مورد ما، واختيار دور يحدد نطاق وصولهم إلى ذلك المورد فقط. الأدوار خاصة بنوع المورد:
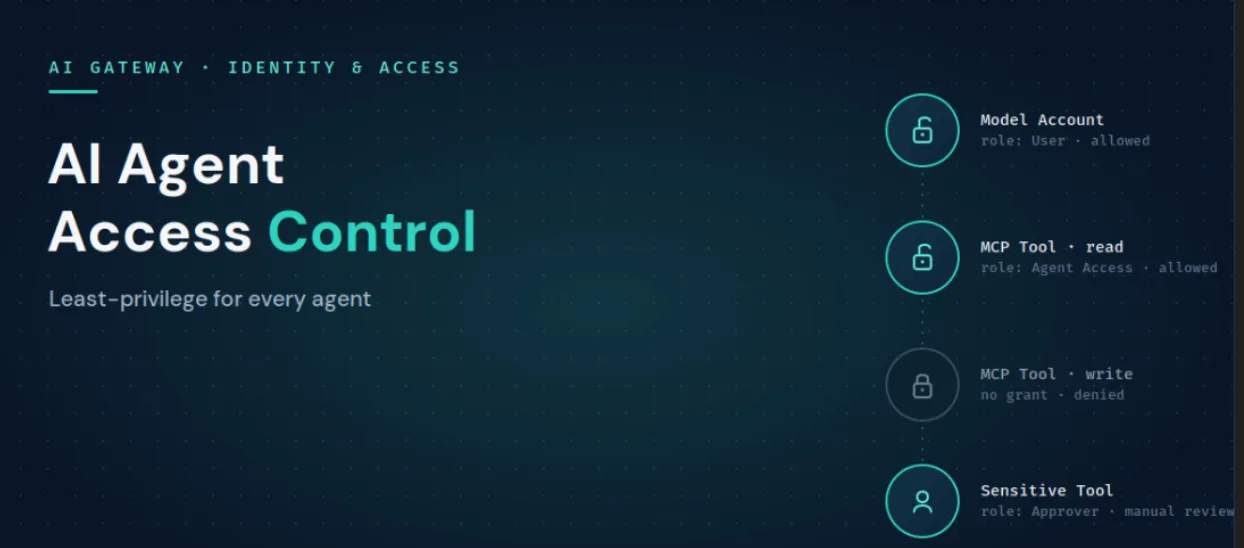
هنا يكمن جوهر مبدأ الصلاحيات الأقل. امنح الوكيل "وصول الوكيل" (Agent Access) فقط لخوادم MCP التي يحتاجها لعمله، واجعل الفريق "مستخدماً" (User) على حساب النموذج الذي يُسمح له باستدعائه، وأضف "موافقاً على خادم MCP" (MCP Server Approver) عندما تتطلب الأداة موافقة قبل تشغيلها. لا حاجة لإنشاء أدوار مخصصة لأي من ذلك.
تطبق الأدوار على مستوى المستأجر عبر المستأجر بأكمله ويتم تكوينها ضمن "الوصول" (Access)، ثم "الأدوار" (Roles). وهي تحكم الإجراءات على مستوى المستأجر مثل إنشاء الموارد، وإدارة المستخدمين، وإدراج كل مورد من نوع معين. توفر TrueFoundry دورين افتراضيين: المسؤول (Admin)، والذي يتمتع بالتحكم الكامل ويجب أن يقتصر على عدد قليل من الأشخاص، و العضو (Member)، والتي لا تملك افتراضياً صلاحية الوصول إلى أي شيء، ويجب منحها صلاحية الوصول إلى الموارد بشكل صريح. وعندما تكون هاتان الصلاحيتان واسعتين جداً أو ضيقتين جداً، يمكنك إنشاء دور مخصص.
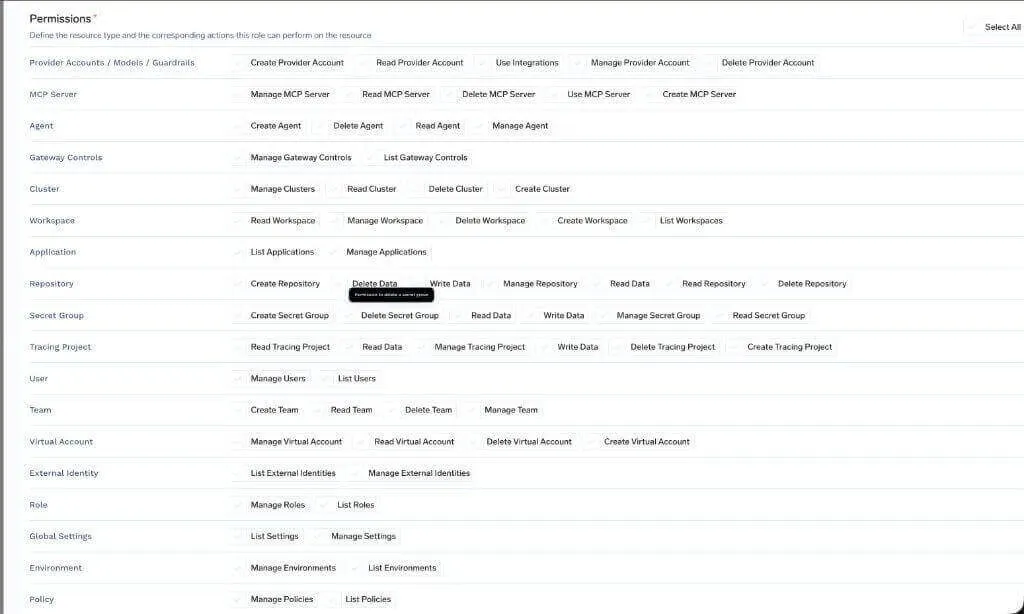
لقطة شاشة للمنتج، وثائق TrueFoundry: أذونات الأدوار المخصصة.
يمكن تعيين الأدوار للفرق وكذلك للمستخدمين الأفراد، وتكون الأذونات الفعلية للمستخدم هي مجموع أذونات دوره الخاص وجميع الأدوار الموروثة من فرقه. بالنسبة للمؤسسات التي تقوم بمزامنة مجموعات الهوية عبر بروتوكول SCIM، يتم استيراد هذه المجموعات كفرق في TrueFoundry ويمكن منحها أدواراً مباشرة، بحيث يتبع الوصول نفس مصدر الحقيقة الذي يديره مزود الهوية (IdP) الخاص بك بالفعل.
تفصل بوابة MCP بين ثلاثة جوانب غالباً ما تتداخل مع بعضها البعض في الفرق، وهذا الفصل هو ما يجعل تطبيق مبدأ "أقل الصلاحيات" على مستوى الأداة أمراً عملياً.
TrueFoundry AI Gateway delivers ~3–4 ms latency, handles 350+ RPS on 1 vCPU, scales horizontally with ease, and is production-ready, while LiteLLM suffers from high latency, struggles beyond moderate RPS, lacks built-in scaling, and is best for light or prototype workloads.


AI agent access control is the set of policies that decide whether an agent, user, or team is allowed to reach a given model, MCP server, or individual tool. It governs whether a call is permitted, which is a separate job from guardrails that inspect what a call contains. On TrueFoundry it is enforced at the gateway through resource-level collaborators and tenant-level roles.
Access control decides whether a call is allowed to happen. Guardrails inspect the content of a call that is already allowed, catching injections, PII, secrets, and unsafe operations. You need both: access control keeps the set of permitted calls small, and guardrails police what flows through the ones that are permitted.
Give each agent its own identity, then grant it access only to the specific model accounts and MCP tools its function requires, using resource-level collaborator roles. Scope the agent to its job rather than to the permissions of the person driving it, use approver roles for sensitive tools, and prefer team-based grants so access stays manageable.
Yes. Access rules on the MCP Gateway can narrow to specific tools within a server, so an agent can be granted a read-only tool while the write tool on the same server stays off limits. Because the gateway fronts every call, the rule covers every caller of that tool automatically.
نعم. تعمل TrueFoundry في شبكتك الافتراضية الخاصة (VPC)، أو في موقعك، أو في بيئة معزولة، أو في بيئة هجينة، أو عبر سحابات متعددة، ولا تغادر أي بيانات نطاقك. هذا هو السبب الرئيسي الذي يجعل الشركات الخاضعة للتنظيم تفضلها على بوابات SaaS فقط.
Yes. It includes an MCP Gateway, Agent Gateway, and an MCP and Agents Registry with tool-level access control, governing agents from LangGraph, CrewAI, AutoGen, and custom frameworks from one place.



أحدث الأخبار والمقالات والموارد تصلك مباشرة إلى بريدك الوارد