


Erhalten Sie sofortigen Zugriff auf eine TrueFoundry-Live-Umgebung. Stellen Sie Modelle bereit, leiten Sie den LLM-Verkehr weiter und erkunden Sie die gesamte Plattform — Ihre Sandbox ist in Sekundenschnelle einsatzbereit, ohne dass eine Kreditkarte erforderlich ist.


What is Infrastructure as Code and how does it work?

As a company’s software systems grow, IT teams need to manage more servers, databases, storage, and network resources across development, testing, and production environments.
Relying on manual processes and manual configuration becomes harder as infrastructure grows. It can also create configuration drift, where environments gradually become different because changes are applied inconsistently.
Infrastructure as Code (IaC) replaces much of this manual infrastructure management with code and infrastructure automation. Teams define the required infrastructure in files that can be reviewed, tested, versioned, and reused.
This guide explains what is Infrastructure as Code, how it works, the main approaches, benefits, tools, and use cases.
What is Infrastructure as Code?
Infrastructure as Code (IaC) is a DevOps practice for managing and provisioning IT infrastructure through code instead of manual setup.
Teams create infrastructure definitions that describe the required servers, databases, networks, security policies, access control, and other infrastructure components. These files act as a single source of truth for how the environment should be configured.
For example, instead of asking system administrators to configure a virtual machine manually, a team can define its size, operating system, network settings, and security rules in code. The IaC tool then applies those settings automatically.
Because these definitions are treated much like source code, teams can store them in source control, review pull requests, test infrastructure updates, and track their history.
IaC can manage virtual resources in the cloud as well as infrastructure that ultimately runs on physical hardware. This gives teams a repeatable approach to managing both legacy infrastructure and modern infrastructure.
How does Infrastructure as Code work?
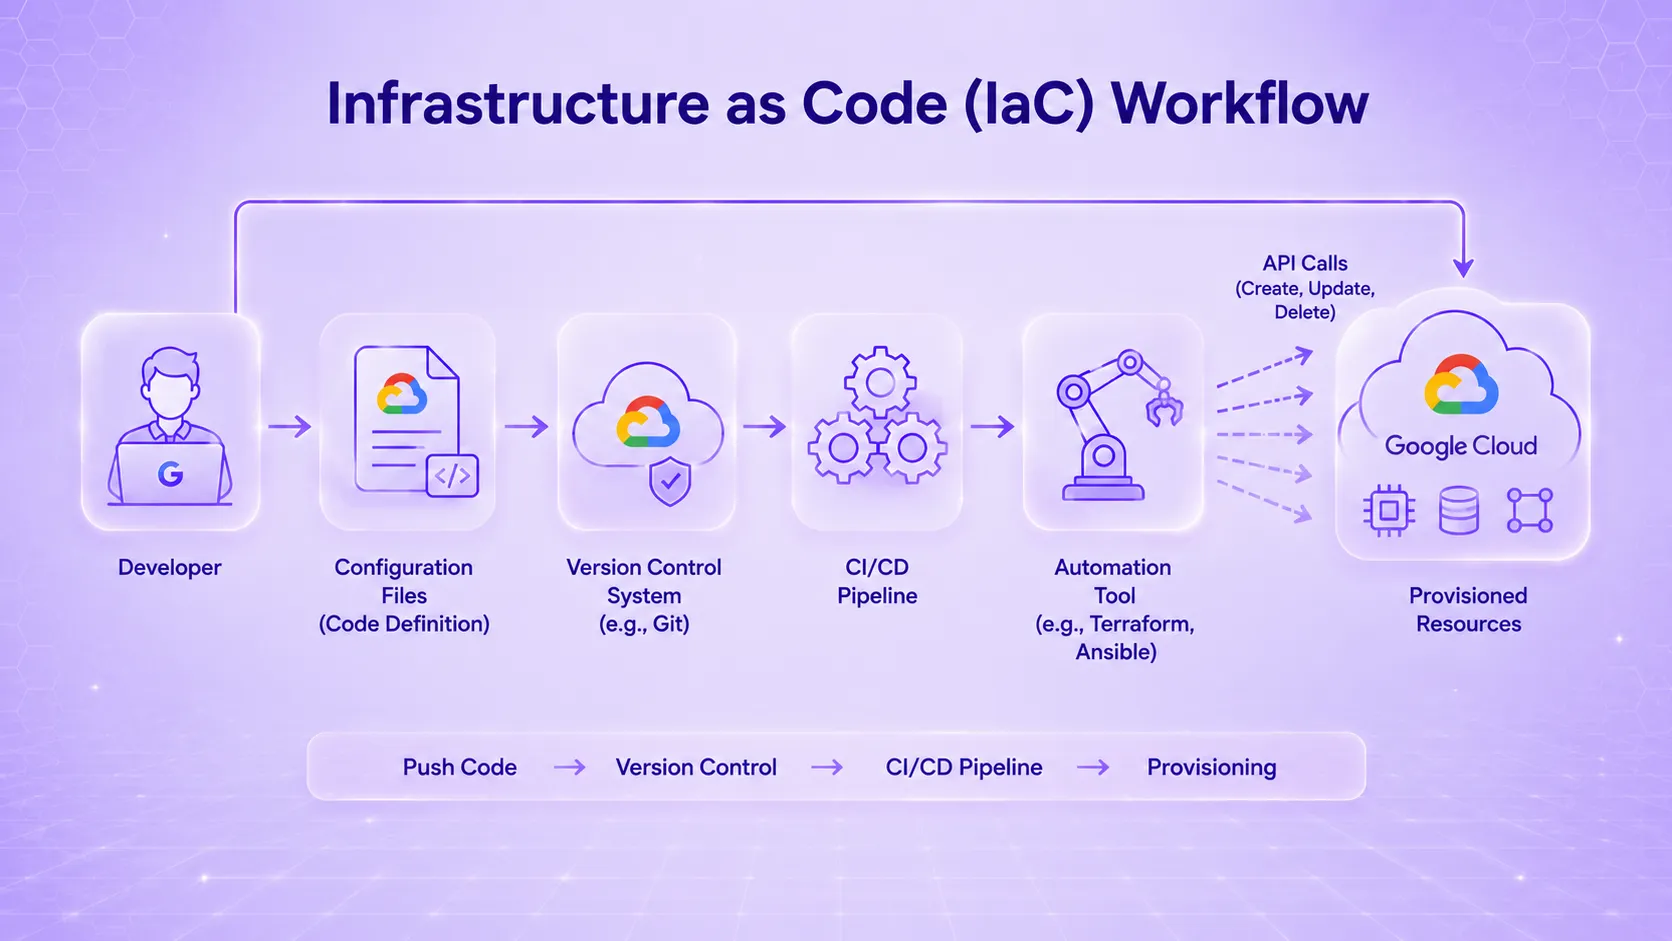
Infrastructure as Code follows a repeatable process in which infrastructure requirements are written in configuration files and applied through automation tools.
The process usually looks like this:
- Write the configuration: Teams describe the servers, storage, networks, security rules, and other resources they need. These infrastructure definitions specify the environment’s required configuration.
- Define the desired state: With declarative IaC, teams describe the desired state of the infrastructure. The tool compares that state with the existing environment and determines which changes are required.
- Store the files in source control: Systems such as Git keep infrastructure code alongside other project files. This creates a single source of truth and allows teams to review changes through pull requests before they are applied.
- Run validation and error checking: Teams can check syntax, configuration, security vulnerabilities, and policy violations before an infrastructure deployment begins.
- Run the automation tool: The IaC tool connects to the target platform through APIs and applies the approved configuration. Depending on the IaC solution, this may involve AWS services, Google Cloud resources, Kubernetes infrastructure, or on-premises systems.
- Create or update the infrastructure: The tool creates, changes, or removes resources to match the approved configuration. These repeatable infrastructure deployments reduce the need for one-off manual changes.
For example, if a service needs more servers during a traffic spike, the team can change the required server count in the IaC file. The tool then applies that change automatically instead of requiring each server to be created manually.
Because the same definitions can be reused across environments, IaC also helps teams maintain a consistent cloud architecture as infrastructure changes.
What are the different approaches to Infrastructure as Code?
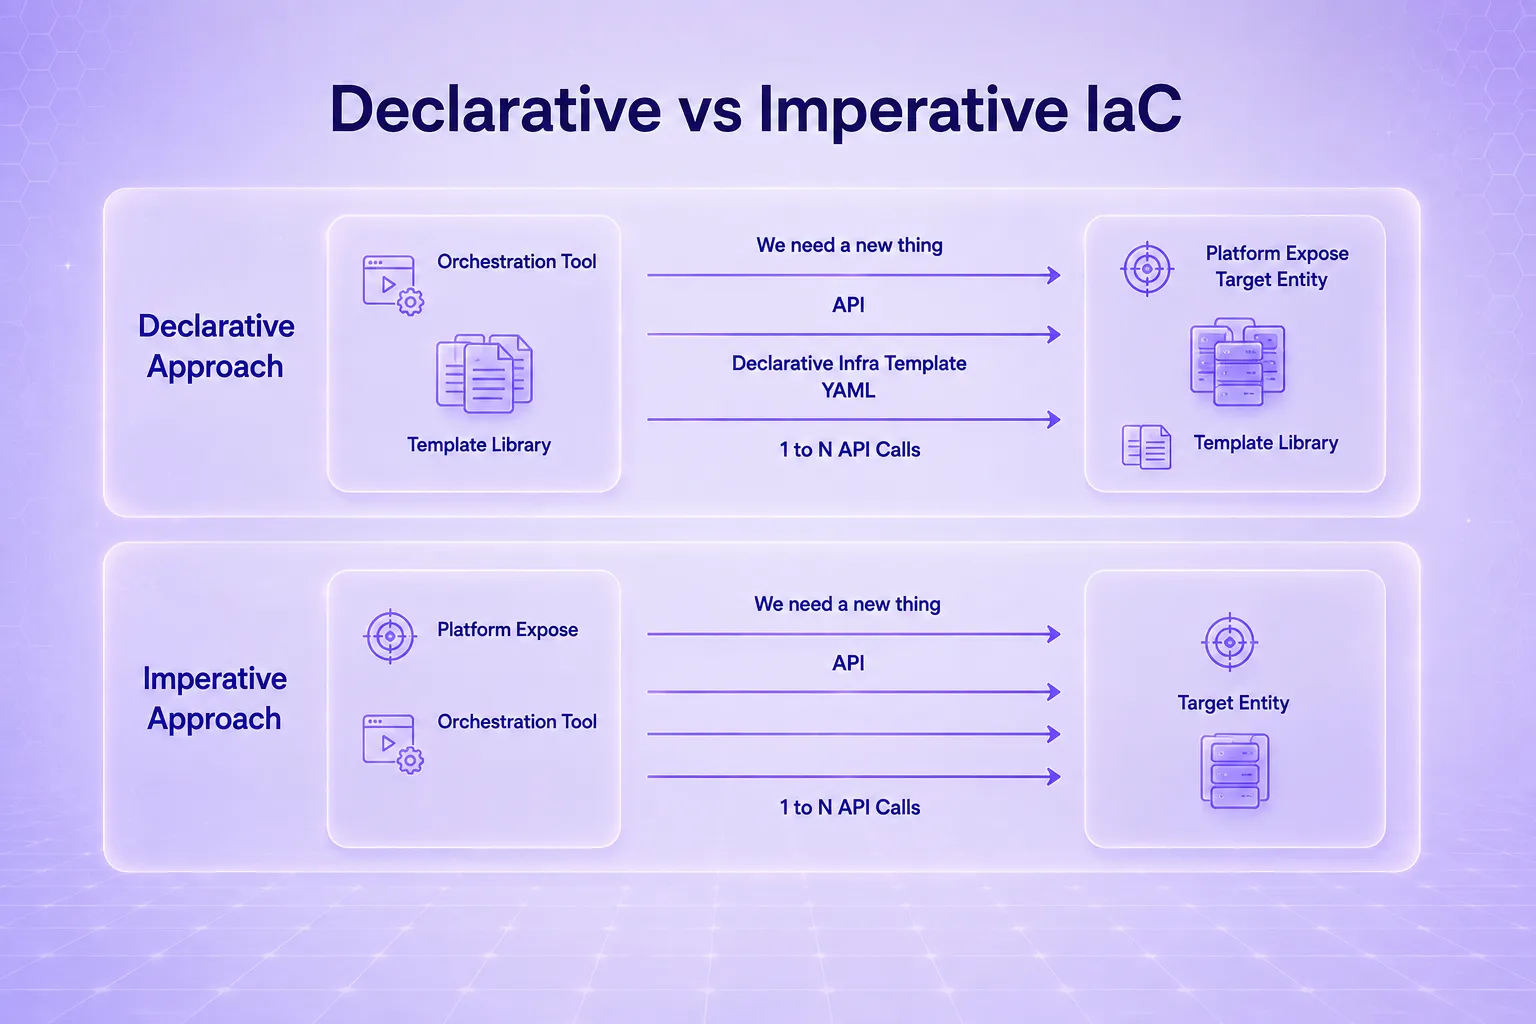
Infrastructure as Code can follow different approaches. The choice depends on whether teams want to define the final state, control each step, or use programming languages to describe the infrastructure.
Declarative approach to IaC
In the declarative approach, teams describe what the final infrastructure should look like. The IaC tool determines the changes required to reach that state.
For example, a team can specify that an application needs:
- Three servers
- One database
- One load balancer
The tool compares this desired setup with the existing infrastructure and makes the required changes.
This approach reduces the need to define every step manually and helps keep environments consistent. Terraform and AWS CloudFormation are common examples of declarative IaC tools.
Imperative approach to IaC
In the imperative approach, teams describe how the infrastructure should be created. They write the commands or steps that need to run in a specific order.
For example, the instructions may tell the system to:
- Create a server
- Install the required software
- Change its settings
- Deploy the application
This approach gives teams more control over the order of operations but requires more detailed instructions.
Programmable approach to IaC
Some IaC tools also let teams define infrastructure programmatically using general-purpose languages such as Python, JavaScript, TypeScript, or Go.
Instead of relying only on a dedicated IaC language, developers can use familiar programming features such as:
- Loops
- Conditions
- Functions
- Reusable components
For example, Pulumi lets teams write infrastructure code in languages such as Python, JavaScript, and Go. AWS CDK also lets developers define AWS infrastructure using programming languages and then converts that code into CloudFormation templates.
What are the benefits of Infrastructure as Code?
Infrastructure as Code gives teams a structured way to manage infrastructure through code and automation. This becomes especially useful as environments, teams, and deployment frequency grow.
The main benefits include:
- Faster provisioning: Infrastructure automation allows teams to create complete environments without repeating manual processes for every resource.
- More consistent environments: Using the same definitions across production and test environments reduces configuration differences and helps prevent configuration drift.
- Fewer manual errors: Automated configuration reduces mistakes caused by manual configuration, missed settings, or one-off infrastructure changes.
- Better version control and traceability: Infrastructure code can be stored as source code, making infrastructure updates easier to review, audit, and roll back.
- Easier collaboration: Development, operations, security, and other IT teams can review changes through the same source-control and pull-request workflows.
- Reusable infrastructure: Teams can reuse infrastructure definitions across projects instead of rebuilding environments from scratch.
- Stronger security controls: Automated checks can identify security vulnerabilities and confirm that security policies and access control rules are applied consistently.
- Support for immutable infrastructure: Teams can replace infrastructure with a newly configured version instead of repeatedly modifying existing resources. This immutable infrastructure approach can reduce configuration drift.
- Better cloud operations: Repeatable deployments make cloud operations easier to standardize across multiple environments and providers.
Following IaC best practices, such as version control, code review, automated testing, and policy checks, helps teams get these benefits without introducing unnecessary operational risk.
How does IaC fit into DevOps and CI/CD pipelines?
Infrastructure as Code fits into DevOps by bringing infrastructure changes into the same code-based workflow used for application code. Infrastructure definitions can be versioned, reviewed, tested, and deployed as part of the broader software development lifecycle.
Connecting infrastructure management with DevOps
IaC gives development and operations teams a shared way to manage infrastructure changes. Instead of managing infrastructure changes separately, teams use the same code-based review and version-control workflow before changes are applied.
This helps teams:
- Keep a history of infrastructure changes
- Review updates before they go live
- Follow the same process across development, testing, and production
Automating infrastructure through CI/CD pipelines
IaC files can also become part of a CI/CD pipeline, where infrastructure changes move through automated validation and deployment stages.
During continuous integration, the pipeline can:
- Check syntax and configuration
- Run automated error checking
- Scan for security vulnerabilities
- Validate security policies
- Confirm that proposed infrastructure changes are valid
During continuous delivery, approved infrastructure code can move through test environments and become ready for production deployment.
Teams can apply additional approvals before production, depending on their governance and cloud operations requirements.
Managing infrastructure after deployment
IaC is also useful after the first deployment. Teams can update the same code when they need to add resources, change settings, or apply security updates.
Since these changes are stored in version control, teams can see what changed over time and manage infrastructure without relying on repeated manual updates.
What are the different tools and technologies for Infrastructure as Code?
Infrastructure as Code tools can support different parts of infrastructure management, from provisioning resources to checking code before deployment. Common categories include:
Terraform and OpenTofu are commonly used across multiple cloud providers. OpenTofu is an open source IaC tool, while Terraform also supports a broad provider ecosystem.
Pulumi lets teams define infrastructure using languages such as Python, JavaScript, TypeScript, and Go. This can help developers manage infrastructure using concepts already familiar from application code.
AWS CloudFormation and the AWS Cloud Development Kit are designed for AWS environments and can provision a wide range of AWS services.
Ansible is widely used for configuration management and automation. Red Hat also offers Ansible-based tooling for broader enterprise automation workflows.
How to choose the right IaC tool?
The right IaC tool depends on the infrastructure being managed and how the team prefers to work. Key factors to consider include:
- Cloud platform support
- Multi-cloud requirements
- Configuration files or programming language preference
- Integration with DevOps and CI/CD workflows
- Security and compliance needs
- State management and team collaboration
- Provider and module ecosystem
- Ease of reviewing and maintaining infrastructure changes
For example, Terraform and OpenTofu work well across multiple providers, while AWS CloudFormation and AWS CDK are designed for AWS environments.
What are the common use cases and examples of Infrastructure as Code?
Infrastructure as Code is useful when teams need to recreate environments, manage infrastructure across multiple platforms, or make changes through a repeatable process. Common use cases include:
Multi-cloud and hybrid cloud deployments
IaC can help teams manage resources across multiple providers or across cloud and on-premises infrastructure. For example, an organization may run some workloads using AWS services while using Google Cloud for other infrastructure components. The environments can still be managed through a consistent code-based process.
Containerized and Kubernetes environments
IaC is commonly used to provision the compute, networking, and storage resources required by Kubernetes clusters. Teams can use the same infrastructure definitions to create development, test, and production environments. This makes container infrastructure easier to reproduce and manage.
Test and staging environments
Development teams often need separate test environments before application code reaches production. IaC allows these environments to be created from the same definitions as production. Teams can test infrastructure updates, application changes, security policies, and access control before release.
Machine learning infrastructure
IaC can also support machine learning workloads that need repeatable compute, storage, networking, or Kubernetes environments. For example, teams can define the infrastructure required for model training and deployment, then recreate the same setup across development and production.
Teams can also use IaC to provision the compute, networking, Kubernetes, and security resources needed to run an on-prem AI Gateway inside a private cloud, VPC, or on-premises environment.
Disaster recovery and environment recreation
IaC can help teams rebuild infrastructure after a failure because the required setup is already defined in code. Instead of recreating servers, networks, and other resources manually, teams can use stored infrastructure definitions to restore the environment more consistently.
IaC recreates infrastructure configuration, while application data still requires separate backup and recovery processes.
Manage AI Infrastructure with IaC
Infrastructure as Code gives teams a repeatable way to create and manage infrastructure through code instead of handling each change manually. It also makes infrastructure changes easier to track, test, and apply across different environments.
The right IaC approach and tool depend on the infrastructure being managed, the cloud environment, and how the team prefers to work.
Teams managing AI applications across cloud and Kubernetes environments can use TrueFoundry’s AI Gateway to centralise model access, routing, governance, and observability.
You can also book a demo to explore the platform.
Steuern, implementieren und verfolgen Sie KI in Ihrer eigenen Infrastruktur

GenAI infra- einfach, schneller, günstiger
Top-Teams vertrauen uns bei der Skalierung von GenAI

- © 2022 ENSEMBLE Technologies



Abonnieren Sie unseren Newsletter
Die neuesten Nachrichten, Artikel und Ressourcen werden in Ihren Posteingang gesendet


