September 28, 2026
|
5 min read

Published: September 28, 2026

Blazingly fast way to build, track and deploy your models!
Most “vs” posts start by making the other product sound worse than it is. This one cannot. Arcade raised a $60M Series A on 12 June 2026 led by SYN Ventures, with strategic investment from Morgan Stanley and Wipro, taking total financing to $72M (Arcade Series A announcement). Morgan Stanley is both investor and named customer.
The useful question is narrower: what does each product cover, and what will you still have to buy afterwards? That has a factual answer in both vendors’ docs.
Arcade no longer calls itself a tool-calling platform. Its framing is now the actions runtime: “Arcade is the actions runtime between your agents and every system they reach. One control point to enforce, execute, and govern every action, every time.”
It also swings directly at gateway vendors, worth quoting because it frames the disagreement honestly: “Start with the API gateway vendors. They’re solving a networking problem. They route traffic. Routing traffic isn’t authorizing an action” (Arcade Series A blog). The control point, Arcade argues, belongs at the action, not the network hop.
[SCREENSHOT: Arcade.dev — the dashboard showing a tool execution with the delegated user authorization step visible]
Authorization is the real differentiator, and it is deep. Every action runs at the intersection of what the user may do and what the agent may do — not a service account, not a shared token. Arcade brokers OAuth, handles refresh and rotation, and injects credentials at execution so they never reach the agent or MCP client. It supports generic OAuth 2.0 plus 33 named providers and five IdP user sources: Auth0, Clerk, Entra ID, Okta and Stytch (Arcade auth providers docs).
Arcade authored the MCP tool authorization specification, which it states is “now adopted by Anthropic and the major MCP clients and servers,” and sits on MCP security and governance steering committees — corroborated externally (SiliconANGLE, 25 November 2025). Standards authorship is a durable advantage; we will not talk around it.
The tool catalogue is large, though how large depends which page you read: “7,000+ tools / 80+ toolkits” on the product page, “7,500+ tools / 81 MCP servers” in the docs, “8,000+” on the homepage and in the Series A blog. We note the inconsistency rather than pick for them. The positioning is “agent-optimized… not thin API wrappers”, backed by a public benchmark at toolbench.arcade.dev.
[SCREENSHOT: Arcade.dev — the toolkit catalogue page showing available toolkits and per-tool detail]
Smithery gives Arcade the registry. On 5 August 2026 Arcade acquired Smithery, “a leading public registry and hosting platform for MCP” (Smithery joins Arcade). Smithery still runs as a separate brand and lists 23,611+ MCP servers. Arcade’s own Registry is still Early Access — but Arcade now owns the biggest public MCP index and its developer funnel.
The rest of the surface. An MCP Gateway federating Arcade-hosted, custom and third-party servers behind one endpoint, with nine documented remote-MCP vendor integrations (Salesforce, ServiceNow, Snowflake, Atlassian, GitHub, Splunk and more). Reference-grade Python SDK docs, ten frameworks, six MCP clients. Contextual Access for pre and post tool-call policy hooks and group-based tool access. And a six-page evals section — scoped to tool-call accuracy rather than model quality, but real and documented, which is more than many competitors offer.
Deployment: Arcade is not SaaS-only. Its docs list Arcade Cloud, the Azure and AWS marketplaces, GCP (explicitly “coming soon”), self-hosting with Helm, and hybrid MCP servers (Arcade deploy docs). Marketing goes further — “Cloud, on-prem, air-gapped, or hybrid”. Anyone saying Arcade cannot run in your own infrastructure has not read the docs.
Compliance: SOC 2 Type 2, achieved 18 August 2025 (Arcade SOC 2 post). HIPAA, ISO 27001 and GDPR: [VERIFY] — not claimed on any page we could read, and the trust centre is a JavaScript-rendered portal with no crawlable content.
Pricing, published and usage-based:
Two metered dimensions — auth events and tool calls — is unusual and worth modelling before you commit. And SSO, RBAC and audit logs are Enterprise-gated on the pricing page, despite the homepage saying “SSO, RBAC, and full audit logs out of the box.”
TrueFoundry is an AI control plane. The MCP gateway is one component inside it rather than the whole product — the crux of this comparison.
MCP gateway and registry. Six documented ways to add a server — TrueFoundry-managed, official remote, any remote, Virtual MCP Server, OpenAPI import, hosted stdio — plus 43 per-vendor doc pages and a registry with public list/version APIs.
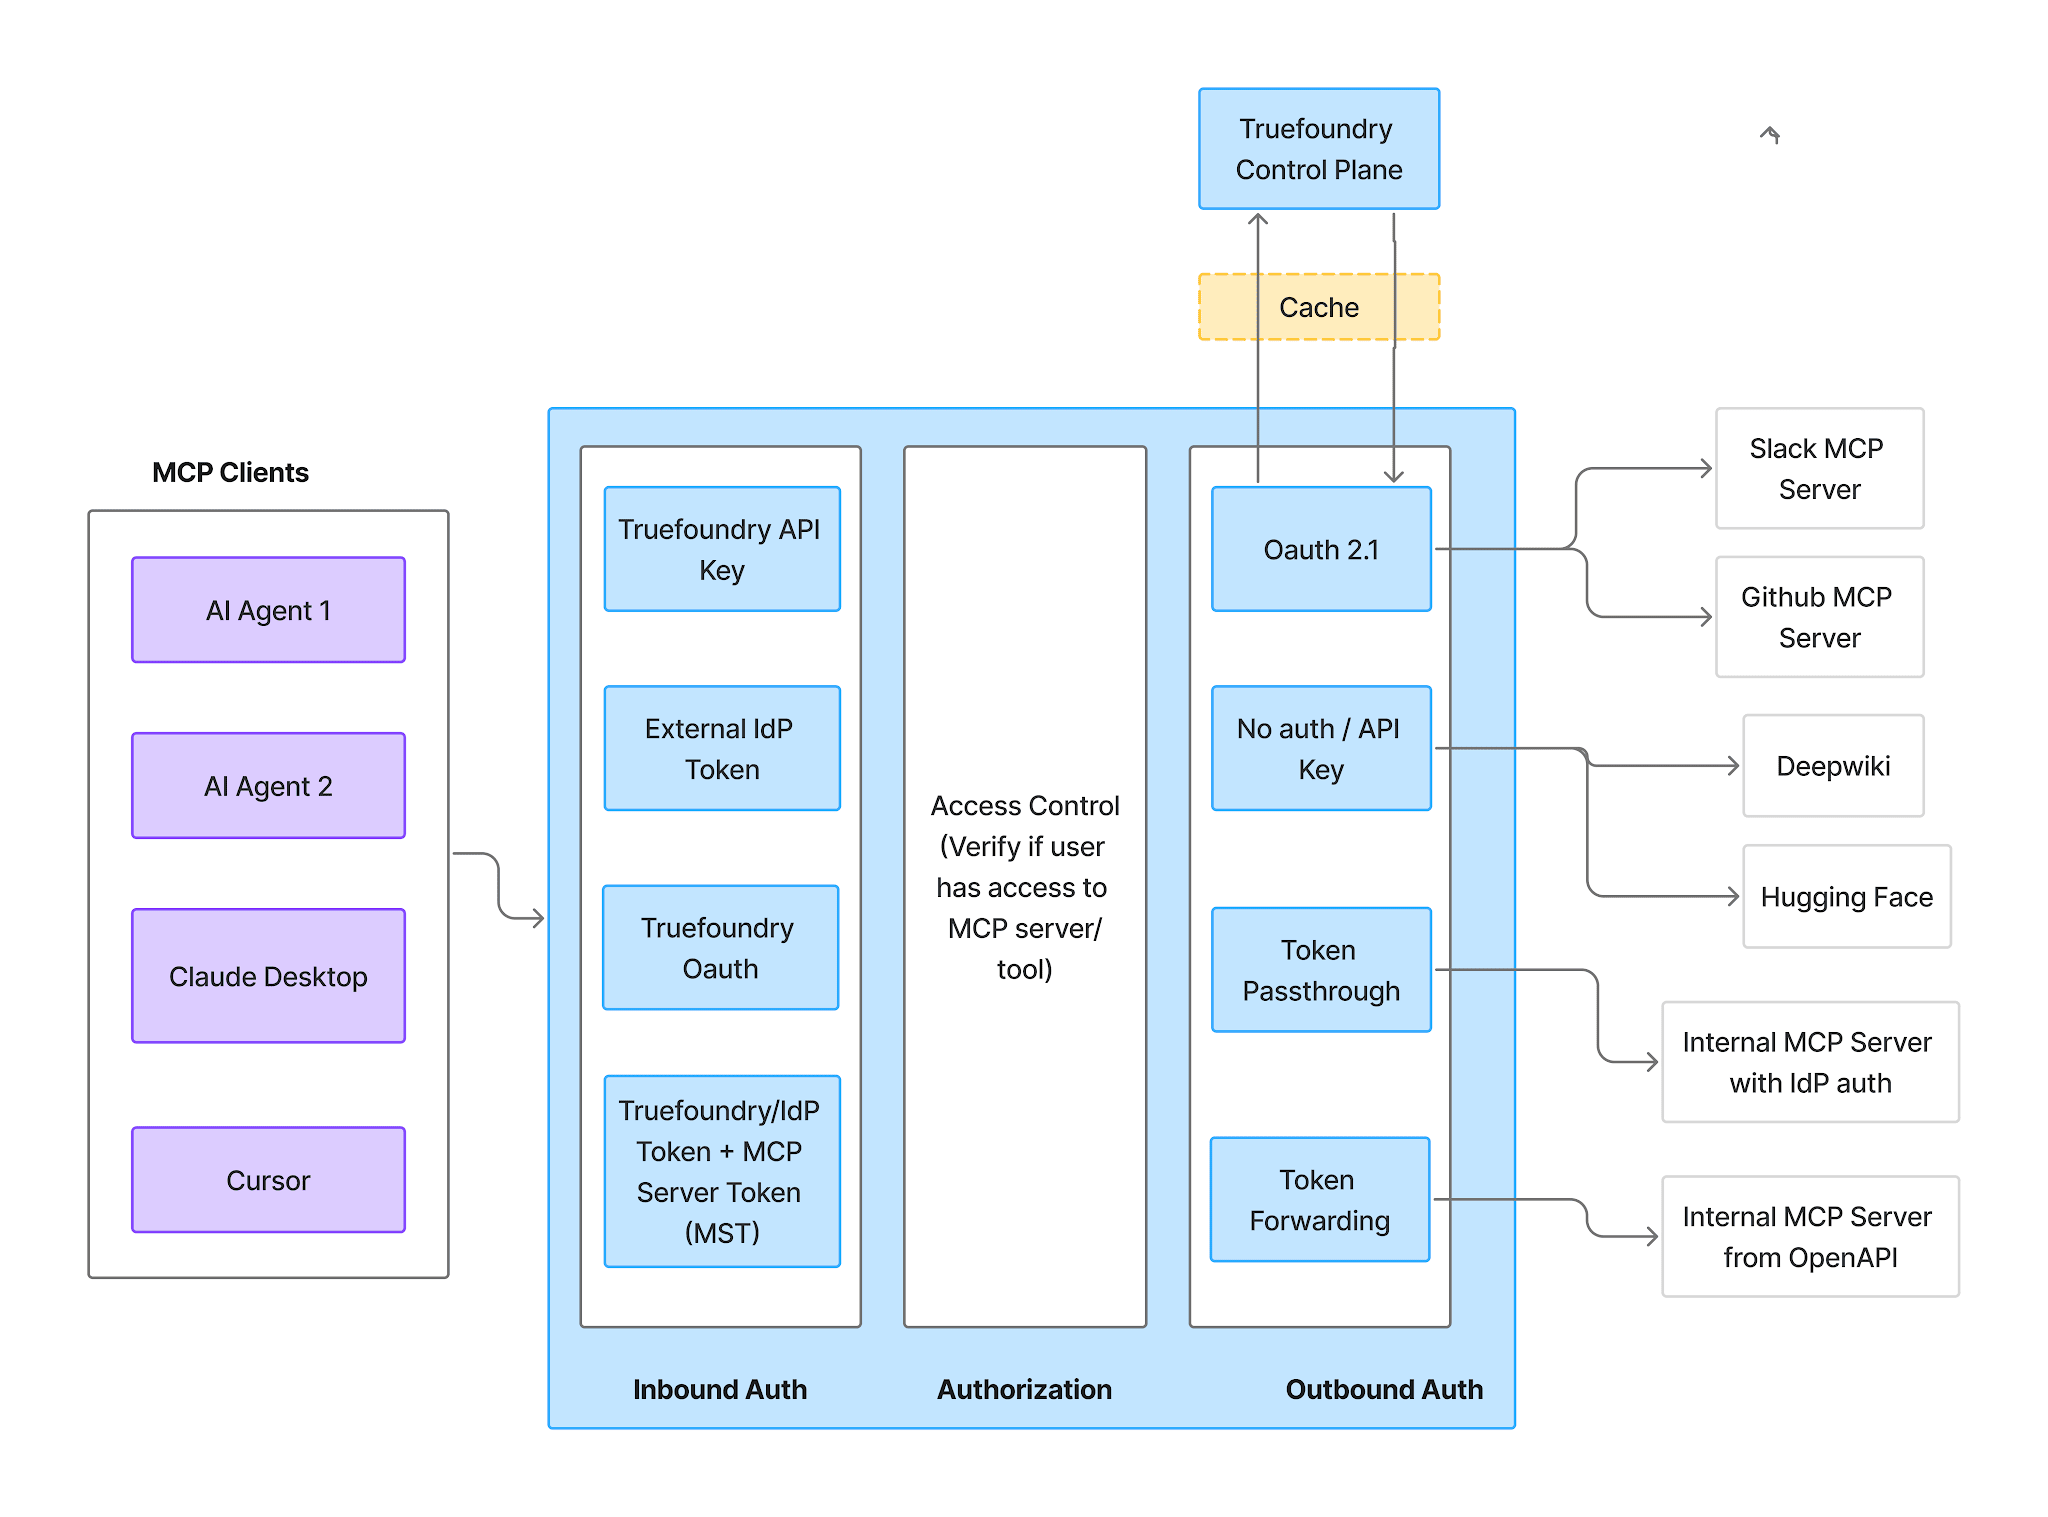
On auth — the head-to-head with Arcade’s strongest area — TrueFoundry documents nine outbound modes: OAuth2 authorization code, client credentials, token exchange / on-behalf-of (Okta and Entra jwt-bearer), shared and individual API keys, no auth, token passthrough, token forwarding and AWS SigV4, plus four inbound modes. It also publishes an MCP protocol support matrix across four spec revisions through 2026-07-28, covering OAuth 2.1, RFC 9728, RFC 7591, RFC 8707 and OIDC discovery per revision. Arcade publishes no equivalent matrix.
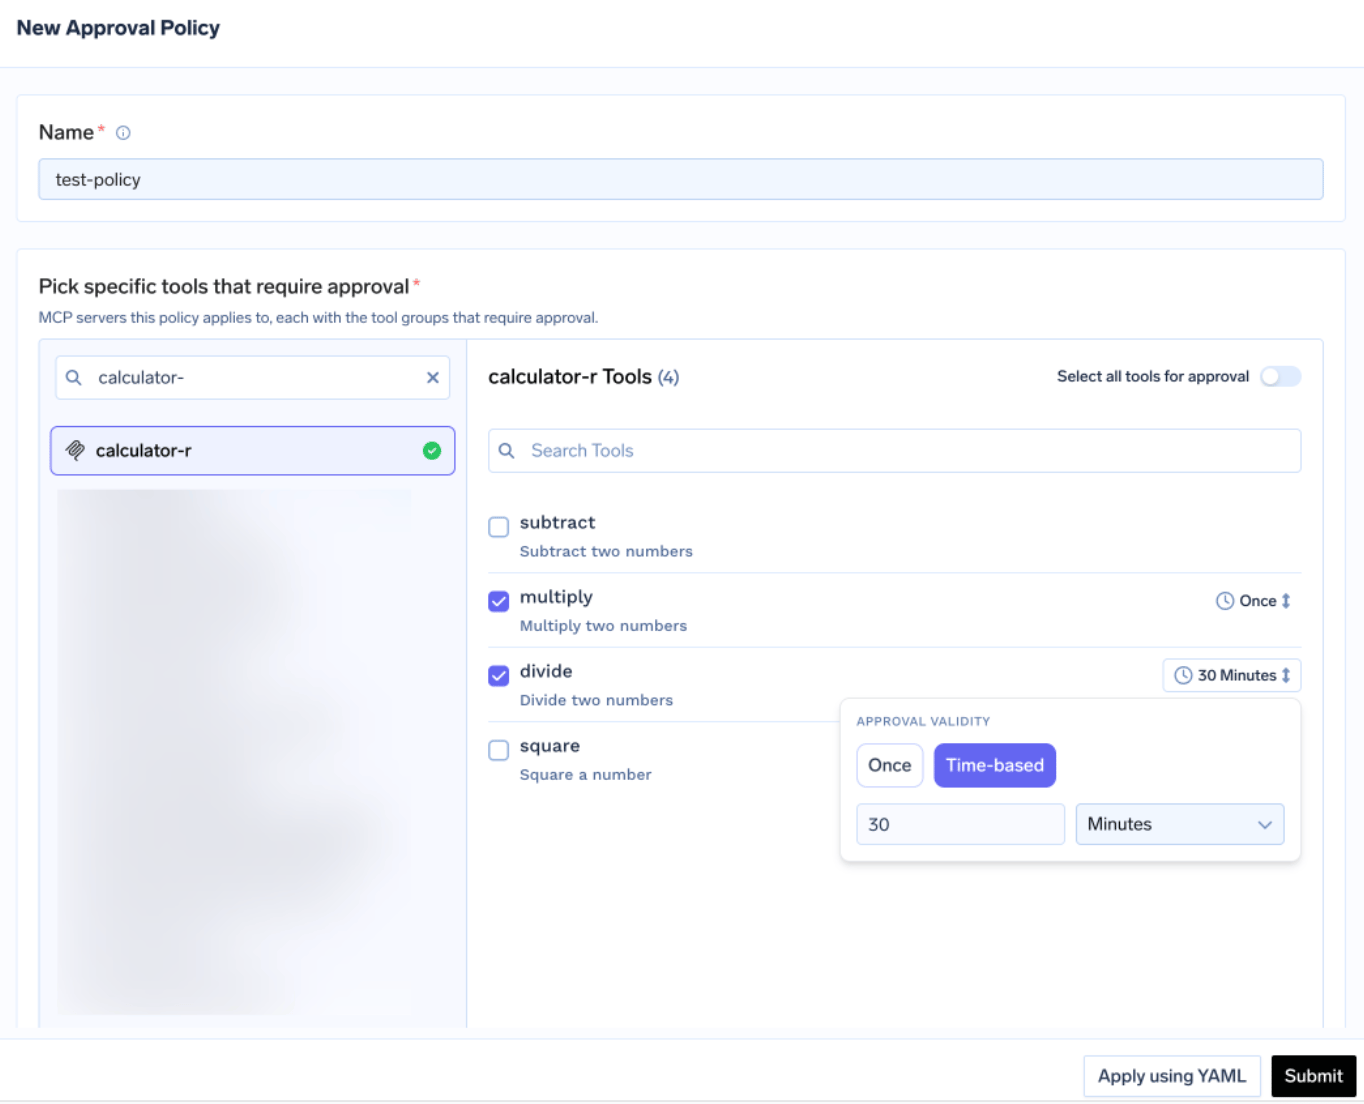
Human-in-the-loop approval is a capability Arcade does not document: scopes of named, destructive or all, grant expiry, and Email, Slack, PagerDuty or Teams notifications. With MCP tool annotations (None / Read-only / Destructive), you can require sign-off before an agent runs anything write-shaped (more detail).
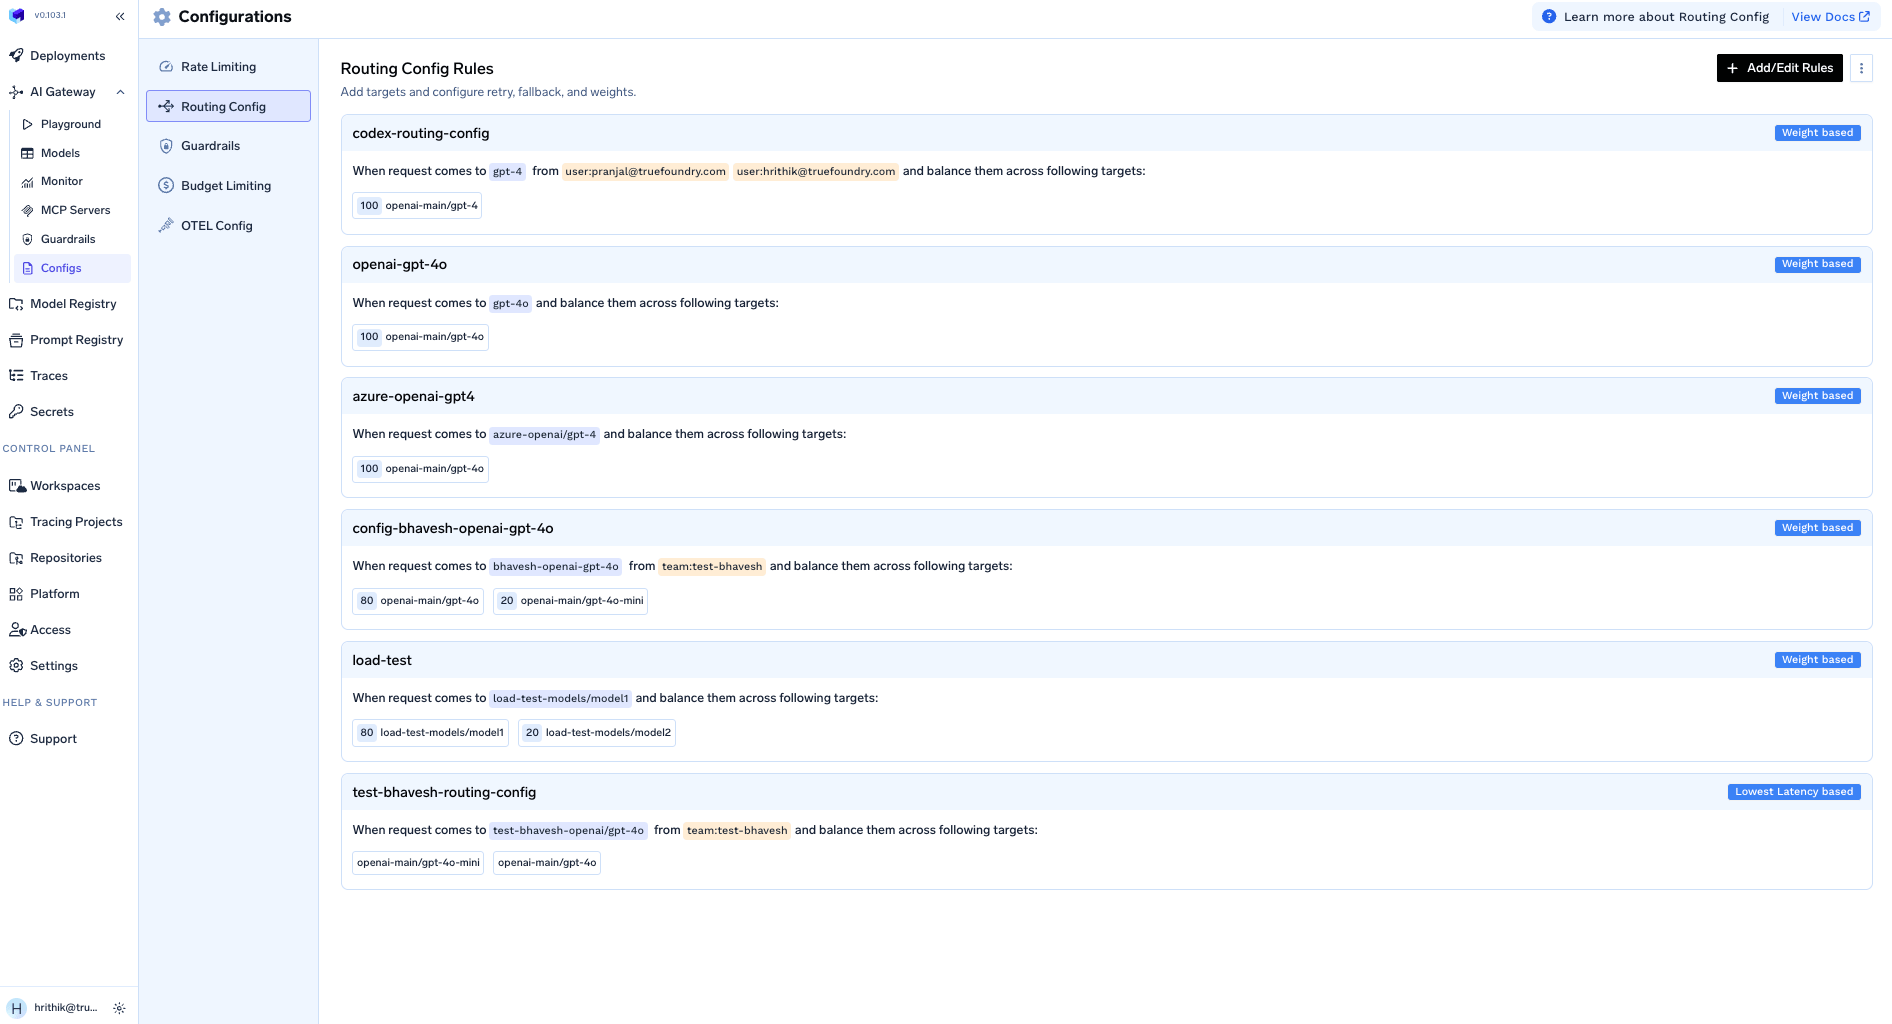
The AI Gateway. 1,000+ models across 28 named providers behind one OpenAI-compatible API, with weight-based routing (canary, sticky sessions), priority-based fallback with SLA cutoffs on TTFT and TPOT, latency-based strategies, exact-match and semantic caching, and token or request rate limiting per minute, hour or day.
Model deployment. vLLM, SGLang, Triton, TorchServe, TF Serving, MLflow and LitServe, with a model registry, autoscaling on CPU, RPS or cron, and fractional GPUs via TimeSlicing and MIG. Arcade has no product here and does not claim one.
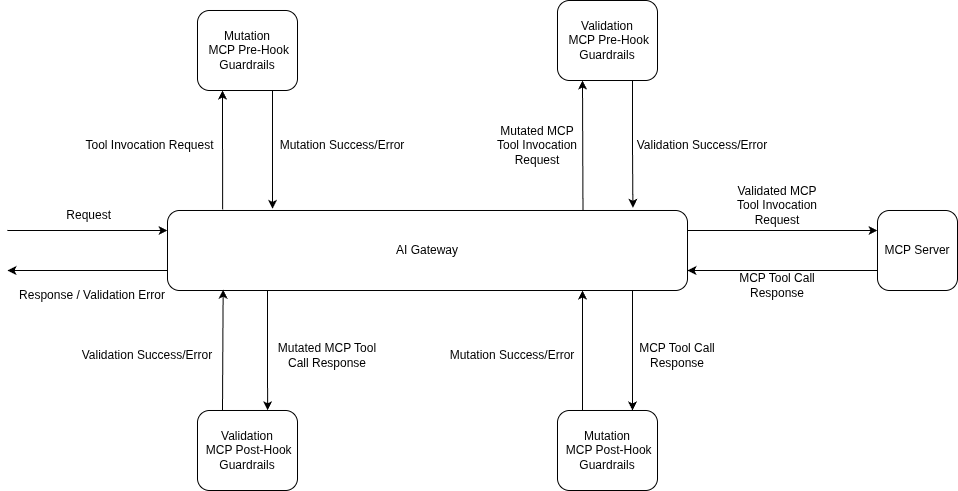
Guardrails. Four hook points — LLM input, LLM output, MCP pre-tool and MCP post-tool — with nine built-in guardrails (secrets detection, code safety, SQL sanitizer, regex, prompt injection, PII, content moderation, Cedar, OPA) and 17 external providers including Bedrock Guardrails, Azure Content Safety, CrowdStrike and Google Model Armor. Honest caveat: content moderation, PII and prompt-injection guardrails run only on the TrueFoundry-hosted gateway, not when you host it yourself.
Cost and budgets. Budget Limiting V2 with tenant-level and team-scoped budgets — “use team budgets when a team lead should manage their own team’s spending without tenant-admin access” — scoped by subject, model, provider account or metadata, with a warn-only mode. Cost tracking runs off an open-source pricing catalog at github.com/truefoundry/models; attribution flows through an X-TFY-METADATA header.
RBAC and SSO. Subjects can be a user, team, virtual account or agent. Resources span provider accounts, MCP servers, agents, clusters, workspaces, repositories and secret groups, each with its own role family. SSO over OIDC or SAML 2.0 with SCIM 2.0 provisioning — SAML guides for nine IdPs, SCIM for four. Arcade documents five IdP sources and no SCIM.
Deployment and compliance. Seven documented scenarios: SaaS across 12+ regions and 3 clouds; self-hosted and VPC via Helm plus OpenTofu/Terraform, with guides for AWS, GCP, Azure, OpenShift and generic Kubernetes; on-prem; and air-gapped, documented concretely in three places. SOC 2 Type II, HIPAA and GDPR are consistently claimed. ISO 27001: [VERIFY] — older doc pages list it, the security page does not. SIEM export is coming soon, a live gap against Arcade.
Pricing: Developer $0 (3 users, 10k requests/user, 5 MCP servers), Pro $25/user/mo (unlimited users, 20k requests/user, +$20 per additional 100K requests), Enterprise custom. MCP tool calls draw on the same allowance as LLM requests — no separate MCP meter.
Every “Not documented” entry was checked against Arcade’s docs navigation and its product, pricing and tools pages on 25 September 2026.
Two product boundaries, not a scorecard. Arcade drew its boundary at the action and went deeper there than anyone; TrueFoundry drew it around the whole model-and-agent path.
1. The two-product problem. Arcade governs tool calls; it does not carry model traffic. The moment your agent calls an LLM — which is every agent — you need a second product for routing, fallback, caching and rate limits. That is not a criticism; it is what Arcade’s docs say. But the real evaluation becomes “Arcade plus a gateway” versus “one control plane,” and cost and operational surface should be compared on that basis.
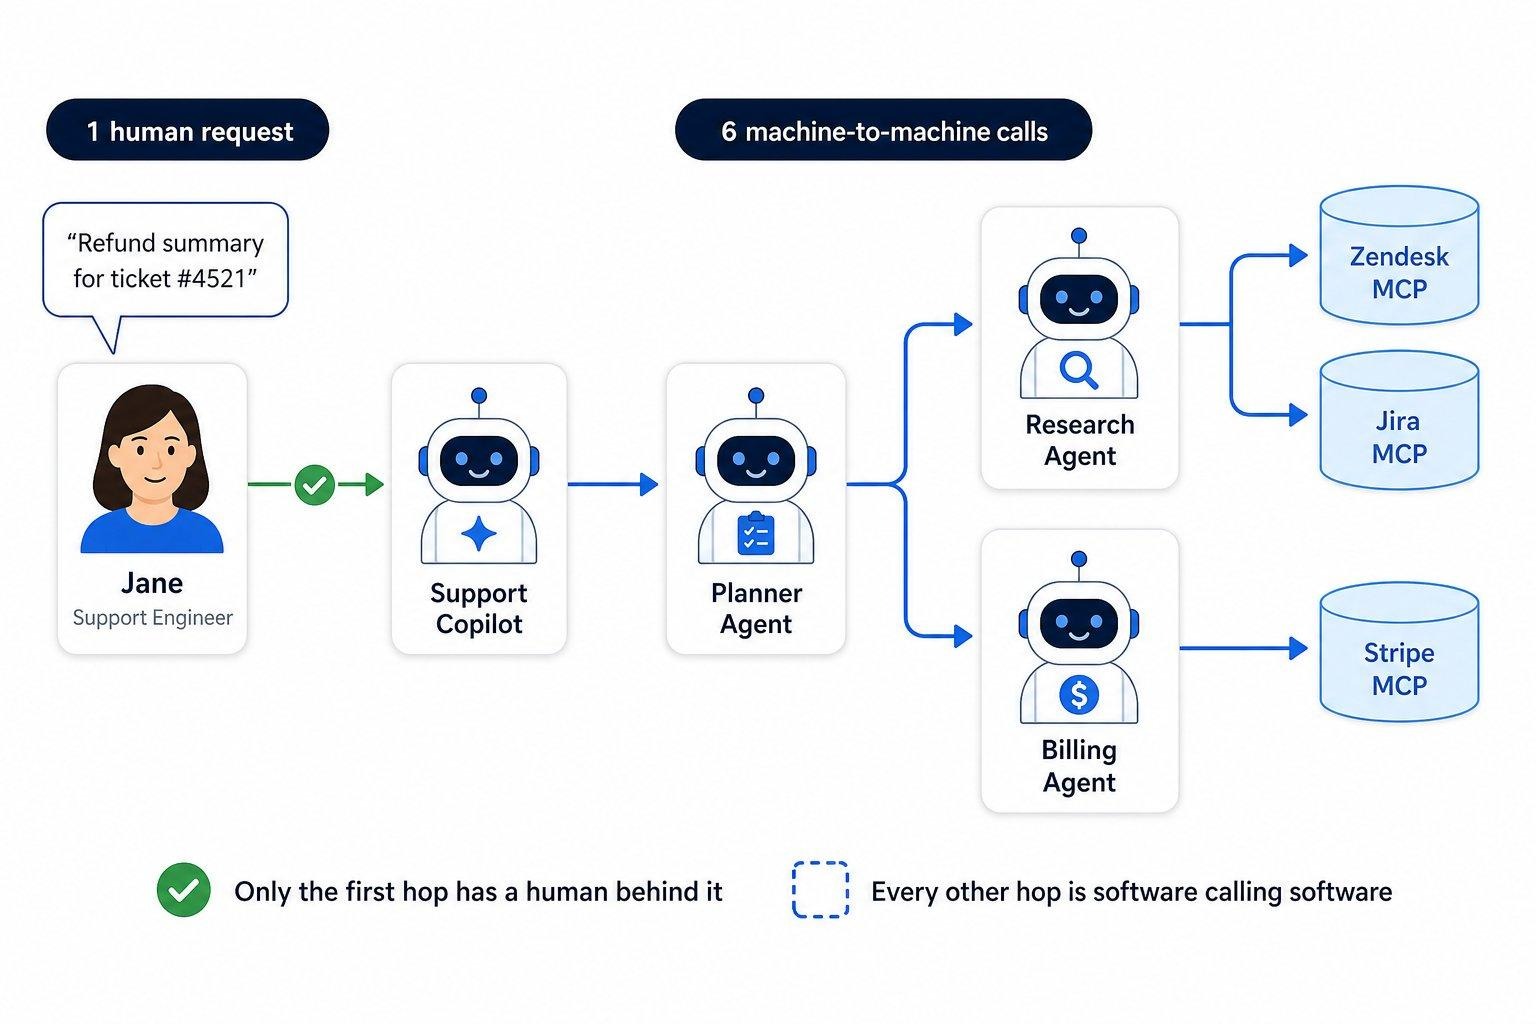
2. Identity fragments across two control planes. Two places where a user, team or agent is defined, two places to provision and deprovision, two places to revoke a departing employee. Arcade documents five IdP user sources and no SCIM; your gateway will have its own model. Keeping those in sync is work nobody budgets for. More in MCP access control.
3. Cost lives in two places and reconciles in neither. Arcade meters auth events and tool calls; your gateway meters tokens. Neither knows about the other, so “what did the support agent cost last month” becomes a spreadsheet. Arcade documents no budget or chargeback feature — rate limits throttle, they do not cap spend.
4. Audit surfaces do not join up. Arcade streams tool-execution logs to your SIEM, which is genuinely useful. But the prompt that triggered the call, the model that produced it, and the guardrail that did or did not fire live in the other system. Reconstructing an incident means correlating two log formats by timestamp.
The argument is not that TrueFoundry does authorization better than Arcade. It is that authorization is one of six or seven things a platform has to get right, and solving one leaves six.
TrueFoundry’s AI Gateway adds roughly 3-4 ms of latency, handles 350+ RPS on 1 vCPU, and fronts 1,000+ LLMs behind one OpenAI-compatible API. Those numbers decide whether you can put the gateway in front of everything or only the important traffic — and a control point that covers some of the traffic is not a control point.
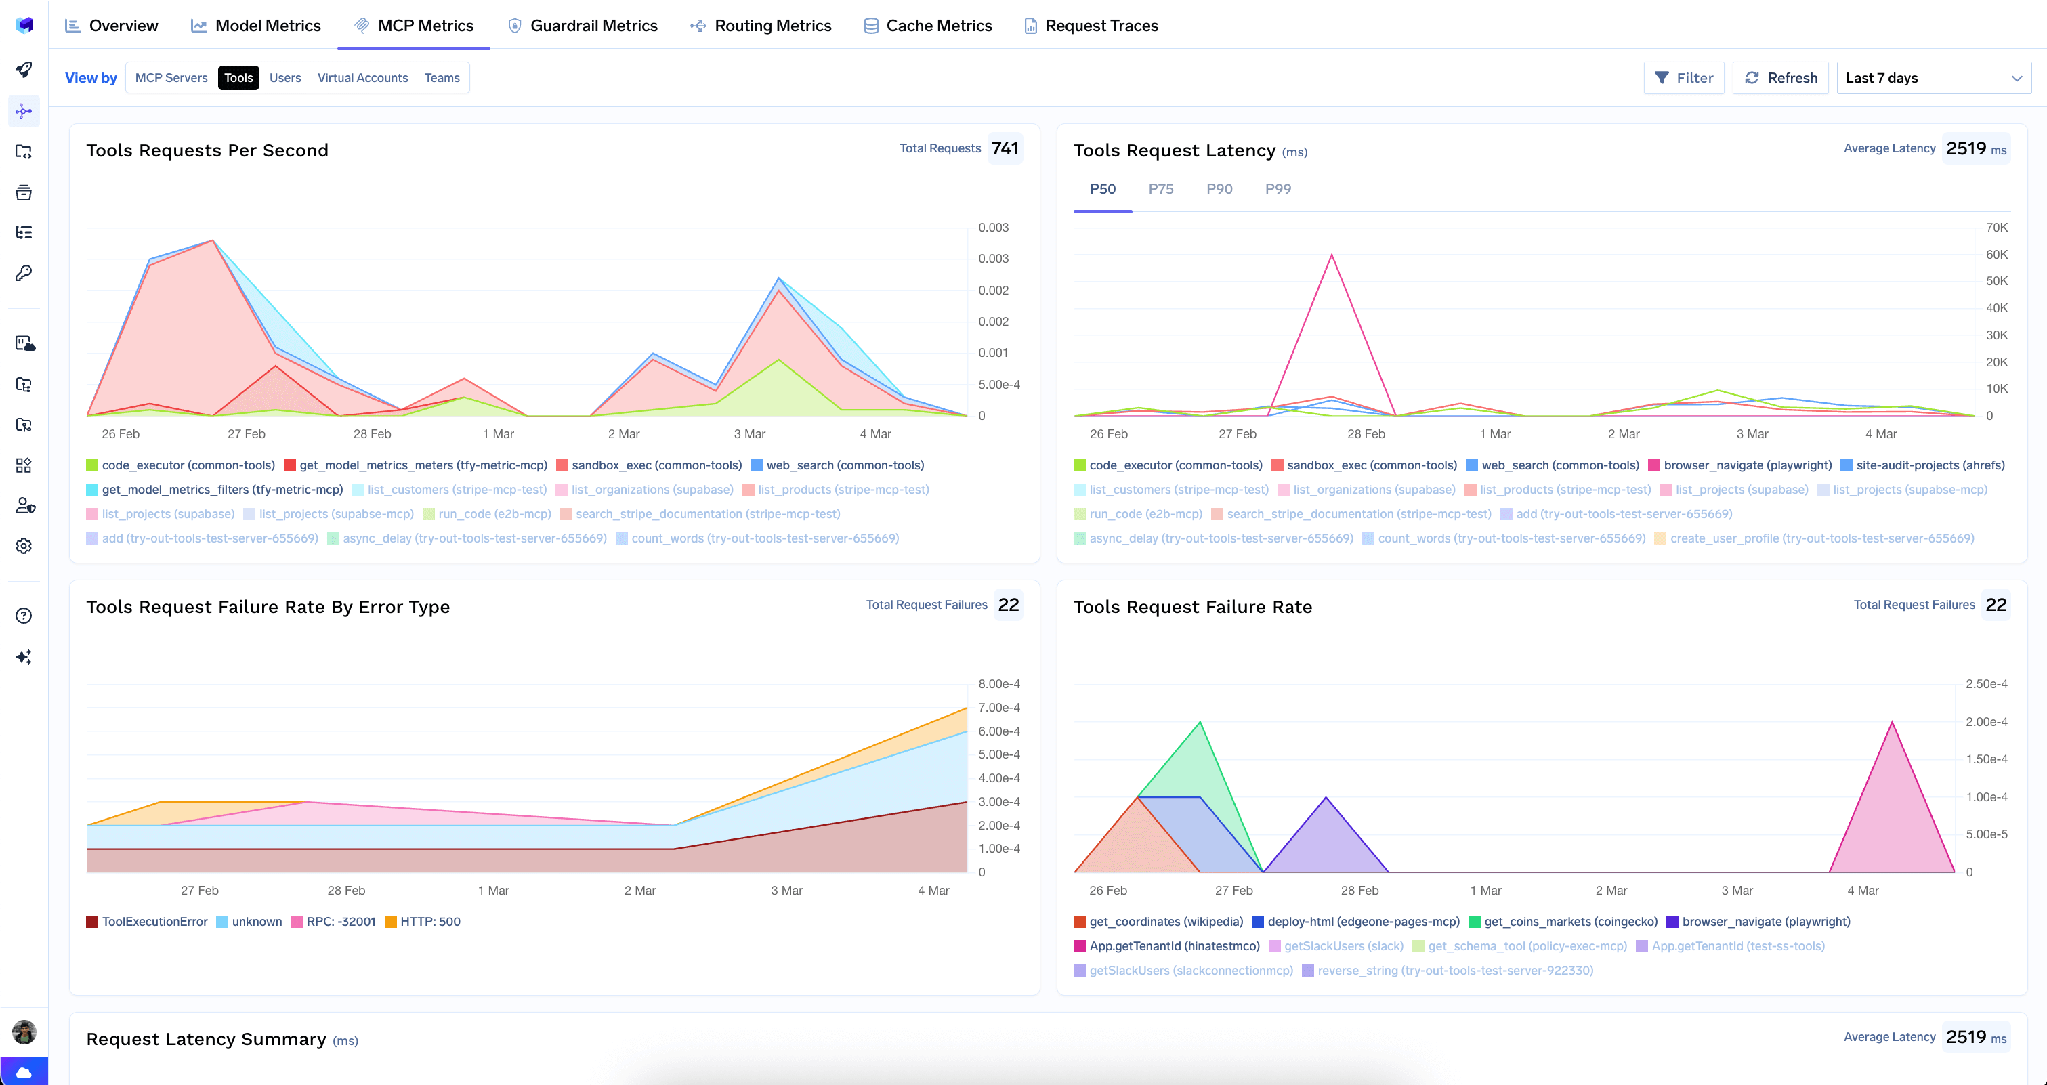
Because MCP tool calls and LLM requests run the same path, they land in the same metrics, traces and budgets. MCP metrics cover total calls, top servers, top tools, RPS per server and P50-P99 latency with tool-level drill-down — next to model spend, not in a different product.
Auto Routing is a cost lever that does not exist in a tool-only product. Across 550 prompts, routing between model tiers by request complexity cut cost by 69% while retaining 98% of baseline quality, with mean latency falling from 7.6s to 4.0s; on production-shaped traffic the reduction reached 80%. Pair that with team-scoped budgets and you get cost attribution a team lead can actually manage.
We would rather you pick correctly.
The scope table carries the detail. This is the decision summary.
Arcade.dev is a strong product with a defensible thesis, real enterprise customers, standards authorship and $72M behind it. If someone tells you it is lightweight or that it cannot run in your infrastructure, they have not looked.
The reason to choose differently is scope. Arcade governs what an agent is allowed to do. It does not govern what model the agent talks to, what that costs, whether the prompt leaked a secret, or who approved the destructive call — and its own documentation is clear about that. So the real comparison is Arcade plus a gateway plus a guardrail layer plus a budgeting story, versus one control plane that contains all four.
If your hardest problem is OAuth across thirty SaaS tools, buy the thing that solves it. If it is that nobody can say what your agents cost, what they touched, and who said yes, you want the control plane.
TrueFoundry AI Gateway delivers ~3–4 ms latency, handles 350+ RPS on 1 vCPU, scales horizontally with ease, and is production-ready, while LiteLLM suffers from high latency, struggles beyond moderate RPS, lacks built-in scaling, and is best for light or prototype workloads.




No, and it does not claim to be. Arcade’s only “gateway” product is the MCP Gateway, which federates tool servers. No model routing, fallback, provider failover or token-based rate limiting appears in its docs navigation as of 25 September 2026. Adopt Arcade and your model traffic still needs a gateway in front of it.
Yes. Arcade documents Helm-based self-hosting alongside Arcade Cloud, AWS and Azure marketplace deployments and hybrid MCP servers, with GCP coming soon, and markets on-prem and air-gapped. The caveat is documentation depth: as of 25 September 2026 there is no air-gapped install guide in the docs deploy section, whereas TrueFoundry documents air-gapped install across three doc pages.
For tool authorization specifically the alternatives are thin — that is Arcade’s moat. For an MCP gateway inside a broader control plane, TrueFoundry, Kong and IBM ContextForge are the usual comparisons; see best MCP gateways.
No. MCP tool calls draw on the same request allowance as LLM requests, on the same seats. Arcade meters two dimensions on the Team plan — auth events at $0.10 each and tool calls at $0.01 each — worth modelling if your agents are chatty.
Split. Arcade holds SOC 2 Type 2 since August 2025 and streams logs to your SIEM over OpenTelemetry today. TrueFoundry holds SOC 2 Type II, HIPAA and GDPR, but SIEM export is still coming soon. ISO 27001 is [VERIFY] for both. If SIEM streaming gates your rollout, Arcade wins that line item.



The latest news, articles, and resources sent to your inbox