November 5, 2026
|
5 min read

Blazingly fast way to build, track and deploy your models!
Artificial intelligence has moved from experimentation into increasingly important business workflows. Today, it drives decisions, automates workflows, and powers customer experiences across industries. But as AI systems scale, so do the risks, from data bias and model opacity to security lapses and accountability gaps. These challenges demand more than policies; they demand enforceable, technology-driven governance.
An AI governance framework provides the foundation for using AI responsibly, defining policies, standards, and oversight mechanisms to ensure every model aligns with ethical, legal, and organizational goals. Yet, translating these frameworks into daily practice requires infrastructure.
That’s where AI Gateway comes in. Acting as the control plane between applications and models, a gateway can centralize access management, apply content guardrails, log every model call for audit, and enforce compliance policies at scale.
As regulations like the EU AI Act, NIST AI RMF, and ISO 42001 reshape global standards, enterprises need both frameworks and infrastructure. Governance defines the “what” and “why.” The AI Gateway delivers the “how.”
In this blog, let us talk about the AI governance framework, its objectives, principles and more.
As organisations use AI across more teams and business processes, they need clear rules for how these systems are built, deployed, monitored, and managed. An AI governance framework provides that structure. It brings together policies, processes, roles, safeguards, and oversight to help an organisation use AI responsibly while managing its risks.
In simple terms, AI governance is about how an organisation sets rules and responsibilities for the way AI is developed and used. An AI governance framework turns those principles into something more practical, with defined processes, controls, roles, and checks that teams can follow.
Organisations do not have to create all of these rules from scratch. They can use established external frameworks like NIST AI Risk Management Framework (AI RMF), ISO/IEC 42001, and the EU AI Act and regulations to shape their approach. For example, a company might refer to a risk-management framework for guidance, adopt a recognised management-system standard, or follow specific legal requirements that apply to its AI systems.
This is where the difference between NIST AI RMF, ISO/IEC 42001, and the EU AI Act becomes important. Although all three can influence an organisation's approach to AI governance, they are not interchangeable.
The NIST AI Risk Management Framework (AI RMF) is a voluntary framework that helps organisations identify and manage AI risks. ISO/IEC 42001 is a management-system standard for establishing and maintaining an AI management system. The EU AI Act is binding legislation that sets legal requirements for AI systems within its scope.
So, your AI governance framework is the organisation-specific system you put in place, while external frameworks, standards, and laws can provide the guidance or requirements that help shape it.
The core objectives of an AI governance framework are accountability, transparency, and compliance. Together, they help ensure AI systems have clear owners, can be understood and audited, and operate within the rules that apply to them.
Establish clear accountability: Organisations define who owns AI systems, approves their use, manages risks, and reviews incidents. Access controls and audit logs can support traceability.
Maintain transparency: Keep a record of which models are in use, what they are used for, and how they perform. Centralised observability gives compliance and engineering teams shared visibility into model usage and performance.
Ensure compliance: Turn regulatory requirements and internal policies into enforceable controls. Policy-based routing and guardrails can help apply requirements such as data residency and content restrictions consistently across models.
Unlike traditional IT governance, AI governance must manage dynamic, evolving systems that learn over time. An AI Gateway such as TrueFoundry's can support this with centralised access controls, policy enforcement, logging, and monitoring across AI traffic, so governance is applied at the point where models are called.
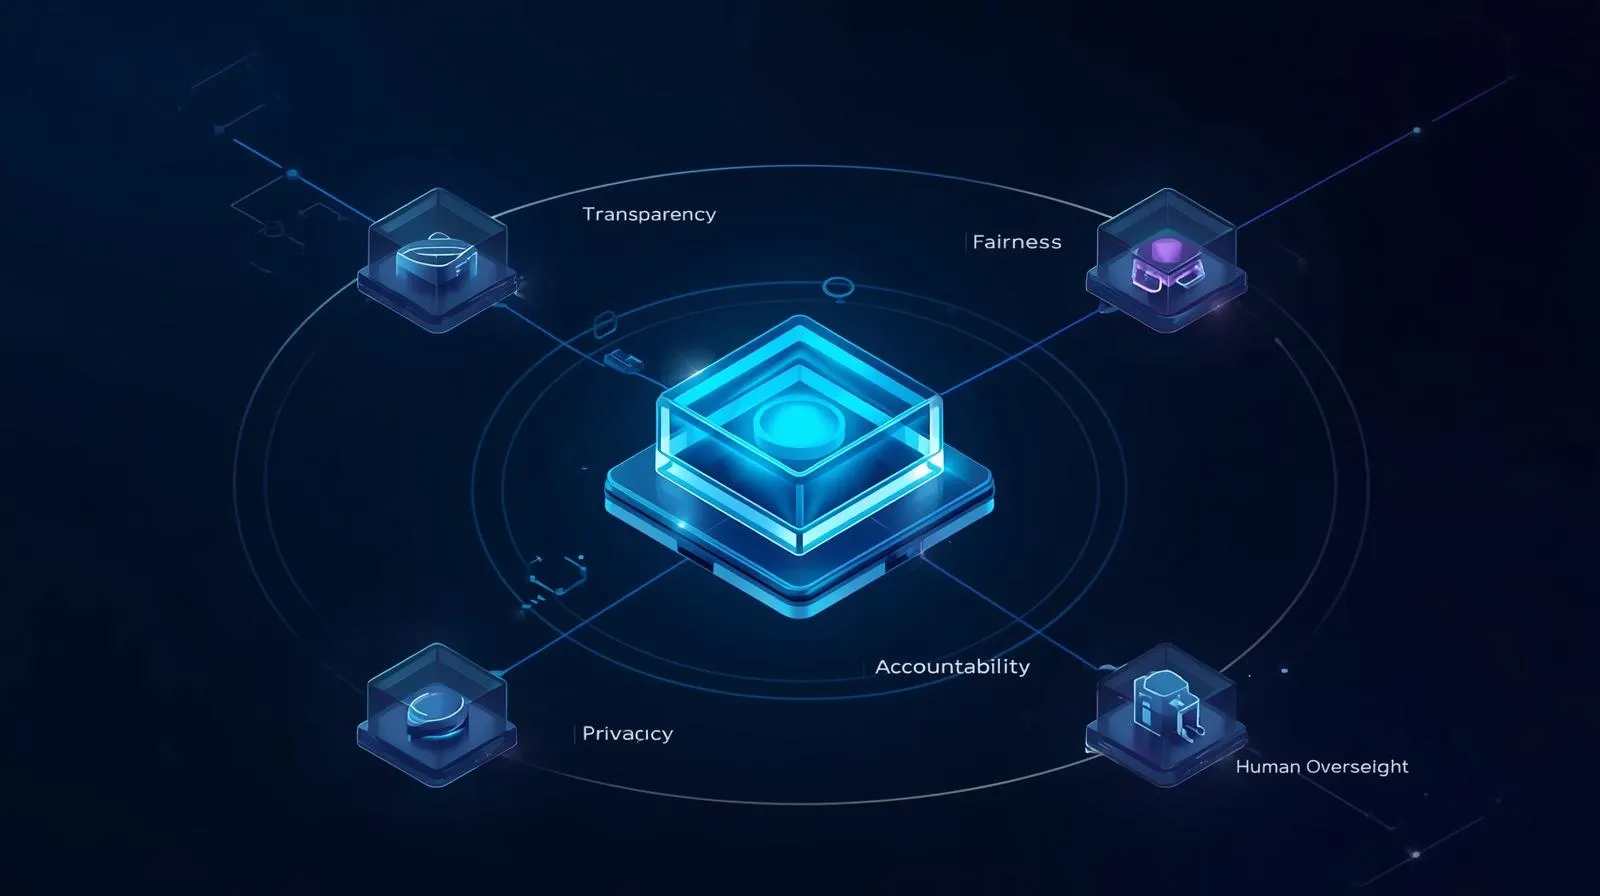
AI governance frameworks are guided by a set of principles that help organisations use AI responsibly while managing potential risks.
But defining these principles is only half the challenge enforcing them across multiple models, APIs, and teams requires a unified infrastructure.
That’s where TrueFoundry’s AI Gateway comes in. Acting as the enforcement layer of governance, it embeds these principles directly into the AI stack through centralized routing, access control, observability, and guardrails. Below are the core principles of AI governance — and how TrueFoundry makes each one operational in real-world enterprise environments.
Accountability means clearly defining who is responsible for an AI system throughout its lifecycle. Organisations need to know who can access models, who oversees their use, and who is responsible when something goes wrong.
TrueFoundry supports this through role-based access controls, identity-aware policies, and audit logs that provide greater visibility into AI usage.
Transparency and explainability help organisations understand how AI systems are being used and, where appropriate, why they produce particular outputs. Documentation and traceability are important here.
TrueFoundry’s Gateway makes this possible through end-to-end traceability and unified logging. Every request and response - including prompt, latency, token usage, and model version — flows through the Gateway, creating a single, explainable audit trail.
This central visibility simplifies compliance audits and support model comparison, performance analysis, and explainability reporting all within one dashboard.
Fairness focuses on identifying and reducing bias or discriminatory outcomes in AI systems. Governance processes can help teams test models, identify potential risks, and apply consistent policies.
TrueFoundry enables this through policy-based routing and programmable guardrails. Queries can be automatically directed to validated or bias-tested models, while the Gateway can flag or filter outputs that violate fairness constraints. This ensures consistent, organization-wide enforcement of fairness standards — across models, business units, and regions.
Privacy requires organisations to protect personal and sensitive information throughout the AI lifecycle. This includes controlling who can access data and how it is processed or shared.
TrueFoundry’s Gateway acts as a secure boundary between applications and model providers — encrypting all traffic, masking personally identifiable information (PII), and enforcing token-level access policies.
By funneling all model traffic through this governed perimeter, organizations achieve compliance with GDPR, CCPA, and data residency laws automatically, without rewriting application code or managing fragmented connectors.
Security and safety cover risks such as unauthorised access, misuse, attacks, and unexpected model behaviour. Governance therefore needs appropriate access controls, monitoring, safeguards, and testing.
TrueFoundry brings several of these controls together through features such as authentication, access management, rate limiting, observability, and guardrails.
Human oversight ensures that people remain involved when AI outputs or actions could have significant consequences. Depending on the use case, this may involve reviewing an output, approving an action, or stepping in when a defined risk is detected.
TrueFoundry supports this through human-in-the-loop workflows and configurable controls that allow selected interactions to be reviewed. For example, it can automatically flag high-risk or policy-sensitive outputs for manual review before returning them to end users ensuring that human oversight is embedded directly into runtime, not bolted on afterward.
Together, these principles provide the foundation for responsible AI governance. Platforms such as TrueFoundry can help organisations move from defining these principles on paper to applying them consistently across the AI stack.
AI can create new opportunities for organisations, but wider adoption also brings challenges around risk, compliance, data, and accountability. An AI governance framework gives teams a repeatable way to identify risks, assign responsibilities, apply controls, and review AI systems throughout their lifecycle.
It can help organisations:
When governance policies are applied through a central AI Gateway, organisations can make them more consistent across models, applications, and teams. This can lead to several practical outcomes:
Ultimately, AI gateways like TrueFoundry’s turn governance from a static framework into a living, programmable system - one where compliance, ethics, and transparency are built into every API call. It transforms AI from a technical initiative into a responsible enterprise capability, empowering innovation that’s as secure and compliant as it is intelligent.
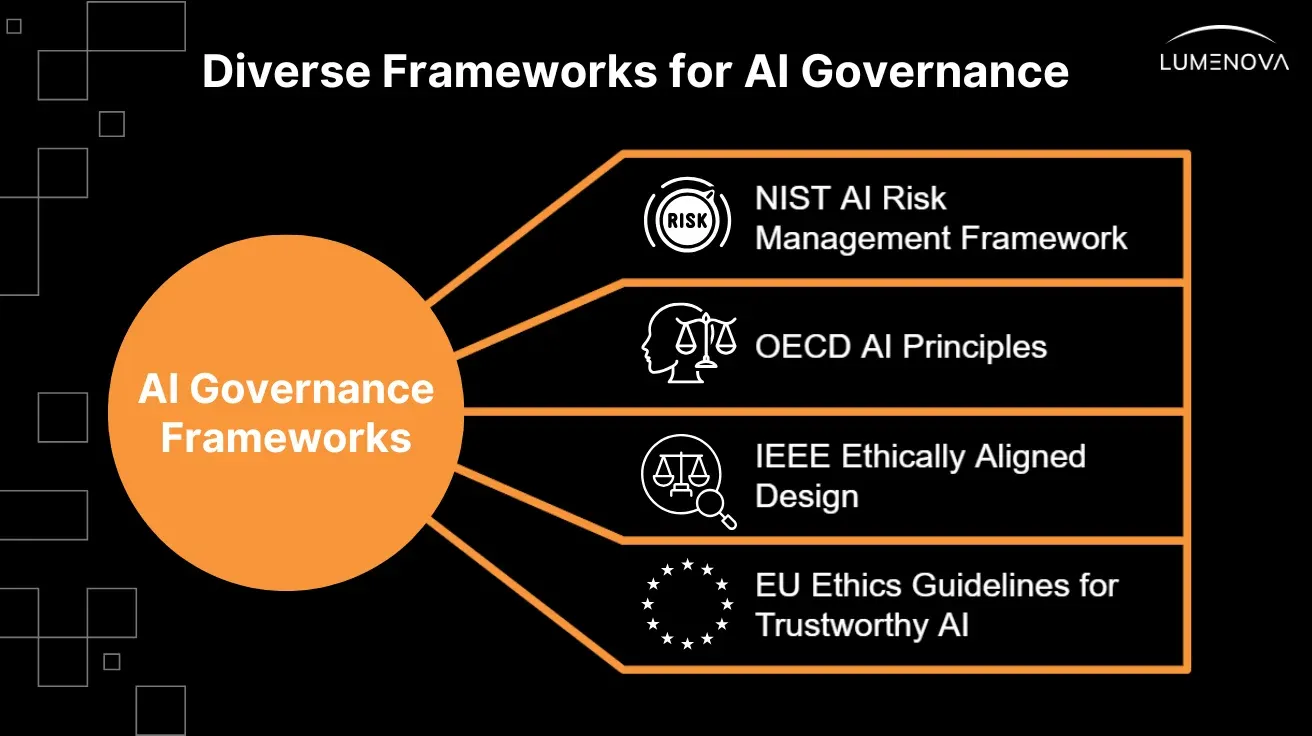
AI governance frameworks serve different purposes, from managing risks and setting organisational standards to establishing legal requirements. Here are the key frameworks and approaches to know in 2026.
As artificial intelligence scales globally, a growing number of frameworks are emerging to help organizations govern it responsibly. These frameworks combine ethical, technical, and legal principles to ensure AI remains trustworthy and compliant. Below are five of the most influential AI governance frameworks shaping enterprise strategy in 2026.
NIST AI Framework overview:
The NIST AI Risk Management Framework (AI RMF) is a voluntary framework that helps organisations identify, assess, and manage AI risks. It is built around four functions: Govern, Map, Measure, and Manage.
In simple terms, NIST helps you understand what could go wrong with an AI system, how serious the risk may be, and what you can do about it.
NIST has also expanded its guidance for newer AI technologies. Its Generative AI Profile, released in 2024, focuses on risks associated with generative AI. NIST is also working on updates to the AI RMF, so organisations using it should keep an eye on the latest guidance.
ISO/IEC 42001 Overview:
ISO/IEC 42001:2023 is an international standard for creating and maintaining an Artificial Intelligence Management System (AIMS). It helps organisations establish processes for managing AI responsibly across the business.
Unlike NIST AI RMF, which focuses on managing AI risks, ISO/IEC 42001 takes a broader management-system approach. It helps organisations put policies, processes, responsibilities, and continual improvement practices around their AI activities.
It is worth noting that ISO/IEC 42001 is not new in 2026. It was published in 2023. More recently, ISO/IEC 42006:2025 established requirements for organisations that audit and certify AI management systems against ISO/IEC 42001.
EU AI Act Overview:
The EU AI Act is different from the frameworks above because it is law, not voluntary guidance. It uses a risk-based approach, with requirements depending on how an AI system is classified and used.
Some provisions are already applicable, including rules covering prohibited AI practices, AI literacy, general-purpose AI, and transparency. The implementation timeline for certain high-risk AI requirements has also been adjusted as part of the EU's 2026 Digital Omnibus changes.
If your organisation develops, provides, deploys, or uses AI that falls within the Act's scope, the relevant legal requirements need to be considered alongside any voluntary governance framework.
OECD AI Principles Overview:
Adopted by over 47 countries and jurisdictions, the OECD AI Principles provide broad international guidance for developing and using trustworthy AI. They cover areas such as fairness, transparency, explainability, robustness, security, and accountability.
Unlike the EU AI Act, the OECD Principles are not a law that organisations must automatically comply with. They provide a common set of principles that governments and organisations can use when developing their own AI policies and governance approaches.
The principles were updated in 2024, and the OECD has continued adding practical guidance. Its Due Diligence Guidance for Responsible AI, published in 2026, provides organisations with a more practical approach to identifying and addressing potential AI-related impacts.
UK Pro-innovator AI Framework Overview:
The UK's approach to AI regulation is different from the EU's. Rather than relying on one comprehensive AI law, the UK has used a pro-innovation framework based largely on existing regulators and sector-specific rules.
The framework is built around five principles covering safety and security, transparency and explainability, fairness, accountability and governance, and contestability and redress.
In practice, this means that organisations need to consider the rules and guidance issued by the regulator relevant to their particular sector and AI use case. The UK's approach continues to evolve as new legislation and regulatory guidance are introduced.
Signed in 2025, the Executive Order 14179 titled “Removing Barriers to American Leadership in Artificial Intelligence” sets national priorities for AI development and oversight.
Together, these frameworks form the global foundation for AI governance. They provide organizations with practical, ethical, and regulatory guidance to balance innovation with accountability in 2025 and beyond. While these frameworks define global standards, organizations still need technical systems that can implement them consistently. AI Gateways act as that enforcement layer, translating policy into action through centralized governance, monitoring, and auditing.
Together, these frameworks form the global foundation for AI governance. They provide organizations with practical, ethical, and regulatory guidance to balance innovation with accountability in 2026 and beyond.
Selecting the right AI governance structure determines how effectively your organization can manage risk, compliance, and innovation at scale. But governance cannot remain a static document or committee; it must live within the AI infrastructure itself.
This is where AI Gateways redefine governance. Acting as the programmable control plane for your enterprise AI ecosystem, a gateway unifies access, security, observability, and compliance across every model and provider. It enforces the rules your governance framework defines—automatically, consistently, and audibly.
A strong governance structure combines three pillars: leadership ownership, process design, and infrastructure enforcement. Below is how AI Gateways enable each.
Governance starts with accountability. Form an AI Governance Council or Ethics Committee that defines enterprise-wide AI principles, risk thresholds, and compliance standards.
The AI Gateway becomes the council’s technical enforcement layer—translating those policies into runtime rules. For example, when leadership sets “PII must never leave EU data centers,” the gateway enforces that through region-aware routing and data residency policies without additional engineering work.
Clear ownership across the AI lifecycle prevents governance gaps.
With a Gateway in place, access roles can be tied directly to responsibilities—developers, auditors, and business units can each have scoped permissions and rate limits. Every model invocation is automatically linked to a user identity and logged, turning accountability into an operational metric, not a compliance checklist.
Traditional governance models rely on manual reviews; AI Gateways automate them.
Gateways sit between your applications and AI providers, applying guardrails, content filters, and bias detection policies in real time. This integration ensures that compliance is not an afterthought in deployment pipelines but a built-in stage of every AI workflow.
For example, before a model response is returned, the Gateway can check it against approved formats, remove sensitive data, and tag logs for audits—all transparently to end users.
Governance demands visibility. Gateways provide centralized observability aggregating model metrics, token usage, latency, and error rates across providers.
Through one dashboard, risk officers and engineering teams can monitor model performance, policy violations, or anomalous usage patterns. This turns governance from static documentation into a real-time monitoring system.
TrueFoundry’s AI Gateway, for instance, enables fine-grained policy control, unified logging, and cost tracking per user or team ensuring operational oversight without friction.
Not all AI systems carry the same risk profile. Gateways help automate risk stratification by tagging each model or endpoint with its risk level, routing high-risk tasks through stricter policies (such as content moderation or human validation).
This dynamic routing ensures resources and oversight are concentrated where accountability matters most without slowing down lower-risk innovation.
Governance must evolve as your models and regulations do. Gateways enable continuous feedback loops by capturing metrics and logs that inform audits, bias reviews, and retraining triggers.
When combined with leadership oversight, this creates a closed governance loop:
policy → enforcement → observation → improvement.
By aligning leadership intent with a gateway-based enforcement layer, enterprises can move beyond checkbox governance.
They gain a living system that enforces rules automatically, adapts to change, and proves compliance through data. TrueFoundry’s AI Gateway transforms governance from a reactive control mechanism into an intelligent, scalable framework where every AI call is secure, explainable, and policy-compliant by default.
Putting AI governance into practice becomes harder as organisations move from a few controlled experiments to multiple models, applications, teams and autonomous agents. The main challenges include:
These challenges are difficult to manage when governance depends on separate policies, manual reviews and disconnected tools. An AI governance platform can bring these controls closer to the infrastructure where AI is actually being used.
AI systems don’t stand still. They learn, retrain, and evolve continuously often faster than traditional governance models can adapt. As data changes and models self-improve, static checklists and manual reviews are no longer enough.
Modern governance must be dynamic, data-driven, and enforced at runtime. That’s precisely where TrueFoundry’s AI Gateway transforms governance from a static framework into a living system.
Adaptive governance starts with visibility. TrueFoundry’s AI Gateway provides real-time observability across every model, tool, and API.
Every interaction- prompt, response, latency, token count, or error passes through the gateway, creating a continuous audit trail. This allows compliance teams to detect drift, bias, or abnormal behavior as it happens, not months later during an audit.
By making model behavior observable, the gateway turns governance into an always-on monitoring system.
AI policies shouldn’t depend on human intervention to stay compliant. TrueFoundry’s Gateway enforces them automatically at the API layer.
It can dynamically route queries based on risk, geography, or sensitivity- for instance:
These routing rules make governance adaptive: the infrastructure itself responds to regulatory and operational changes without halting innovation.
Static frameworks fail when every update requires re-architecture. TrueFoundry’s Gateway enables modular governance, where each control (security, privacy, content moderation, cost tracking) can evolve independently.
Need to update your data retention policy or compliance region? Adjust the Gateway’s configuration- not your application code.
This modularity allows organizations to evolve governance continuously, as new regulations or internal policies emerge.
Automation ensures speed, but responsible governance needs human judgment. The Gateway enables human-in-the-loop workflows- automatically flagging high-risk outputs or policy violations for manual review.
For example, if a model generates sensitive or non-compliant content, the Gateway can pause the response, tag it for review, and log the event for future retraining.
This feedback mechanism blends human oversight with automated guardrails, ensuring governance stays both efficient and ethical.
Governance doesn’t end at enforcement- it improves with data.
Through unified logs and observability dashboards, TrueFoundry’s AI Gateway provides insights into usage patterns, model accuracy, and compliance metrics. These insights help refine routing policies, update fairness checks, and improve guardrail configurations.
In other words, the Gateway itself becomes the feedback engine that drives better governance decisions.
Regulatory expectations are changing rapidly- from the EU AI Act to sector-specific AI codes of conduct. With TrueFoundry’s Gateway, governance frameworks can adapt instantly through configuration updates rather than system overhauls.
When compliance zones shift or new standards arise, you can adjust routing, audit, and retention policies in minutes- ensuring governance scales as fast as innovation.
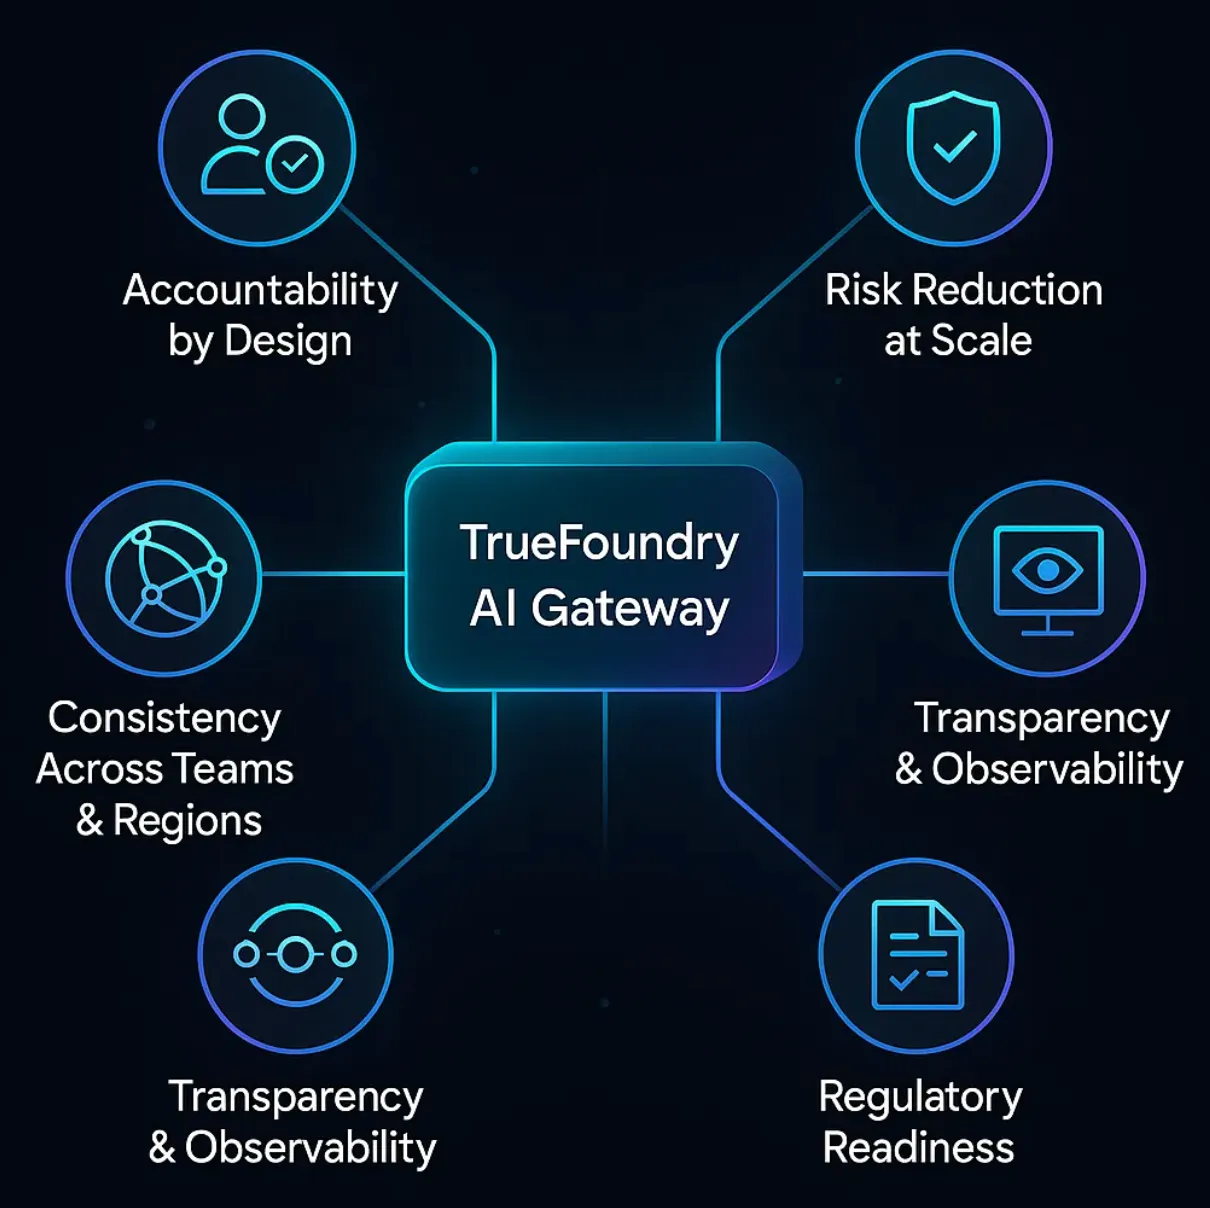
Accountability by Design: Every model call passes through the Gateway, which tags it with user identity, timestamp, and metadata. This creates a complete audit trail for regulators and internal reviews, making ownership visible and provable.
Risk Reduction at Scale: The Gateway applies guardrails, content filters, and data privacy policies automatically. It can block non-compliant requests, enforce rate limits, and redact sensitive information before it ever leaves your environment.
Consistency Across Teams and Regions: TrueFoundry’s centralized interface ensures all teams from R&D to production use standardized model APIs, prompt templates, and schemas. Centralized policies can be applied across supported models, providers, teams, and environments.
Transparency and Observability: With unified logs and dashboards, the Gateway provides real-time visibility into which models are being used, how they perform, and what data they touch, turning compliance from a periodic task into a continuous process.
Regulatory Readiness: As frameworks like the EU AI Act, NIST AI RMF, and ISO 42001 evolve, TrueFoundry’s AI Gateway allows enterprises to adapt instantly updating routing, access, or audit policies through configuration, not code.
AI governance is no longer just about creating policies. As organisations use more models, applications and AI providers, they need governance that can work consistently across this growing ecosystem.
TrueFoundry’s AI Gateway helps bring governance into the AI infrastructure with centralised access controls, monitoring and policy enforcement. This allows organisations to apply governance requirements more consistently while keeping visibility across AI usage.
With frameworks such as the NIST AI RMF, ISO/IEC 42001 and the EU AI Act shaping responsible AI practices, organisations need an approach that can adapt as their AI systems and requirements change. Building governance into the infrastructure can make AI adoption more controlled, transparent and accountable.
See how TrueFoundry can help you operationalize AI governance. Book a demo.
TrueFoundry AI Gateway delivers ~3–4 ms latency, handles 350+ RPS on 1 vCPU, scales horizontally with ease, and is production-ready, while LiteLLM suffers from high latency, struggles beyond moderate RPS, lacks built-in scaling, and is best for light or prototype workloads.




AI governance focuses on the rules, roles, processes and controls used to manage AI. Responsible AI is broader and focuses on developing and using AI in ways that address concerns such as fairness, safety, transparency, privacy and accountability.
No. The NIST AI Risk Management Framework is voluntary. NIST created it to help organisations manage AI risks and improve trustworthiness across the design, development, deployment and use of AI systems.
NIST AI RMF is a voluntary framework for identifying and managing AI risks. ISO/IEC 42001 is an international standard that specifies requirements for establishing and continually improving an AI Management System (AIMS).
The EU AI Act does not simply require every organisation to adopt one specific AI governance framework. Instead, it establishes legal requirements based on factors such as AI system risk, with obligations for providers and users covered by the Act.
AI governance is usually a shared responsibility. Leadership sets direction, while teams such as legal, security, compliance, IT, data and AI development may manage different controls. Clear ownership helps ensure risks are identified and addressed.
There is no single review schedule that applies to every organisation. Reviews should happen regularly and whenever major changes occur, such as introducing a new model, changing an AI use case, discovering a risk or facing new regulatory requirements.



The latest news, articles, and resources sent to your inbox