


Erhalten Sie sofortigen Zugriff auf eine TrueFoundry-Live-Umgebung. Stellen Sie Modelle bereit, leiten Sie den LLM-Verkehr weiter und erkunden Sie die gesamte Plattform — Ihre Sandbox ist in Sekundenschnelle einsatzbereit, ohne dass eine Kreditkarte erforderlich ist.


What Is Prompt Injection and How Does It Work?

Steuern, implementieren und verfolgen Sie KI in Ihrer eigenen Infrastruktur
Frequently Asked Questions
What is prompt injection in simple terms?
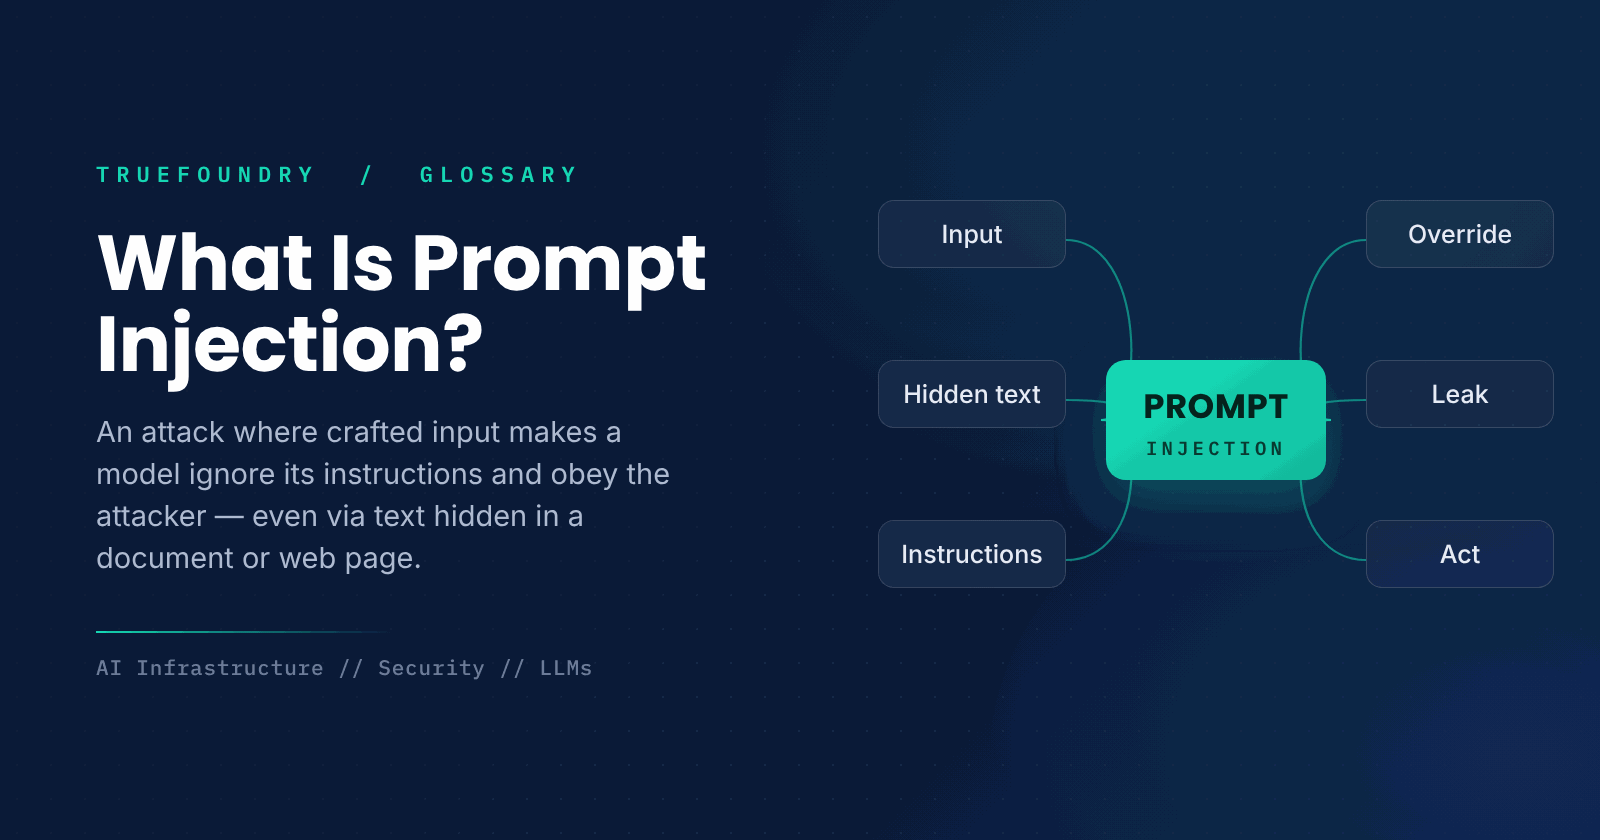
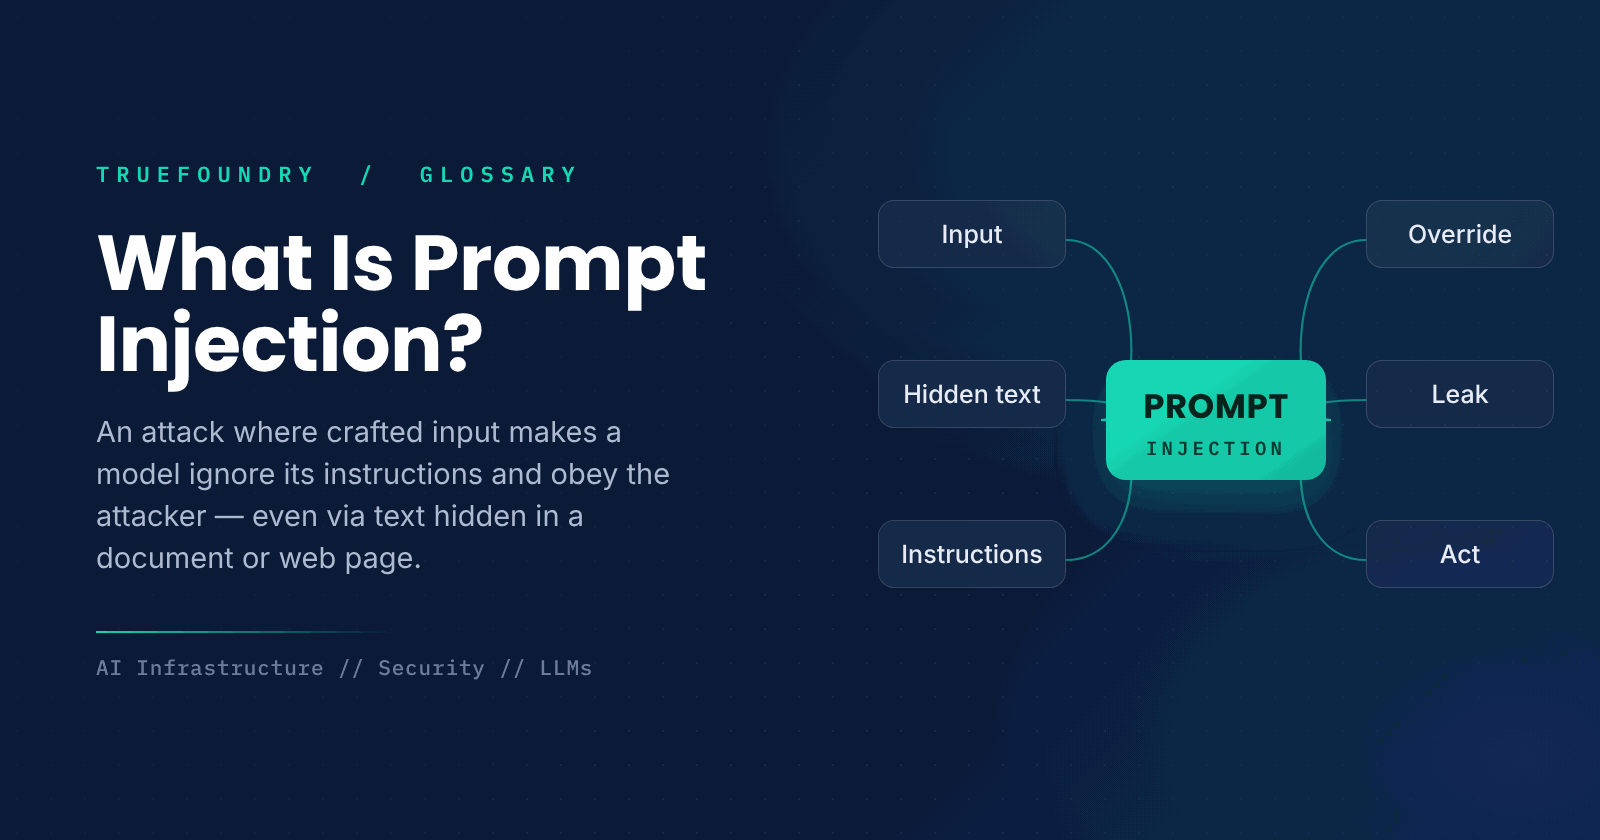
It is fooling a language model into disregarding its instructions by giving it text that tells it to do something else. Since the model follows instructions in its input, such malicious text can hijack what it does.
What is the difference between direct and indirect prompt injection?
A direct injection is when an attacker types malicious instructions straight into the prompt. An indirect injection is where the malicious instructions are embedded in content the model reads, such as a web page or document, so a third party attacks through data the model consumes.
Why is prompt injection hard to prevent?
A model cannot distinguish a trusted instruction from untrusted data, because both are just text within its context. There is no clean boundary to enforce, so injection cannot be fully eliminated, only reduced with layered defenses.
What is the difference between prompt injection and jailbreaking?
Prompt injection overrides an application's instructions by feeding it crafted input. Jailbreaking is an effort to circumvent the safety guidelines built into a model. They overlap, since a jailbreak can be delivered via injection, but injection is the broader category.
How do you defend against prompt injection?
With layered defenses: give the model the least access to tools and data, treat external content as untrusted, add input and output guardrails, require human approval for high-impact actions, and test against known attacks. No single measure is enough on its own.

GenAI infra- einfach, schneller, günstiger
Top-Teams vertrauen uns bei der Skalierung von GenAI

- © 2022 ENSEMBLE Technologies



Abonnieren Sie unseren Newsletter
Die neuesten Nachrichten, Artikel und Ressourcen werden in Ihren Posteingang gesendet


