November 1, 2026
|
5 min read


Obtenha acesso instantâneo a um ambiente TrueFoundry ao vivo. Implante modelos, direcione o tráfego de LLM e explore a plataforma completa — seu sandbox estará pronto em segundos, sem necessidade de cartão de crédito.



Blazingly fast way to build, track and deploy your models!
Enterprise IAM was built for humans and service accounts. Agents are neither: they act for a user, across several tools, often in chains. If your identity provider has no agent-identity capability — or you simply don't want to depend on one yet — you are left with the three bad options every agent deployment starts with: borrow the user's token, share a service account, or impersonate. All three break the audit trail, as we cover in what AI agent identity is.
The identity-broker pattern lets you skip the wait. One trusted component becomes the issuer and authority for agent identity, so you get governed agents today and keep the option to federate with your IdP later.
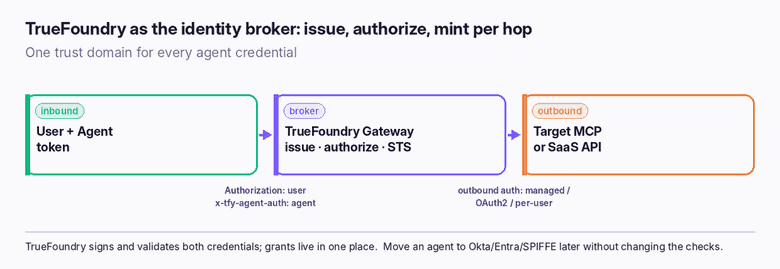
A broker takes on three roles that would otherwise be spread across your IdP, your app code, and each tool. With TrueFoundry as the broker, they map like this:
Registration creates the agent's identity. The agent gets its token from the registry (via ⋮ → Get Token) and sends it with the user's token on every call:
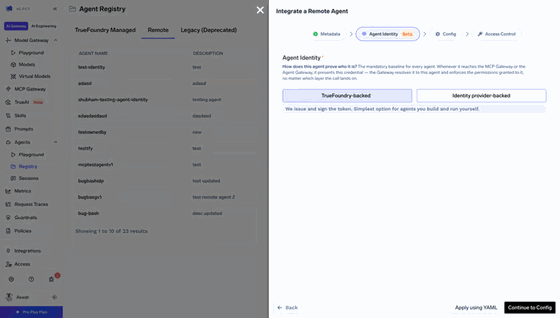
Registering an agent. The broker scenario uses a TrueFoundry-backed identity; you can switch an agent to an IdP later. Source: TrueFoundry docs.
Authorization: Bearer <USER_TOKEN>
x-tfy-agent-authorization: Bearer <AGENT_TOKEN>
The gateway validates both tokens, checks whether the agent may reach the target MCP server and whether it may act for the user, then forwards the request using the target's outbound auth. Anything not granted is denied with a 403. Because TrueFoundry signs and validates both credentials, the gateway is the single trust domain — there is no external exchange to stand up.
The broker also solves outbound credentials, which is where most agent integrations actually stall. It offers three outbound modes depending on what the target supports:
TrueFoundry AI Gateway delivers ~3–4 ms latency, handles 350+ RPS on 1 vCPU, scales horizontally with ease, and is production-ready, while LiteLLM suffers from high latency, struggles beyond moderate RPS, lacks built-in scaling, and is best for light or prototype workloads.



A component that takes on the agent control-plane roles your IdP and app code otherwise would: issuing each agent's identity, authorizing every call, and minting scoped credentials for each hop. In TrueFoundry the gateway is the broker, and it signs and validates the agent token itself.
When your IdP has no agent-identity capability, when you want governed agents quickly, or when your agents are in-house and their targets are internal or reachable with gateway-held credentials. If policy requires every principal in the corporate directory, use an IdP-backed scenario instead.
No. Your enterprise IdP still authenticates human users. The broker only provides and governs agent identity, carrying the user's token alongside the agent's on every call.
Through outbound auth on the MCP server: no auth or a managed header for internal targets, OAuth2 client credentials for app-to-app SaaS, or per-user OAuth (authorization code) when the SaaS needs per-user consent. The gateway stores and refreshes per-user tokens.
Yes. Only the source of the agent's identity changes; the collaborator grants, authorization checks, and audit trail stay the same. You can mix broker-backed and IdP-backed agents in one tenant.
The gateway denies it with a 403 that names the refused principal and the reason — whether the agent lacked access to the target or lacked permission to act for that user.



As últimas notícias, artigos e recursos enviados para sua caixa de entrada