

Collibra is per-tenant: the MCP server URL and every OAuth2 endpoint are specific to your Collibra instance. Collibra also does not support Dynamic Client Registration (DCR), so you must bring your own OAuth client. There is no registration URL and no scopes to configure.
Using Collibra through the MCP Gateway
The TrueFoundry MCP Gateway centralizes access to Collibra - agents connect through one endpoint instead of maintaining separate server configurations per client. When you use Collibra MCP server through the AI Gateway, TrueFoundry provides:- Authentication - Clients authenticate inbound to the AI Gateway with a Personal Access Token, Virtual Account, or IDE OAuth flow. For outbound access, the AI Gateway runs the OAuth2 Authorization Code flow with PKCE (
S256) so each user authorizes their own Collibra account and operates under their own Collibra permissions; tokens are stored, refreshed and injected per user on tool calls. - Access control - Collaborators and role-based policies define who can use the server and which tools they can invoke. Enable or disable individual Collibra tools from the server detail page, or use a Virtual MCP Server to expose only read tools when agents should only read catalog context.
- Observability - Tool calls are traced with caller identity, tool name, inputs, and latency. Monitor server- and tool-level usage in MCP Metrics and export traces to your observability stack via OpenTelemetry.
- Guardrails - Apply pre-tool and post-tool guardrails on MCP tool calls.
Prerequisites
- A TrueFoundry account with permission to add MCP servers, and your TrueFoundry control-plane base URL (used to build the OAuth callback).
- A Collibra instance, and permission to create a user application (OAuth2 client) in it.
- Your Collibra instance URL, for example
https://<your-company>.collibra.com.
Collibra Endpoints
All endpoints use your Collibra instance URL as the base:
Replace
<instance-url> with your Collibra host, for example your-company.collibra.com. Use the same host in all three URLs.
Create a User Application in Collibra
1
Create the user application
In your Collibra instance, create a user application (an OAuth2 client) for TrueFoundry.
2
Register the TrueFoundry redirect URI
Add TrueFoundry’s OAuth callback URL to the user application’s allowed redirect URIs:Replace
<tfy-control-plane-base-url> with your TrueFoundry control-plane host.3
Copy the client credentials
Copy the generated Client ID and Client Secret. You’ll enter them in TrueFoundry in the next section.
Adding Collibra MCP server to TrueFoundry
1
Open the MCP Server catalog
Navigate to MCP Servers in the TrueFoundry sidebar and click Add new MCP Server. On the next screen, select Connect Official Remote MCP Servers - this opens the catalog of pre-vetted servers with auth already templated.
2
Search for and select Collibra
Collibra is available in the official remote MCP server catalogue. In the catalogue search, type “collibra” and click the collibra card.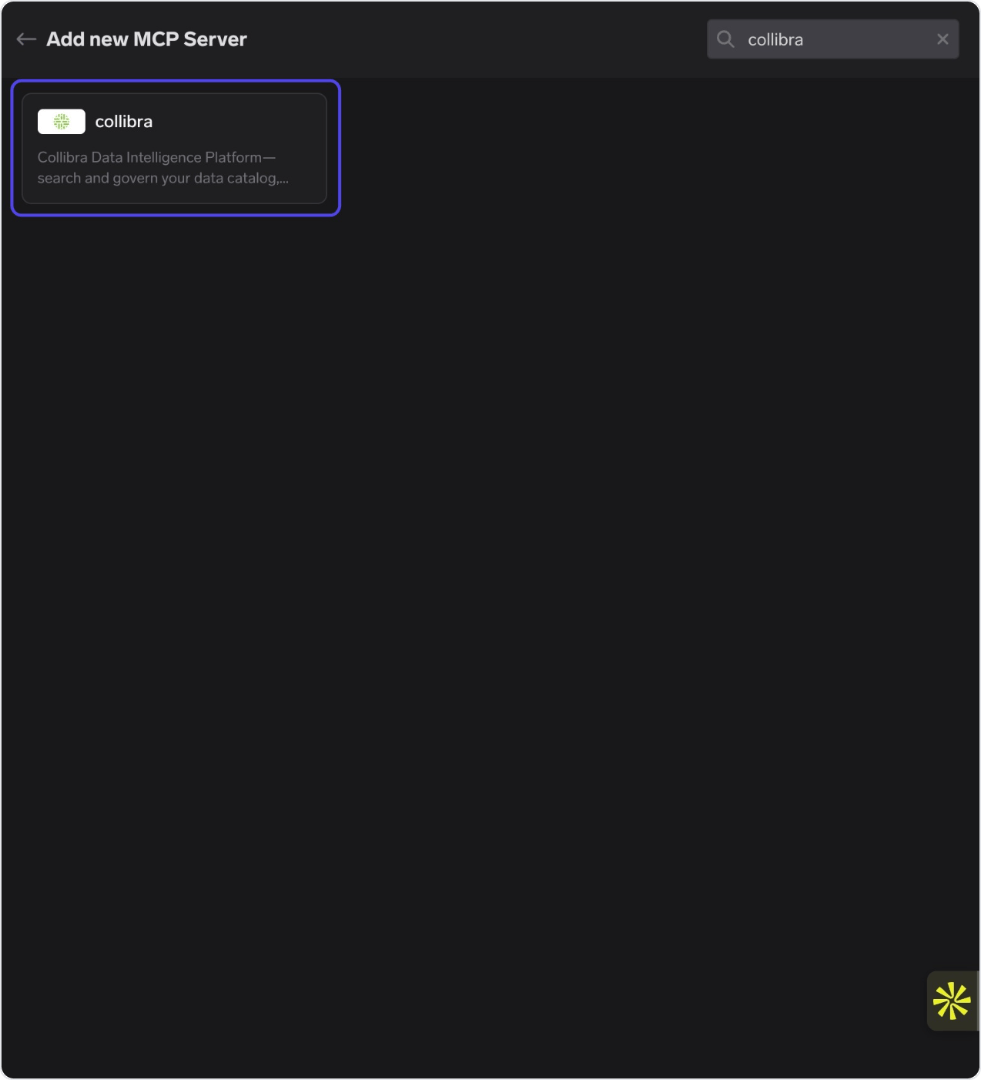
3
Fill in server details
TrueFoundry pre-fills the Name, Description, and URL fields. Replace
{{YOUR_INSTANCE}} in the URL with your Collibra host so it reads https://<instance-url>/rest/mcp. Add yourself or your team under Collaborators with the MCP Server Manager role.4
Configure OAuth2
Select OAuth2 with grant type Authorization Code and fill in the fields:
- Authorization URL:
https://<instance-url>/oauth/v2/authorize - Token URL:
https://<instance-url>/oauth/v2/token - Client ID / Client Secret: the values from your Collibra user application
- Code Challenge Methods Supported:
S256(PKCE is required) - JWT Source: Access Token
5
Authenticate
Save the MCP Server, then open the server’s Tools tab and click Connect Now. You’ll be redirected to Collibra to sign in and authorize access.
6
Verify tools
After authorizing, the Tools tab lists Collibra’s available tools. Click Try on any tool to invoke it through the TrueFoundry MCP Gateway and inspect the JSON output before using it in an agent.
Connecting to an MCP Client
Open the How To Use tab on the Collibra server detail page for your tenant-specific Gateway URL and ready-to-paste client snippets - don’t build the endpoint manually. The tab includes snippets for Claude Code, VS Code, Claude Web, Claude Desktop, Cursor, Windsurf, Codex, and the Python and TypeScript MCP SDKs. Use Show API Key if your client requires a Gateway token in a header.Using the Tool Playground
Before deploying an agent, you can test any Collibra MCP server tool directly in TrueFoundry:1
Open a tool
On the Collibra MCP server detail page, click Try next to any tool.
2
Fill in the inputs
Enter the tool’s input parameters, for example a search term for your data catalog.
3
Execute and inspect
Click Execute Tool and inspect the JSON output in the right panel.
Tool Metrics
The Tool Metrics tab on the Collibra server detail page tracks how agents use each tool:- Invocation count - which tools are called most often
- Latency - how long each tool takes to respond
- Error rates - which tools are failing in production
Disabling Individual Tools
On the Tools tab, toggle off any Collibra tools your agents don’t need:- Disabled tools are hidden from MCP clients and cannot be invoked.
- Enabled tools remain available to agents as usual.