



October 27, 2026
|
5 min read



Blazingly fast way to build, track and deploy your models!
An autonomous agent that holds a static API key or OAuth client secret has the same problem every service account has, only worse: the credential outlives the need for it, it gets copied into images and config files, and anyone — or any prompt-injected tool call — that reads it can impersonate the agent. The more agents and the more instances, the more copies of long-lived secrets you are tracking.
SPIFFE flips the model. Instead of presenting a secret to prove identity, a workload is attested by its environment and handed a fresh, short-lived credential bound to a stable identity. There is no static token to steal, and every running instance gets its own attested credential. This is the same shift from secrets to identity we describe for agents in general in what AI agent identity is.
SPIRE issues an SVID only after two attestation checks pass:
Only a workload that matches a registered entry on an attested node receives an SVID. The SVID comes in three shapes, and the practical fit for gateway calls today is the JWT-SVID:
The acme.com portion of the SPIFFE ID is the trust domain. On Kubernetes, SPIRE trusts projected service account tokens and the agent reads its JWT-SVID from the SPIFFE Workload API at runtime — so no secret is ever written to a config file or baked into an image.
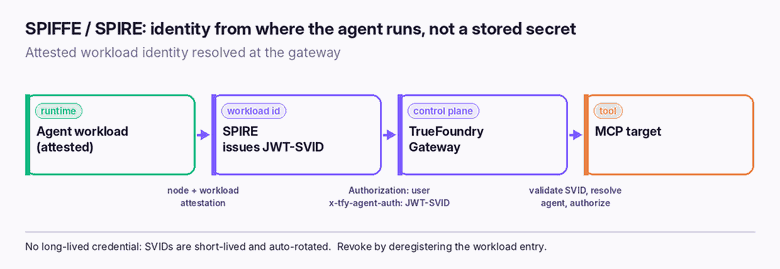
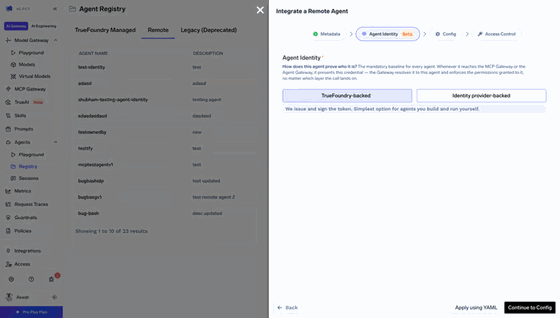
To TrueFoundry, a JWT-SVID is just another identity-provider token. The agent is registered as identity-provider-backed — the same registration step every externally-issued agent identity uses:
Each request then carries two tokens, exactly as in standard agent identity and on-behalf-of delegation:
Authorization: Bearer <USER_TOKEN>
x-tfy-agent-authorization: Bearer <JWT-SVID>
The gateway validates the SVID against SPIRE's JWKS, resolves the SPIFFE ID to the registered agent, checks whether that agent may reach the target and may act for the user, and forwards the call with the target's own outbound auth. The user's identity travels alongside the agent's the whole way.
Three steps connect SPIRE to the gateway:
Access itself is still governed by collaborator grants — who may invoke the agent, whom it may act for, and which MCP servers it may reach — the model covered in fine-grained authorization and what MCP authorization is.
Treating the SVID as a replacement for authorization. Attestation proves who the workload is; it does not decide what it may do. You still need collaborator grants and policy at the gateway — identity and authorization are separate layers.
Over-broad attestation selectors. If workload attestation keys only on a namespace, every pod in that namespace can obtain the same SVID. Pin selectors to the service account and image digest so the identity means one workload.
Forgetting the user. An SVID identifies the agent, not the person it acts for. The user's token must still travel in Authorization so the downstream system can answer whose data was touched.
Assuming mTLS alone is governance. X.509-SVIDs secure the transport, but a governed call still needs the gateway to resolve identity, authorize the pair, and audit it.
A platform team runs agents on Kubernetes and refuses to ship another long-lived token. They stand up SPIRE, register an entry for research-agent keyed on its service account and image digest, and expose SPIRE's OIDC endpoint. In TrueFoundry they add SPIRE as an identity provider and register research-agent as identity-provider-backed, mapping its SPIFFE ID. At runtime each pod pulls a JWT-SVID from the Workload API and sends it with the user's token to the gateway, which validates it against SPIRE's JWKS, resolves it to the registered agent, and authorizes the call. When a workload is decommissioned, they deregister its entry and the SVIDs simply stop at the next rotation — no secret to revoke, no config to clean up.
To see why attested identity matters, put it next to the two things teams reach for first. The difference is not cosmetic — it changes who can impersonate the agent and how fast you can shut a compromised one down.
The static key and the shared account share one flaw: the credential is a bearer secret, so possession is identity. SPIFFE breaks that equation — possession of an SVID is worthless without passing attestation on an attested node, and the SVID expires on its own within minutes. There is nothing durable to steal.
The docs describe the end-to-end model as a stack of four layers, each solving one problem, which is worth making explicit because it shows where SPIFFE stops and the gateway starts:
It is called portable because the stable agent identity is derived from attestation, not from a cloud-specific secret — so the same identity holds whether the workload runs on one cluster today and another tomorrow. Layer one is pure SPIFFE/SPIRE; layers two to four are where the TrueFoundry Gateway does its work.
Kubernetes is the common case, and it is where the "no secret on disk" claim becomes real. SPIRE trusts the cluster's projected service account tokens as node-and-workload evidence, and the agent reads its JWT-SVID from the SPIFFE Workload API — a local socket — at runtime. Nothing is written to a file, baked into an image, or passed as an environment variable, so there is no artifact for a leaked image or a prompt-injected cat to expose. When the SVID nears expiry, the SPIRE agent fetches a fresh one transparently, so a long-running agent never stalls on an expired credential. Pin workload attestation selectors to the service account and the container image digest, not just the namespace, so one SVID means exactly one workload rather than every pod in the namespace.
A stored secret is a liability that grows with every agent and every instance. SPIFFE and SPIRE replace it with identity that comes from attestation — short-lived, auto-rotated, and impossible to copy out of a config file. The TrueFoundry Gateway takes the SVID the agent earns at runtime, resolves it to a governed identity, and authorizes the call for the user it acts for.
The result is the thing security teams actually want from autonomous agents: an identity you can attest, authorize, audit, and revoke — without a single long-lived credential in sight.
TrueFoundry AI Gateway delivers ~3–4 ms latency, handles 350+ RPS on 1 vCPU, scales horizontally with ease, and is production-ready, while LiteLLM suffers from high latency, struggles beyond moderate RPS, lacks built-in scaling, and is best for light or prototype workloads.




SPIFFE is an open standard for workload identity and SPIRE is its reference implementation. For AI agents, they issue a short-lived, attested credential (an SVID) based on where the agent runs, so the agent never holds a long-lived secret. TrueFoundry resolves that SVID to a registered agent identity and governs the call.
An SVID is a SPIFFE Verifiable Identity Document. It carries a SPIFFE ID such as spiffe://acme.com/ns/agents/sa/research-agent and comes as an X.509 certificate (for mTLS), a JWT (a bearer token for gateway calls), or a key-bound WIT-SVID. SPIRE issues it only to an attested workload and rotates it automatically.
The agent sends its JWT-SVID in the x-tfy-agent-authorization header and the user's token in Authorization. The gateway validates the SVID against SPIRE's JWKS, resolves the SPIFFE ID to the registered agent, checks the agent's grants and delegation, and forwards the call with the target's outbound auth.
Deregister the workload entry in SPIRE. Its instances stop receiving SVIDs at the next rotation, which acts as a per-instance kill switch. There is no long-lived credential to chase down.
No. SPIFFE proves identity; it does not decide what the agent may do. You still need collaborator grants and policy at the gateway to authorize which targets an agent may reach and which users it may act for.
Yes. TrueFoundry’s data plane runs in your VPC or on-prem, so DSPy’s prompts and optimization data stay in your environment.



The latest news, articles, and resources sent to your inbox
















