October 19, 2026
|
5 min read


احصل على وصول فوري إلى بيئة TrueFoundry مباشرة. انشر النماذج، ووجّه حركة مرور LLM، واستكشف المنصة بالكامل — بيئة الاختبار الخاصة بك جاهزة في ثوانٍ، ولا يلزم وجود بطاقة ائتمان.



Published: October 19, 2026

Blazingly fast way to build, track and deploy your models!
In a regulated environment, “can we use Claude?” is really three questions: where does the data go, who retains it, and can we prove it. Claude is usable under HIPAA, under strict data-residency rules, and under zero-retention requirements — but only if you pick the right access path and wire the controls around it. The capability is there; the work is in the configuration and the proof.
This post maps the compliant ways to run Claude, what each one gives you, and how a gateway lets you enforce residency, retention, and PII controls consistently across them. The Anthropic specifics below are from Anthropic’s privacy documentation on commercial data handling and HIPAA, as of October 2026; always re-confirm current terms.
The access path determines your data-handling posture, so it is the first decision, not an afterthought.
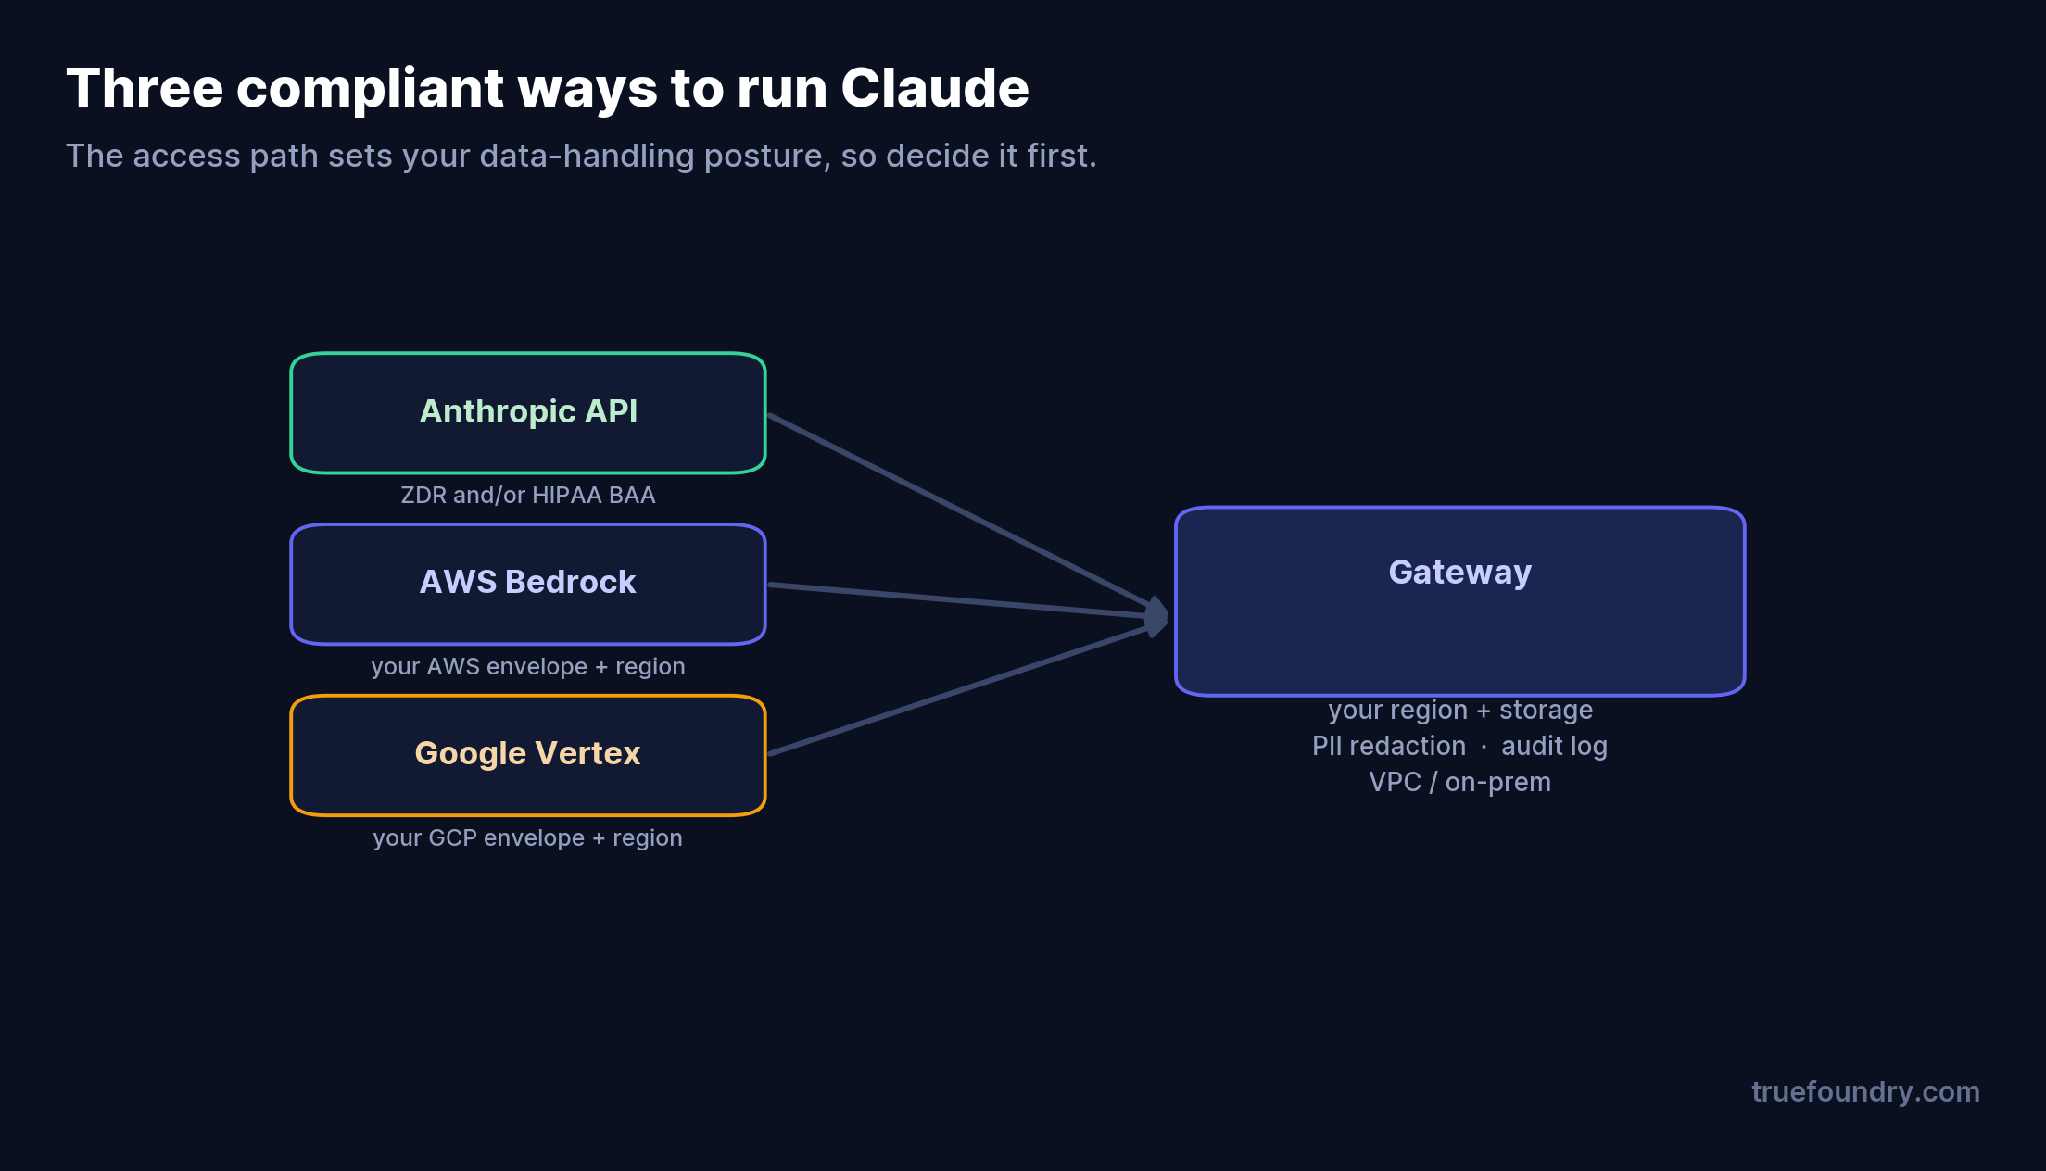
The Anthropic API, hardened. You can run directly against Anthropic with zero data retention and/or under a HIPAA BAA (more on both below). This is the most direct path and keeps you on Anthropic’s newest models immediately.
Claude on AWS Bedrock. Here Claude runs inside AWS, so the data-handling, region, and compliance posture are your AWS environment’s — the same envelope (and BAA) you already use for other regulated workloads on AWS.
Claude on Google Vertex. The same idea on Google Cloud: Claude runs inside your Vertex/GCP environment and region, under your existing GCP compliance arrangements.
Regulated teams often choose Bedrock or Vertex precisely because the data never leaves a cloud account and region they already have approved and under contract — the compliance question becomes “is our AWS/GCP usage compliant,” which they’ve usually already answered.
Two Anthropic mechanisms matter most in regulated settings, and they are often confused.
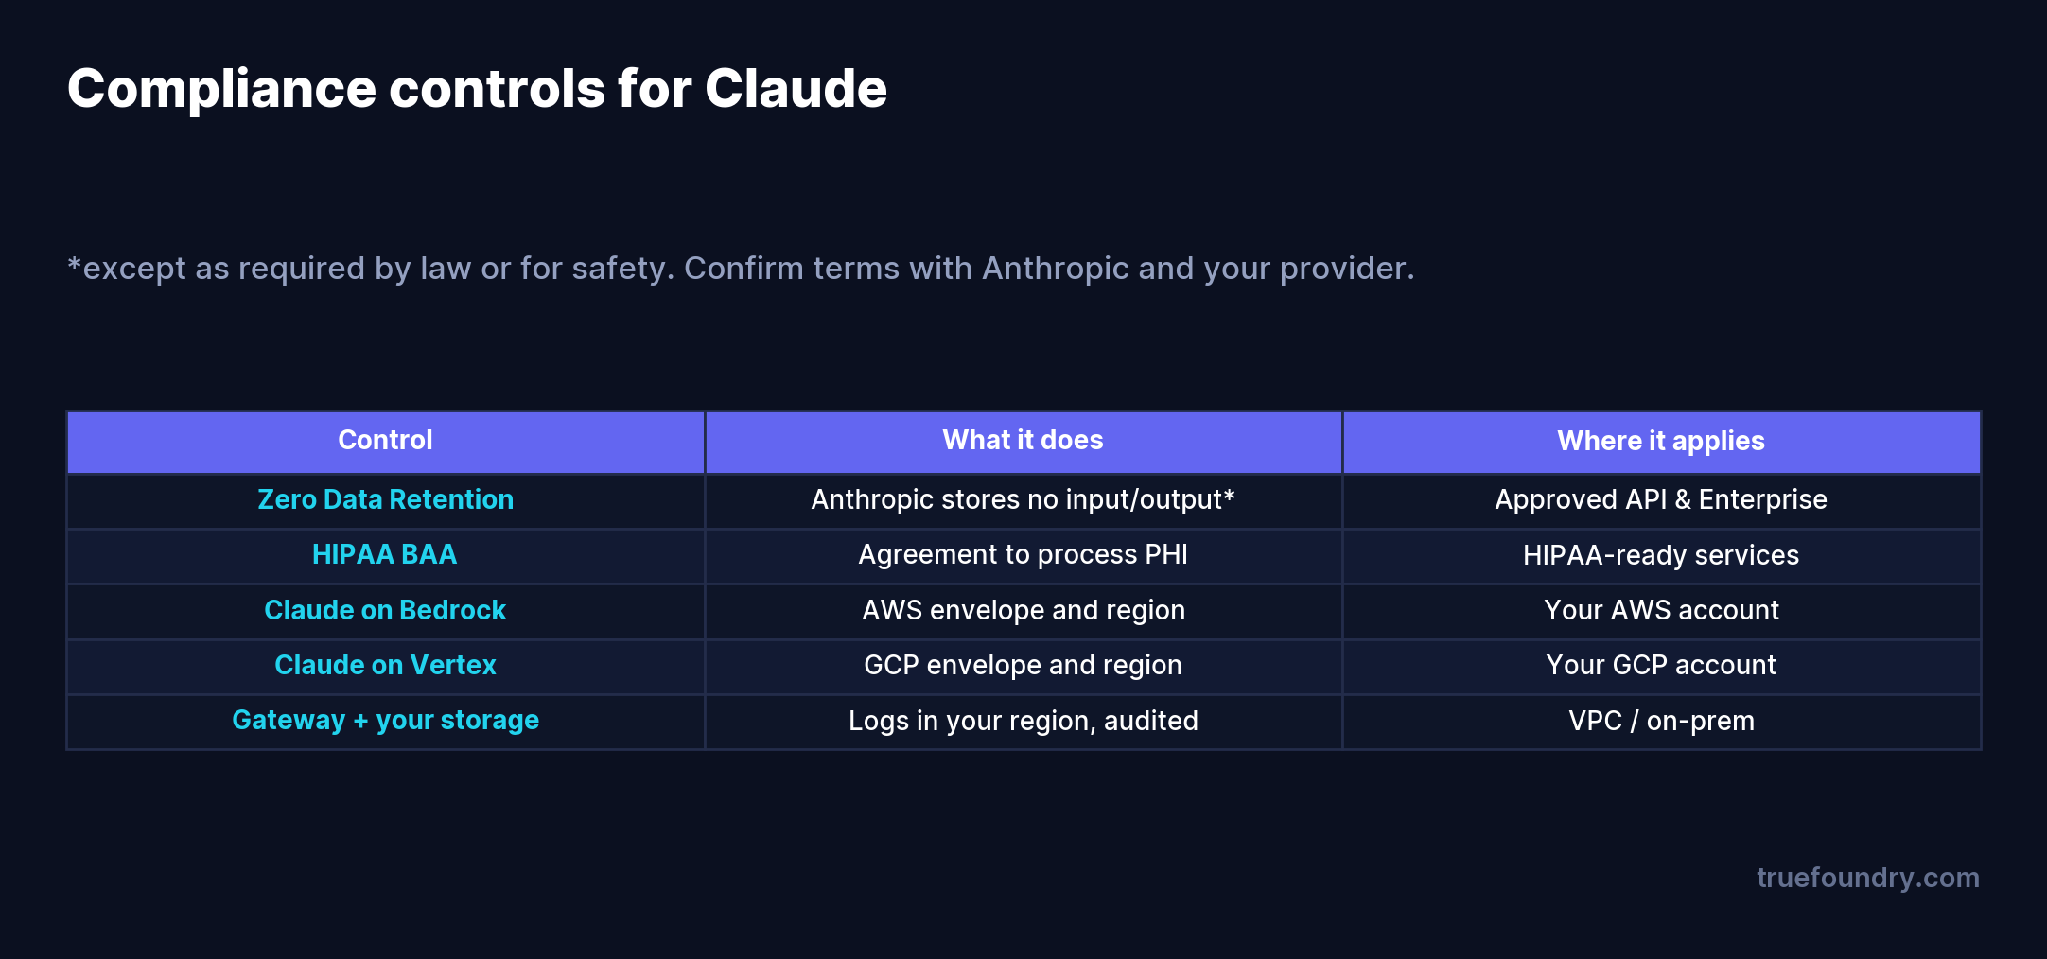
Zero Data Retention. Under an approved ZDR arrangement, Anthropic does not store your inputs or outputs except where needed to comply with law or to combat misuse — it still retains User Safety classifier results to enforce its Usage Policy. ZDR is available to approved Claude API and Enterprise customers, reviewed per organization. Platform users can check their status under Settings, Privacy Controls, Data retention period.
HIPAA BAA. A Business Associate Agreement is available for Anthropic’s HIPAA-ready services — the Claude API with HIPAA configuration enabled, and HIPAA-ready Enterprise plans — and, importantly, a BAA does not require ZDR. For Claude Code accessed via a Console API key, the BAA applies only when that organization has ZDR enabled. The exact features each BAA covers and the configuration each needs are listed in Anthropic’s BAA documentation.
The practical point: ZDR and a BAA are different controls for different requirements. If your rule is “the vendor must not retain our data,” that’s ZDR. If your rule is “we need a signed BAA to process PHI,” that’s the HIPAA path, which can run with or without ZDR. Some regulated teams want both; many need only one.
Choosing a compliant endpoint is necessary but not sufficient — you also have to control where request data is stored and prove what happened. That is the layer a gateway adds, regardless of which Claude path you pick.
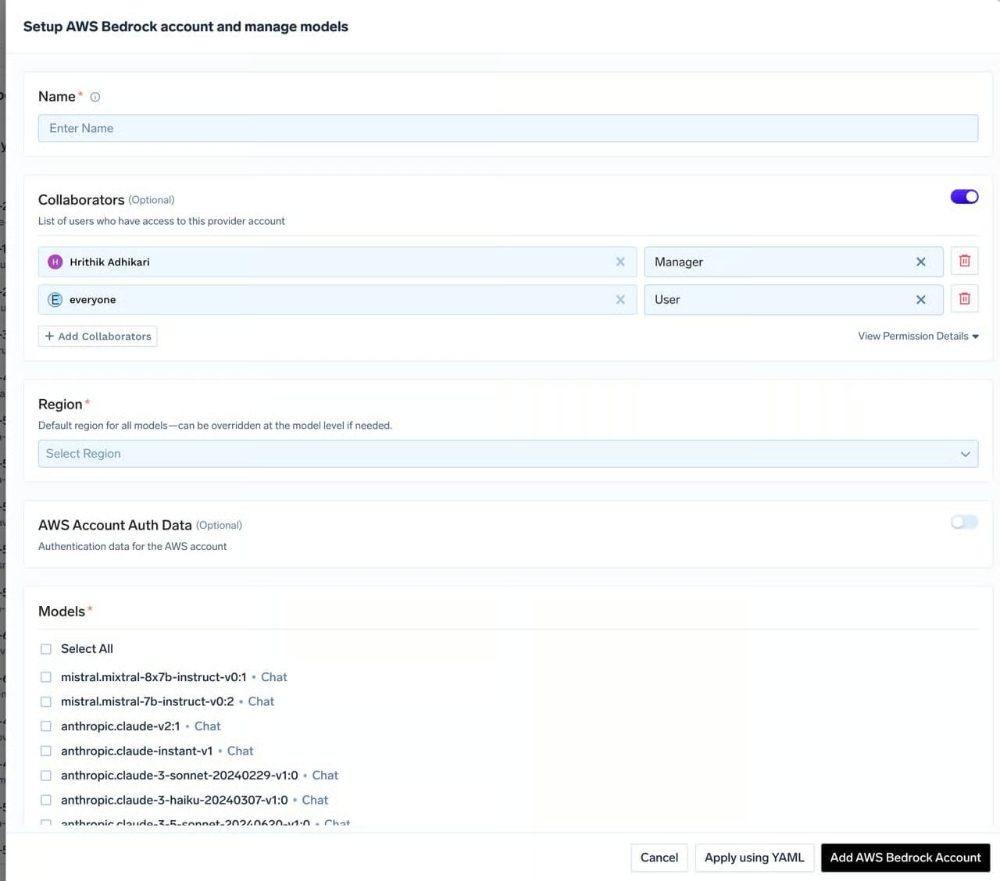
Routed through the TrueFoundry AI Gateway, Claude traffic can be configured so request and response data is stored in your own blob storage and region, the control plane never sits in the live request path (in hybrid and self-hosted deployments), and every call is logged for audit — the proof regulators ask for. You pick the Bedrock region (and per-model overrides), authenticate with an assumed IAM role or key rather than long-lived root credentials, and address Claude through a logical name so the underlying endpoint can change without touching applications.
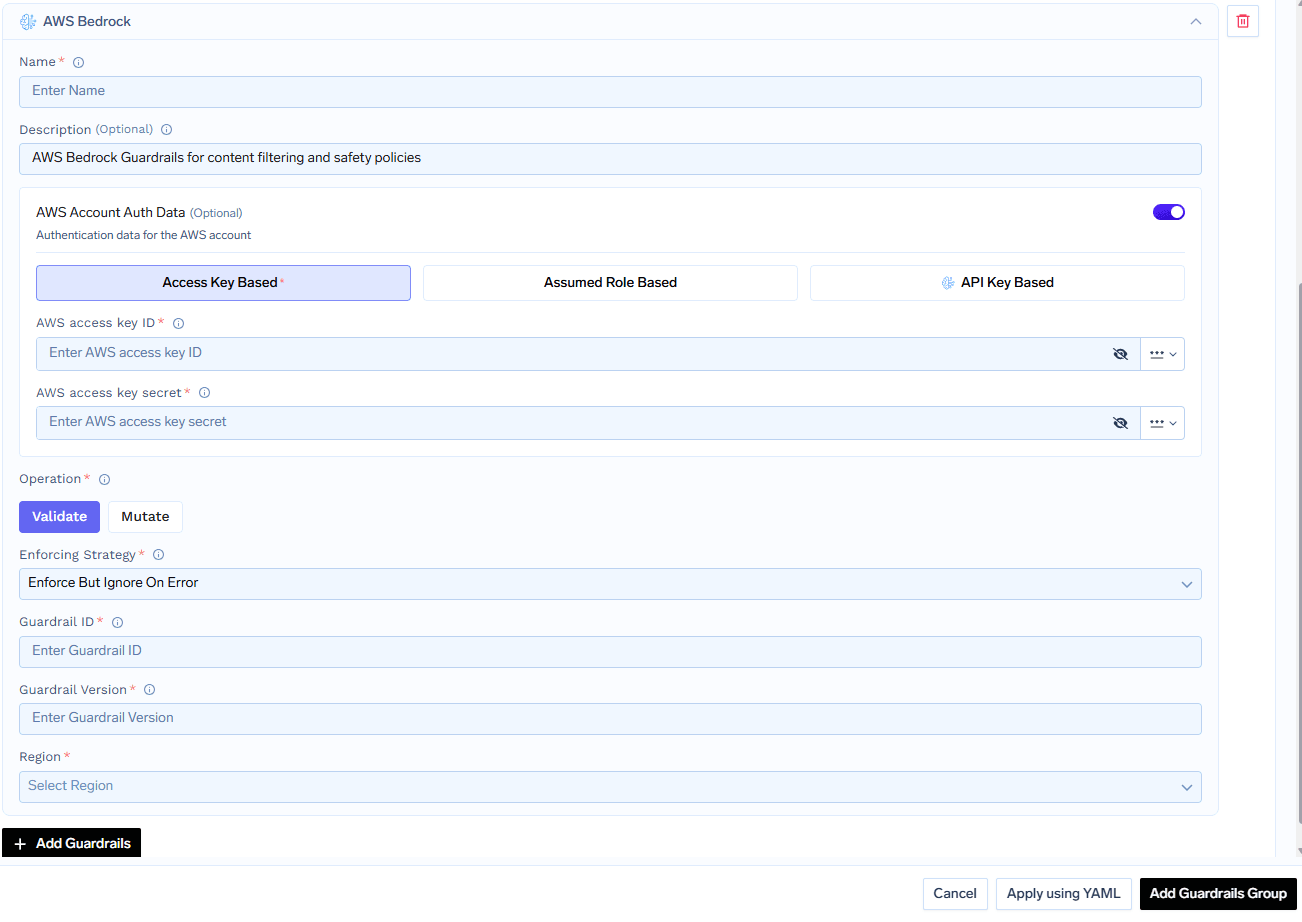
Region and least-privilege authentication for Claude on Bedrock. Source: TrueFoundry docs.
And because the gateway deploys as SaaS, in your VPC, on-prem, or air-gapped, you can put the whole data plane inside your own network when residency or sovereignty rules demand it — so LLM traffic and request data never leave your environment at all.
Compliance is not only about retention and region; it is also about what you send in the first place. A support prompt that carries a patient name or an account number into any provider is a problem no BAA fully neutralizes. The gateway is the place to catch it: a PII guardrail can redact sensitive fields on the way in (and in tool results) before the request reaches Claude, Bedrock, or Vertex, so the raw identifier never leaves your boundary. Pair that with the retention and region choices above and you have defense in depth rather than a single contractual control.
They conflate ZDR and a BAA. They’re different controls. ZDR is about Anthropic not storing data; a BAA is the HIPAA agreement to process PHI, and it doesn’t require ZDR. Pick for your actual rule.
They assume the API path is the only one. For residency or an existing cloud BAA, Bedrock or Vertex keeps Claude inside a cloud account and region you’ve already cleared.
They forget where request logs live. A compliant model endpoint doesn’t help if request data lands in a third party’s storage. Keep logs in your own bucket and region.
They rely on contracts instead of controls. A BAA doesn’t stop a prompt from carrying PII. Redact at the gateway so sensitive data never leaves your boundary.
TrueFoundry AI Gateway delivers ~3–4 ms latency, handles 350+ RPS on 1 vCPU, scales horizontally with ease, and is production-ready, while LiteLLM suffers from high latency, struggles beyond moderate RPS, lacks built-in scaling, and is best for light or prototype workloads.



Anthropic offers a HIPAA BAA for its HIPAA-ready services (the Claude API with HIPAA configuration enabled, and HIPAA-ready Enterprise plans); a BAA doesn’t require ZDR. Running Claude on AWS Bedrock or Google Vertex places it under your cloud provider’s compliance envelope. Confirm scope with Anthropic, the provider, and your compliance team.
Under an approved ZDR arrangement, Anthropic doesn’t store your inputs or outputs except as required by law or for safety enforcement (it still keeps safety classifier results). It’s available to approved Claude API and Enterprise customers.
Yes — via AWS Bedrock or Google Vertex you choose the region, and a gateway lets you set it (with per-model overrides) and keep request data in your own regional storage.
Not necessarily — a BAA and ZDR are separate. A BAA can run with standard retention; ZDR is the control that removes storage. Choose based on whether your requirement is “no retention” or “signed BAA to process PHI.”
Apply a PII guardrail at the gateway that redacts sensitive fields on input and in tool results before the request reaches the model, so raw identifiers never leave your environment.



أحدث الأخبار والمقالات والموارد تصلك مباشرة إلى بريدك الوارد