

Choose a path
External JWT
Okta, Entra, Auth0, or a custom OIDC IdP. Send the IdP JWT as
Authorization: Bearer on every call.Workload Identity Federation
Kubernetes, GitHub Actions, AWS, or GCP. Exchange the platform JWT for a short-lived TrueFoundry token.
Where to configure
Go to Settings > Security & Access > Identity Providers and add a provider. Use the External JWT form for corporate IdPs, or pick Kubernetes, GitHub, AWS, or GCP for workload federation.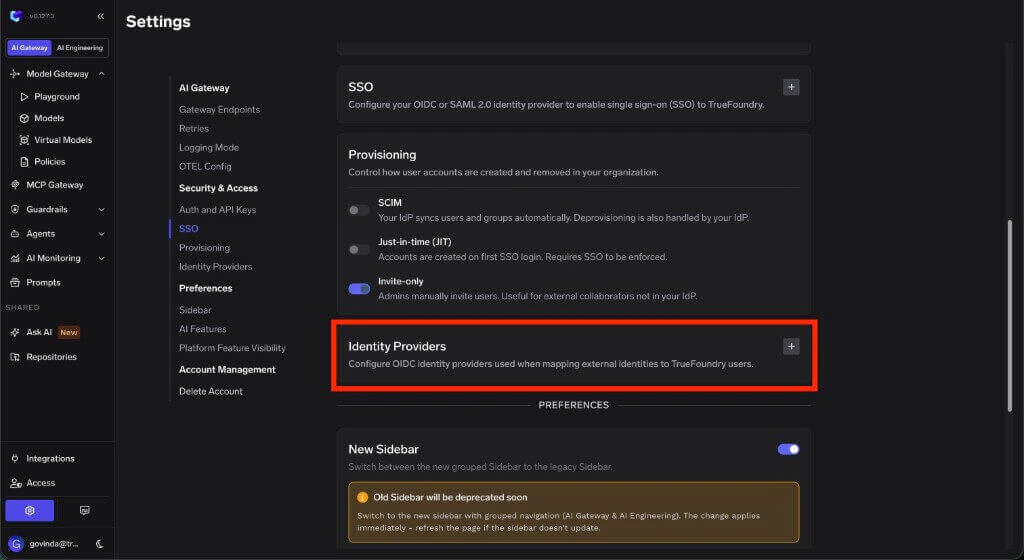
Identity Providers section in Security & Access settings
Related
- External JWT — field reference, Resolve Token To, gateway examples
- Workload Identity Federation — exchange API and provider guides
- Virtual Account mappings
- SSO & SCIM — interactive login and user provisioning